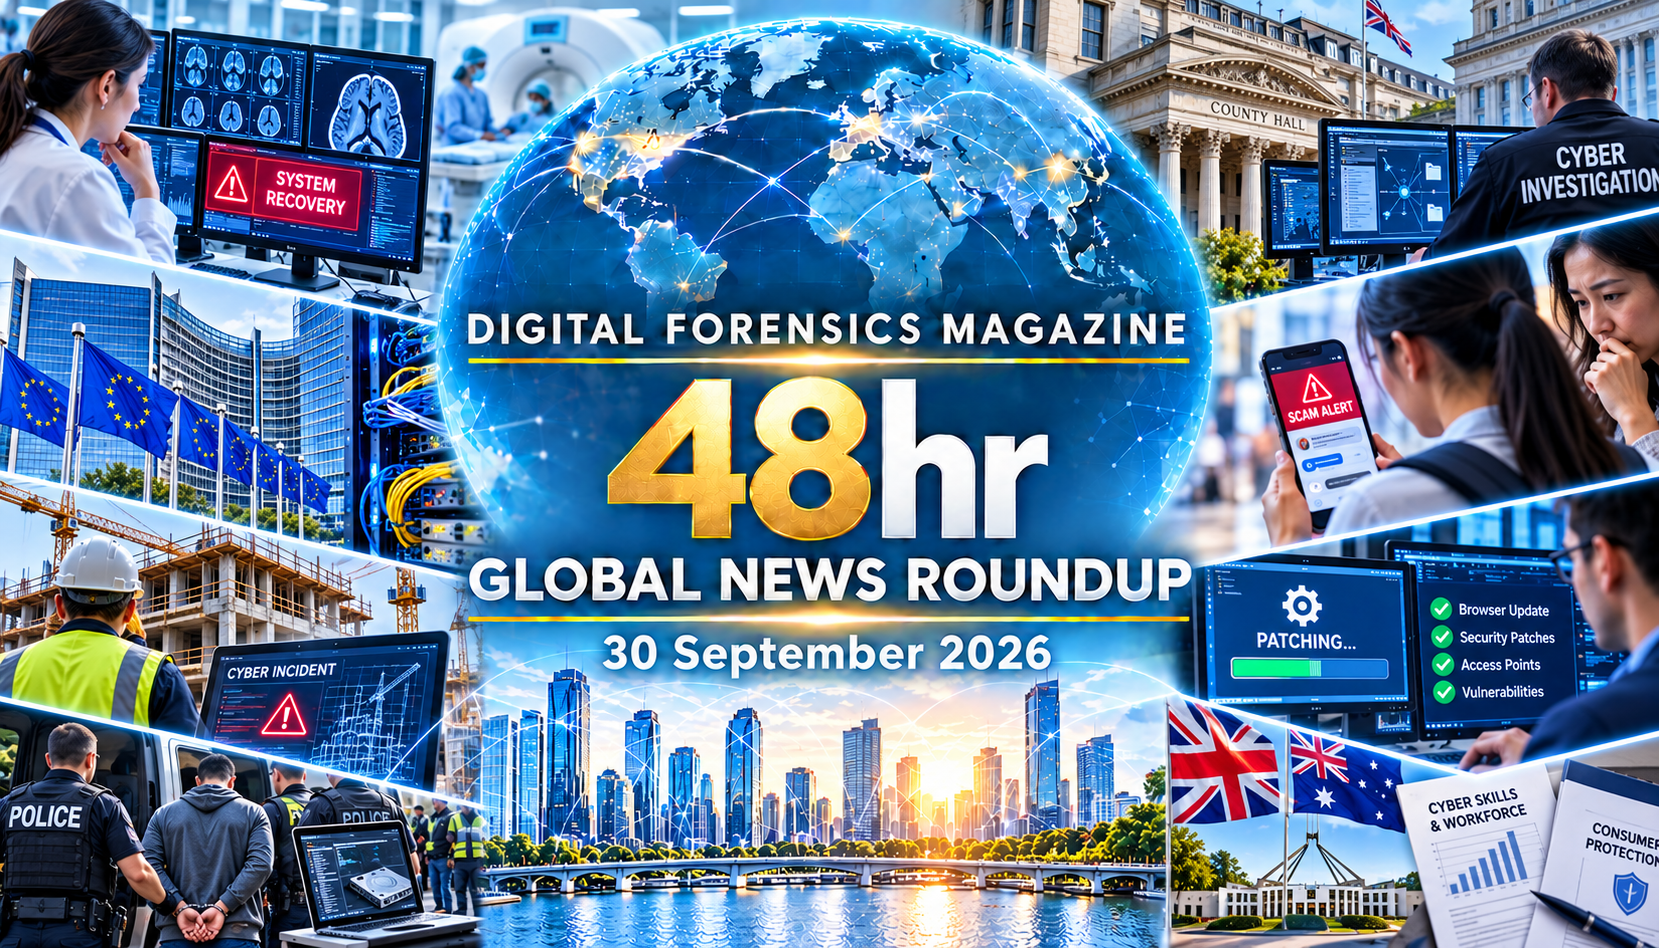

What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
Fraudulent SIM supply chain traced
Banking evidence links fraud network
→Cyber Investigations
California subpoenas OpenAI
TA419 targets AI policy experts
→Major Cyber Incidents
Hattiesburg Eye confirms file acquisition
Queensland discloses supplier-linked loss
→Exploits & Threat Intelligence
TeamViewer fixes five high-severity flaws
TP-Link patches Deco command injection
→Law Enforcement
KillSec suspect arrested in UK
Cyberstalking defendant arrested
→Policy & Standards
India modernises banking evidence law
UK data regulator governance changes
→Gurugram cyber police traced a mobile number used in a commercial fraud to a telecom point-of-sale agent in Kanpur, who was arrested on 30 September for allegedly misusing customers’ KYC documents and live photographs to activate additional SIM cards without their knowledge. Police say the investigation is now examining the wider supply chain and associates after the suspect allegedly supplied around 50 SIMs to cybercriminals.
Police in Chhattisgarh traced an interstate cyber-fraud network to West Bengal and arrested three suspects on 30 September after investigators linked complaints across multiple states through technical evidence and analysis of banking transactions. The district police said the alleged organiser had repeatedly changed location, making the correlation of transaction trails and other technical indicators central to identifying the suspects and connecting the network with reported fraud cases.
California’s Attorney General served OpenAI with an investigative subpoena as part of an ongoing state inquiry into cybersecurity incidents and risks associated with the company and its artificial-intelligence models. The California Department of Justice says the subpoena extends its examination beyond the previously announced Hugging Face incident, while the precise facts, responsibility and legal implications of the incidents under review remain subjects of the investigation rather than established findings.
Proofpoint reported that a threat actor it tracks as TA419 used impersonation and adversary-in-the-middle credential phishing against a small number of US artificial-intelligence policy experts at think tanks, universities and law firms. Proofpoint assesses the group as China-aligned and espionage-motivated, but that attribution remains the company’s assessment; the observed campaigns used fictitious policy invitations and multi-stage redirects intended to capture Microsoft 365 credentials.
Hattiesburg Eye Clinic in Mississippi disclosed that an August network disruption led investigators to conclude that an unauthorised third party may have acquired files containing information about current and former patients. The clinic said its review identified potentially affected data including names, Social Security numbers, telephone numbers and diagnoses or conditions, while reporting no known misuse and continuing notification, law-enforcement liaison and security-enhancement work.
Queensland’s Department of Customer Services, Open Data and Small and Family Business disclosed a material financial loss from a cyberattack involving unauthorised access to a third-party telecommunications provider during the 2025–26 financial year. The department said no government or sensitive data was compromised and that it contained and investigated the incident, engaged external support and strengthened security controls, illustrating the evidential importance of supplier-side access records when reconstructing losses.
ThaiCERT warned that TeamViewer had released fixes for five high-severity vulnerabilities affecting Full Client and Host software across Windows, Linux and macOS, including CVE-2026-92370, which can bypass session permission controls and enable command execution. The advisory says TeamViewer reported no public exploit or evidence of real-world exploitation, so investigators should distinguish vulnerable installations from confirmed compromise while checking versions, session artefacts and affected hosts for anomalous activity.
TP-Link published an advisory for CVE-2026-17176, an OS command-injection vulnerability affecting specified Deco BE11000 and Deco M9 Plus devices that can allow an adjacent-network attacker to execute arbitrary commands with root privileges using a crafted UDP packet. The vendor has issued fixed firmware and describes potential confidentiality, integrity and availability impacts, but the advisory does not establish that exploitation has occurred, making patch status and device telemetry important investigative evidence.
US prosecutors announced the arrest in the United Kingdom of Dutch national Fouad Eltibrizi, who is charged in Puerto Rico with offences including unauthorised computer access conspiracy and extortion-related conduct allegedly connected with the KillSec ransomware group. The indictment remains an allegation, while public coverage of the wider international operation reports additional arrests and infrastructure seizures; investigators are continuing to examine evidence obtained during the coordinated enforcement activity.
Federal authorities in Massachusetts arrested and charged John Anthony Proia III with cyberstalking after an indictment alleged repeated calls, texts and voicemails were sent from changing telephone numbers to a victim and members of her family. Court filings say Voice over Internet Protocol applications were used to generate numbers and obscure identity, making communications records, account attribution and provider data central to reconstructing the alleged contact pattern; the charge remains unproven.
India’s Bankers’ Books Evidence Act 2026 came into force on 1 October, replacing the 1891 legislation and creating a technology-neutral framework for admitting physical, electronic and digital banking records in legal proceedings, inquiries and investigations. The government says the Act standardises authentication and certification requirements and extends the concept of bankers’ books to contemporary digital records, strengthening the procedural basis on which investigators can obtain and present financial evidence.
The United Kingdom’s new Information Commission assumed the functions of the Information Commissioner’s Office on 30 September under governance reforms established by the Data (Use and Access) Act 2025. The government says the regulator’s existing data-protection and freedom-of-information powers continue unchanged, but the move replaces the previous corporation-sole structure with collective executive and non-executive governance, creating a new institutional framework for oversight of personal-data handling and breach accountability.
Editorial Perspective
Across this cycle, the strongest investigative signal is the need to preserve and correlate evidence beyond the immediately affected system. SIM-registration records, banking transactions, cloud-account activity, supplier access and communications metadata all show how attribution increasingly depends on linking artefacts held by different organisations and service providers. Investigative readiness therefore requires organisations to know which third parties hold relevant logs, how long those records are retained and how they can be obtained without losing temporal or evidential context. That becomes especially important when initial technical indicators identify infrastructure rather than the individual or organisation responsible.
The coverage also reinforces the distinction between evidence of vulnerability, evidence of access and evidence of consequential compromise. Advisories for TeamViewer and TP-Link describe exploitable conditions without establishing real-world exploitation, while breach disclosures from Hattiesburg Eye and Queensland provide bounded findings that should not be extended beyond what investigations have confirmed. Maintaining that separation improves evidential integrity and prevents preliminary claims, vendor assessments or allegations from becoming embedded as fact. For investigators, defensible conclusions depend on preserving provenance, recording uncertainty and revisiting earlier hypotheses as new technical, legal and cross-platform evidence emerges.
Reference Reading
- NIST SP 800-86 — Guide to Integrating Forensic Techniques into Incident Response
- NIST SP 800-61 Rev. 3 — Incident Response Recommendations and Considerations
- NIST — Cybersecurity Framework 2.0
- UK NCSC — Logging and protective monitoring
- CISA — Known Exploited Vulnerabilities Catalog
- ICO — Personal data breaches: a guide
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM