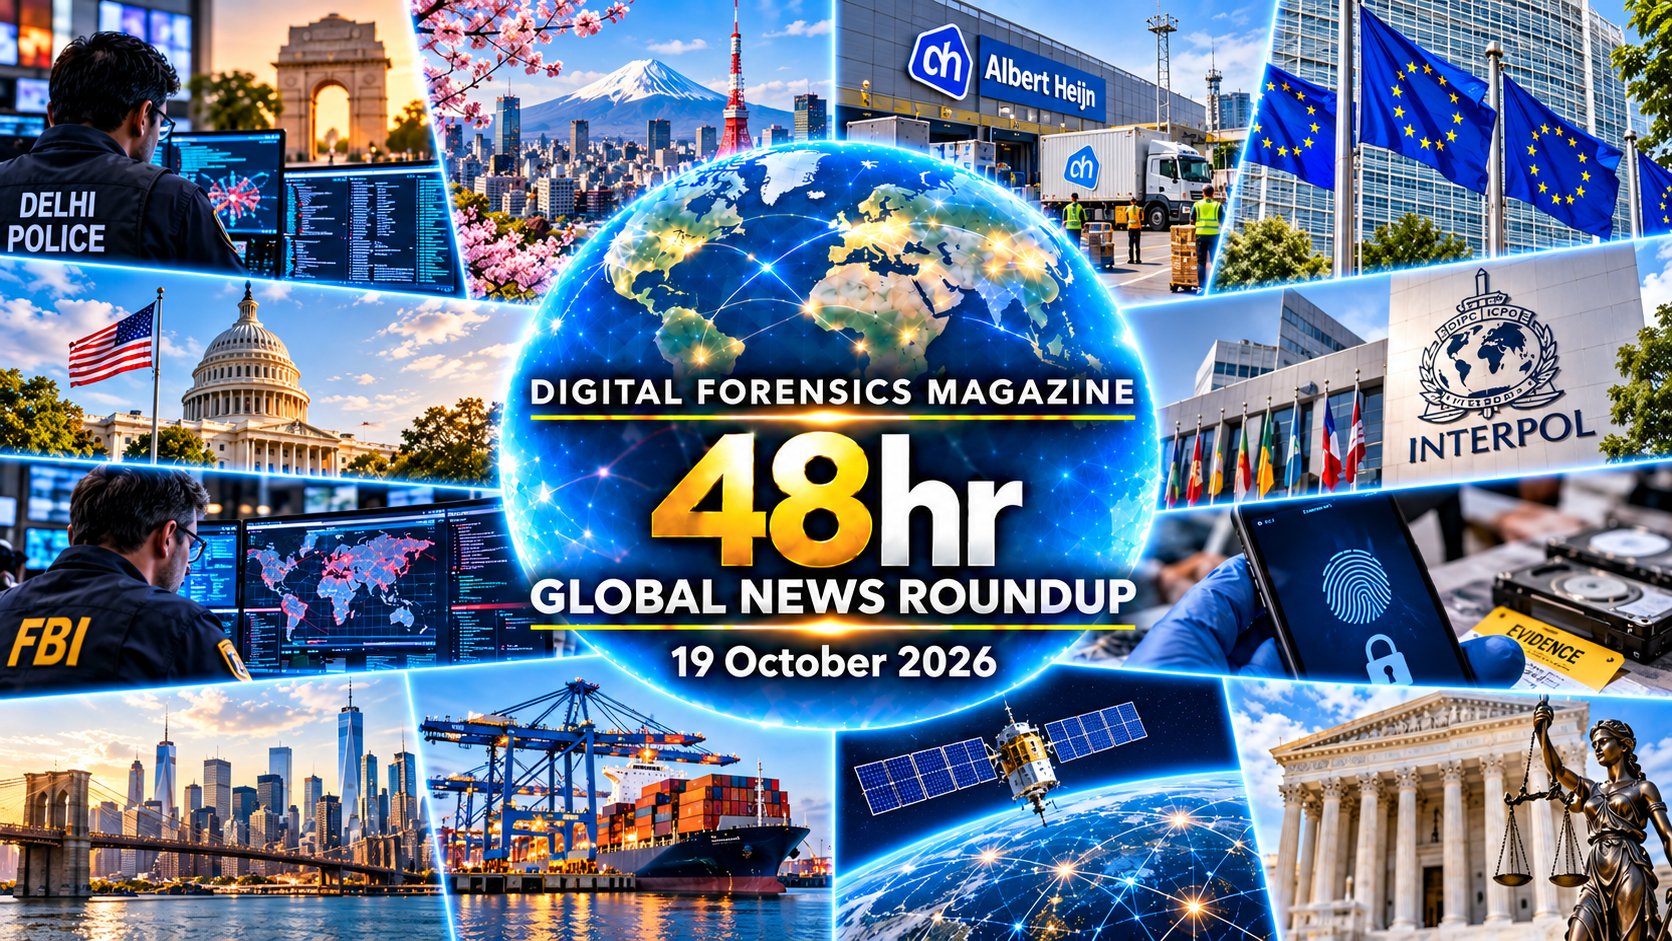

What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
Victoria police evidence audit
OpenCode legacy-system access
→Cyber Investigations
Delhi police trace suspicious transfers
Pakistan cybercrime complaint investigations
→Major Cyber Incidents
Dutch grocery online deliveries remain offline
ConnectWise Cloud Backup service suspended
→Exploits & Threat Intelligence
SiteGuard command-injection exploitation
Chrome security fixes
→Law Enforcement
Hyderabad digital arrest arrests
Makati alleged gambling hub arrests
→Policy & Standards
INTERPOL issues AI deepfake warning
US cyber evidence guidance discussions
→Australian reporting on 19 October described criminal charges against a former Victoria Police digital forensics officer and a review of at least 112 court cases potentially affected by irregularities in device handling, extraction or examination during his work. The allegations remain before the courts, while the reported audit raises significant questions about the chain of custody, quality assurance and the disclosure of possible evidential weaknesses to defence representatives and prosecutors.
OpenCode disclosed that unauthorised access to a legacy Console system may have exposed third-party API keys stored in affected workspaces, with its notification identifying approximately 1.4 per cent of Console users rather than all users of the service. Investigators must distinguish access to stored credentials from subsequent misuse of those credentials, correlate provider audit logs with affected workspace records and preserve the sequence of disclosure, key rotation and any confirmed downstream access.
Delhi Police reported intervening in suspected digital-arrest fraud affecting victims across five Indian states after investigators traced suspicious bank transactions and identified payments linked to impersonation calls, reportedly preventing losses amounting to approximately Rs 1.5 crore. The case illustrates how rapid transaction tracing, coordinated bank intervention, victim interviews and preservation of communications records can interrupt financial crime while investigators pursue the accounts and individuals responsible for directing the transfers.
Pakistan's National Cyber Crime Investigation Agency reported receiving 5,176 complaints, conducting 4,491 inquiries and registering 272 cases during its latest reporting period, with officials also claiming 1,129 arrests and recovery of 105.3 million rupees. Those figures are agency-reported outcomes rather than independently verified measures of criminal activity, but they indicate the scale of complaint triage, evidence assessment and financial tracing required to convert allegations into investigable cases.
Dutch supermarket Albert Heijn said on 19 October that its online deliveries would remain unavailable until at least Thursday after a cyber incident affecting services operated by parent company Ahold Delhaize, extending disruption that began earlier in the month. The newly extended recovery timetable is an operationally material development, although the retailer has not publicly established the technical intrusion mechanism or confirmed data theft, leaving investigators to distinguish service unavailability from unverified compromise claims.
ConnectWise issued further updates on 18 October after unauthorised access to application identities associated with its Cloud Backup service led it to suspend connections, revoke affected certificates and preserve encrypted backup archives during an ongoing investigation. The company stated that it had no evidence its stored backup archives were accessed, while warning that its own investigation could not determine whether each customer's live Microsoft 365 environment had experienced unauthorised activity.
Reuters reported on 19 October that research by Snorre Fagerland described a Chinese-speaking attacker using autonomous artificial-intelligence agents to compromise more than 100 websites, with the researcher estimating almost 1,200 attempted intrusions over several weeks and identifying major-company websites among the targets. The account raises evidence-preservation questions about agent instructions, tool execution histories and web logs, while the reported attack totals and costs remain research findings rather than independently established facts.
A cybersecurity briefing dated 18 October reported that Google had issued a Chrome 155 security update addressing multiple browser vulnerabilities, including memory-safety issues with possible remote-code-execution consequences in vulnerable installations. The briefing provides a useful prompt for patch verification and exposure assessment, but investigators should confirm the exact build, affected platforms and published vulnerability details against Google's original release notes before attributing any suspicious browser activity to these weaknesses.
Hyderabad cybercrime police arrested two men in connection with an alleged digital-arrest scam in which a retired employee and his daughter reportedly lost approximately Rs 29.17 lakh after criminals impersonated enforcement officials over communications channels. Police said the suspected proceeds moved through mule accounts, cash-deposit facilities and Tether cryptocurrency, creating a financial-evidence trail that investigators must reconcile with account ownership, device records and communications before responsibility is established.
Philippine regional reporting on 19 October described the arrest of five women during a police operation at a suspected offshore-gambling operation in Makati, placing another alleged illicit online operation under investigation. The reporting establishes a law-enforcement action but not guilt, and the evidential questions concern the provenance of recovered devices, financial and subscriber records, communications platforms and any digital material capable of linking individuals to specific alleged offences.
INTERPOL announced on 19 October a public-awareness campaign examining criminal misuse of AI-generated deepfakes, including fabricated voices and images deployed to impersonate trusted people and induce payments or disclosure of sensitive information across national boundaries. Investigators reviewing such complaints need to preserve original communications, payment trails and account records, and compare audiovisual artefacts against independently confirmed identities rather than treating an apparently convincing recording as proof of the alleged speaker’s involvement.
Editorial verification pending: a qualifying second Policy & Standards development with an original, dated source has not yet been established within the permitted 48-hour window or applicable section-specific 72-hour fallback. This clearly identified placeholder is not a news story and must be replaced before publication or before any V6.8.1 compliance certificate can be issued; the section must not be represented as complete while the source and event are unverified.
Editorial Perspective
The current developments underline a recurring investigative challenge: a credible chronology of events must be built from records held by several organisations, often across separate jurisdictions and services. Initial notices can establish that an access event or disruption occurred without establishing the precise mechanism or full impact. Investigative readiness therefore depends on retaining system, identity and transaction records long enough for independent correlation. Public communications should distinguish allegations, observed activity and confirmed findings.
Cloud application identities, remote infrastructure and financial intermediaries create evidential dependencies beyond the organisation first reporting an event. Investigators should record when logs were collected, what data sources were unavailable and which claims depend on a single reporting party. Cross-border cooperation can help reconstruct payment routes and account control, but contemporaneous preservation remains essential. The strongest conclusions will be those that connect technical artefacts, accountable custodians and independently corroborated timelines.
Reference Reading
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM