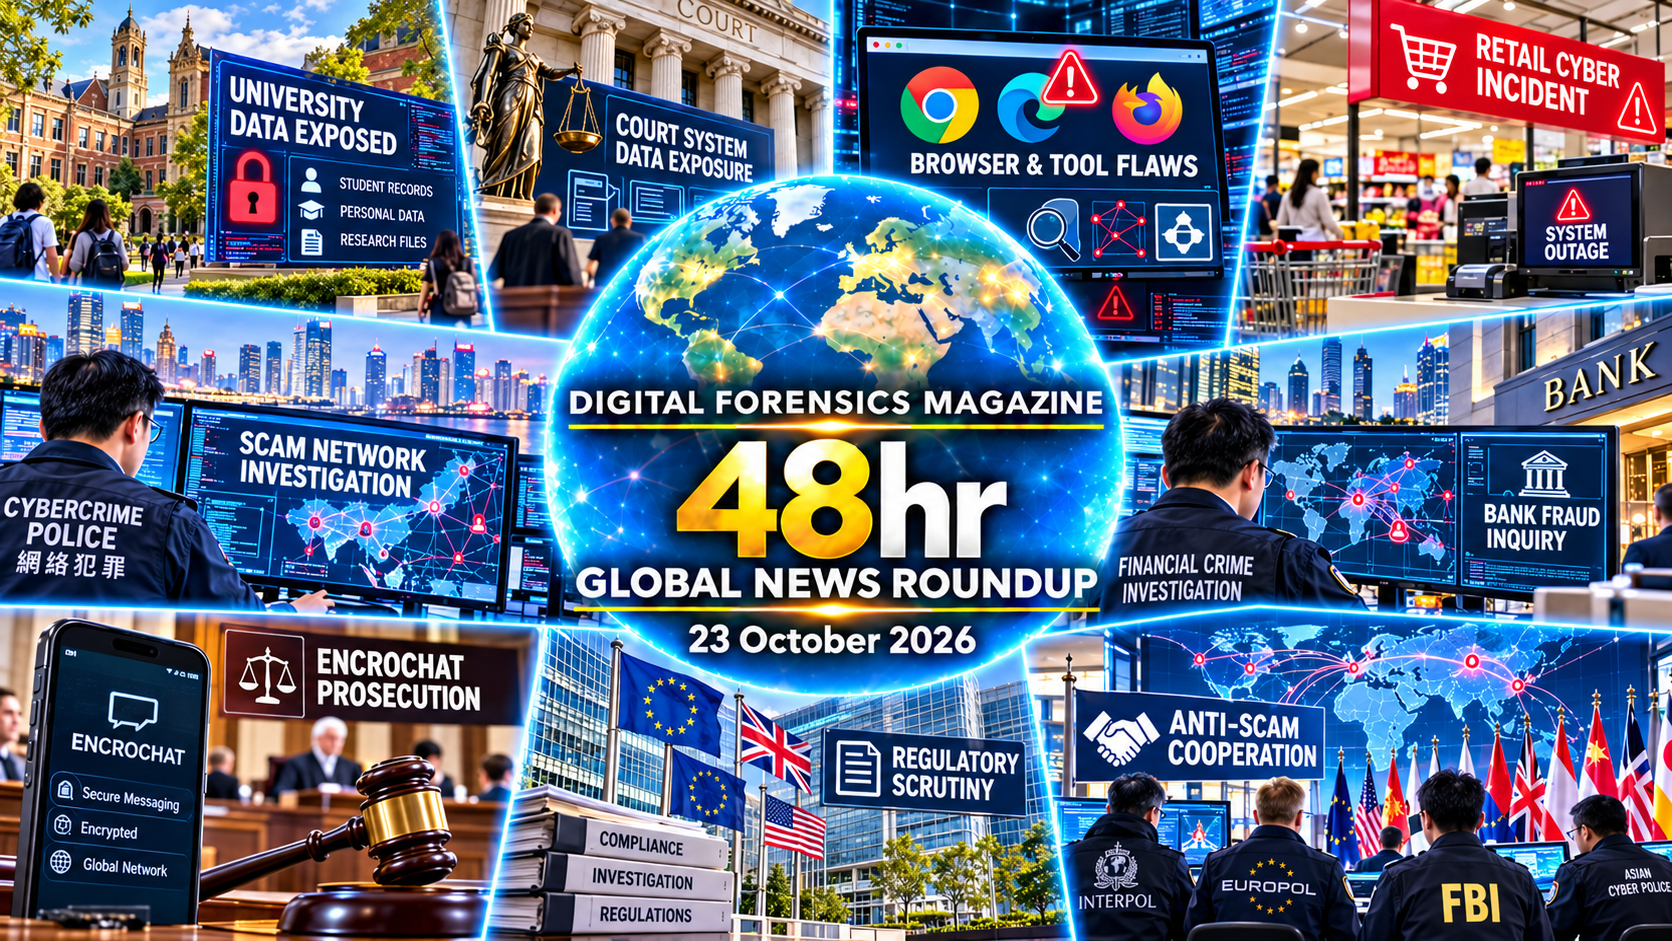
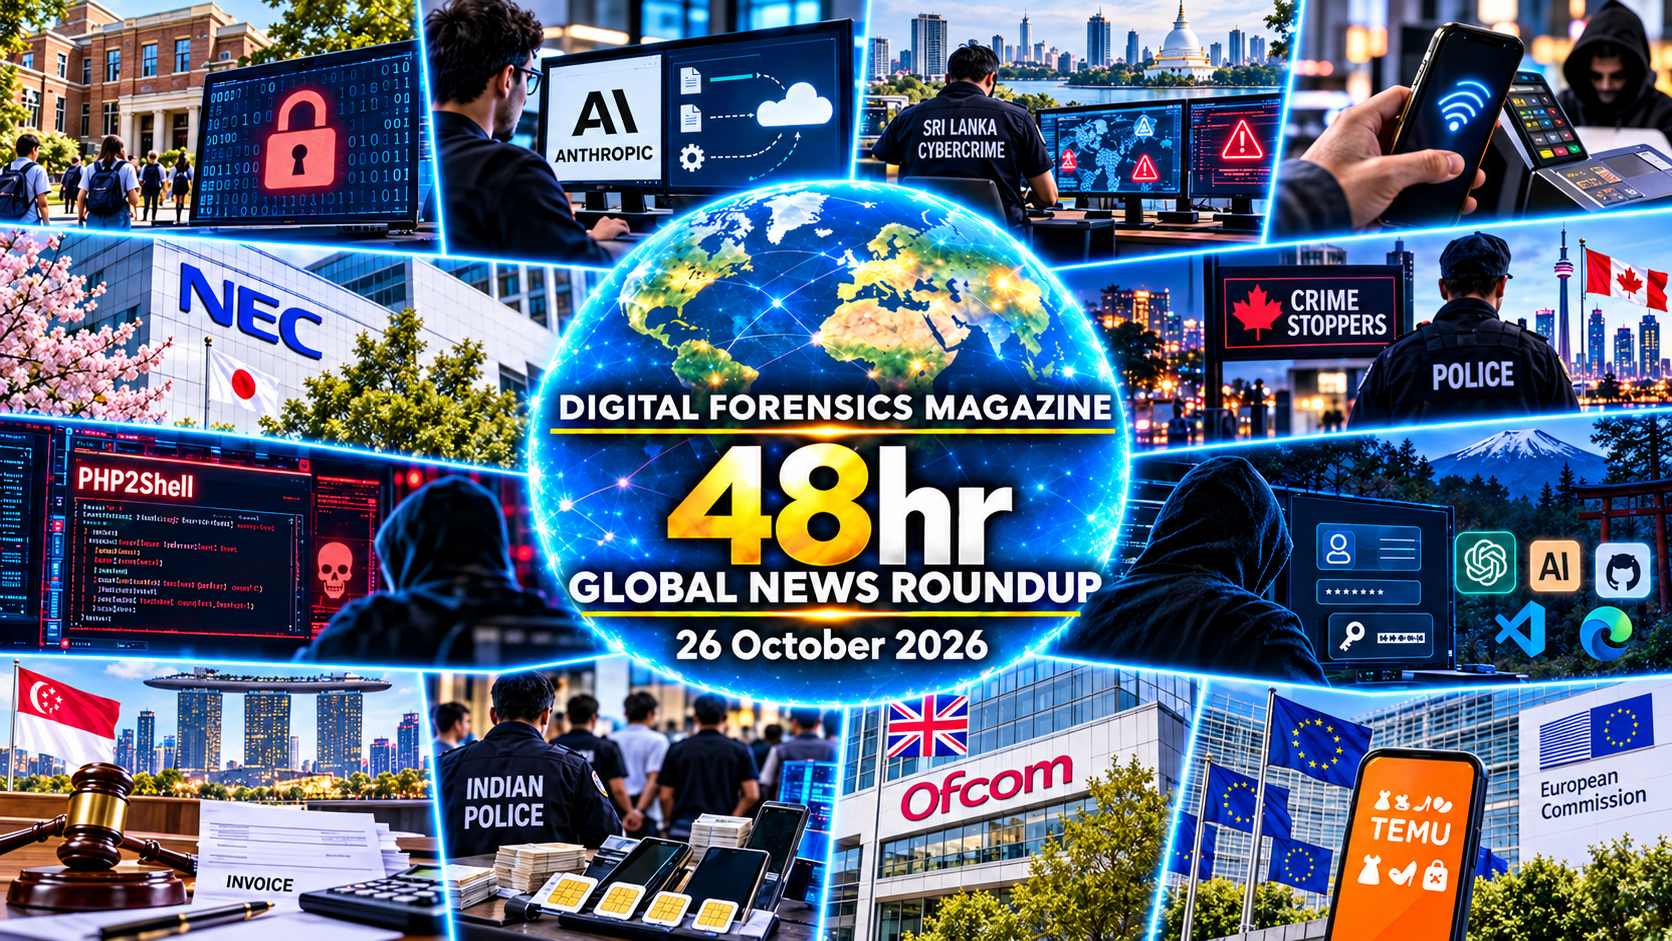

What’s in this roundup?
Two headline highlights from each section. Select a section to open it.
Digital Investigations
Frontline begins notifications following school-data investigation
Researchers demonstrate access to Anthropic business systems
→Cyber Investigations
Sri Lanka scam probes face evidence and prosecution obstacles
Dutch investigators trace bank theft through NFC relay applications
→Major Cyber Incidents
Japanese financial and transport firms disclose compensation plans
Canadian police suspend confidential tip platform following breach
→Exploits & Threat Intelligence
PHP2Shell investigation records successful remote execution
Threat bulletin profiles infostealer targeting AI application credentials
→Law Enforcement
Singapore charges former manager over alleged computer misuse
Indian police arrest suspect in SIM and mule-account inquiry
→Policy & Standards
Ofcom opens investigation into image-hosting compliance
European Commission accepts Temu risk-remediation plan
→Frontline Education announced on 26 October that its investigation of unauthorised access to US school administration services had identified personal information requiring notification, following activity on 14 and 15 August involving a vulnerability in third-party software. Its file review found differing combinations of Social Security numbers, dates of birth, identity documents, Medicaid identifiers and student identifiers, although the company reported no evidence of subsequent misuse and said the intrusion had been contained.
Reporting published in the United States on 26 October described how researchers from Cathedral used weaknesses in third-party business software to access internal Anthropic material during security testing, including meeting transcripts and staff and customer records. Anthropic disputed aspects of the researchers’ compliance with testing rules, said it had disabled the affected software and reported no evidence of other exploitation, while excluding customer conversations and model weights from the accessed material.
An investigation published on 25 October found that Sri Lankan authorities had arrested more than a thousand suspected participants in international online-scam operations during 2026 but secured no successful prosecution under the country’s computer-crime law. Police described obstacles involving overseas complainants, encrypted seized devices, language barriers and many phones and laptops, raising questions about cross-border victim evidence and the capacity to associate individual suspects with specific fraudulent transactions.
Dutch investigators have arrested two suspects in a telephone-based banking fraud investigation reported on 26 October, alleging that manipulated calls induced victims to install an application and scan payment cards so relayed NFC information could support cash withdrawals. Police reportedly seized servers, phones and laptops and linked the scheme to more than 170 victims and losses exceeding €380,000, although the suspects’ precise roles and the full evidential chain remain matters for ongoing investigation.
Reuters reported on 26 October that Japanese companies were announcing customer compensation following separate cyber incidents, including unauthorised access affecting GMO Internet Group’s foreign-exchange trading service and a personal-data incident at car-sharing operator Park24. GMO said it rejected a cryptocurrency ransom demand and was cooperating with authorities, while differing business impacts and compensation schemes underscore the need to separate confirmed customer harm, criminal claims and remedial decisions across unrelated incidents.
Sault Ste Marie Police confirmed on 26 October that it had paused participation in Crime Stoppers after a cybersecurity incident involving the independently operated platform used by reporting programmes across Canada, while emphasising that the platform was separate from police systems. The suspension reflects unresolved questions about the confidentiality of people supplying tips; investigators must distinguish the third-party exposure from evidence of compromise within any participating police force.
Security reporting on 26 October described honeypot evidence of successful remote code execution against an Apache mod_php installation running PHP 8.4.26 using the PHP2Shell vulnerabilities CVE-2026-109618 and CVE-2026-109619, extending earlier reports of attempted exploitation. The researcher’s captured memory disclosure and execution timing provide stronger technical evidence than scans or failed payloads alone, while individual organisations still need host-specific logs and artefacts before concluding that their own systems were compromised.
Check Point Research’s 26 October threat bulletin described Aokigahara as an information-stealing threat targeting authentication material associated with AI desktop applications, developer tools and cloud platforms, including assistants and coding environments used by organisations internationally. The summary identifies exposure of tokens and credentials but does not itself establish the number of confirmed victims, so investigative prioritisation depends on endpoint artefacts, token-use records and independent corroboration of any claimed compromise.
Singapore Police announced on 25 October that a former logistics manager was due to be charged on 26 October with offences including unauthorised access to computer material, cheating and money laundering after investigating fictitious supplier invoices. Police said their enquiries identified 128 invoices and company losses exceeding S$2 million, but those findings remain allegations to be tested against transaction records, account permissions and other evidence during the criminal proceedings.
Regional reporting updated on 26 October said Gujarat Police, assisted by officers in Indore, arrested a man wanted in an alleged cyberfraud case registered in Surat Rural district and transferred him for legal action. Investigators reportedly seized SIM cards and mule-account material during the inquiry, but the arrest does not establish the detained individual’s guilt or prove how each communications record and financial account was used in the suspected scheme.
UK communications regulator Ofcom opened a formal investigation on 26 October into whether an unnamed adult image-hosting service had met Online Safety Act duties concerning illegal content assessments and protections against non-consensual intimate imagery. The investigation examines risk-assessment and hash-matching obligations rather than establishing wrongdoing at the outset, with potential regulatory findings likely to depend on evidence of platform controls, documented decisions, detection processes and how potentially unlawful material was handled.
European reporting on 26 October said the Commission had accepted Temu’s plan to improve assessment of illegal-product risks under the Digital Services Act, giving the platform four months to implement several measures following earlier enforcement. Acceptance is not a finding that product listings are safe or that implementation is complete; future compliance review will depend on auditable risk assessments, platform moderation records and evidence connecting adopted controls to actual marketplace outcomes.
Editorial Perspective
Across the selected investigations, the central challenge is proving what activity occurred rather than repeating claims based on a breach notice, an arrest or a technical demonstration. Cloud logs, device extractions, financial transaction records and platform-moderation histories each answer different evidential questions. Investigators should preserve timestamps, acquisition methods and dependencies that allow these sources to be correlated without overstating what any single record proves. The difference between attempted exploitation and confirmed execution is especially important when deciding which systems require deeper examination.
Cross-border fraud cases reveal how investigative conclusions can stall even when arrests and seized devices are numerous. Encrypted material, overseas witnesses and inconsistent data retention can prevent a plausible narrative from becoming proof. Organisations should identify critical logs and ownership of third-party data before an incident, while documenting uncertainty in victim counts, data exposure and attribution. Regulators and courts will increasingly examine whether an explanation can be reproduced from reliable evidence rather than accepted on the authority of the announcing organisation.
Reference Reading
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM