
What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
Welsh ransomware inquiry exposes dormant test account
Indian bank investigates customer-record exposure
→Cyber Investigations
Indore cyber unit intercepts fraudulent transfer
Singapore investigators trace impersonation scam collectors
→Major Cyber Incidents
London cloud failure disrupts banking and public services
Stop & Shop restores services after parent-company incident
→Exploits & Threat Intelligence
UK issues urgent warning on critical PHP flaws
OVHcloud confirms tampered command-line release files
→Law Enforcement
US fraud defendant admits targeting service personnel
Singapore police seize device in card-data investigation
→Policy & Standards
California announces genetic-data breach settlement
US launches new fraud whistleblower incentive programme
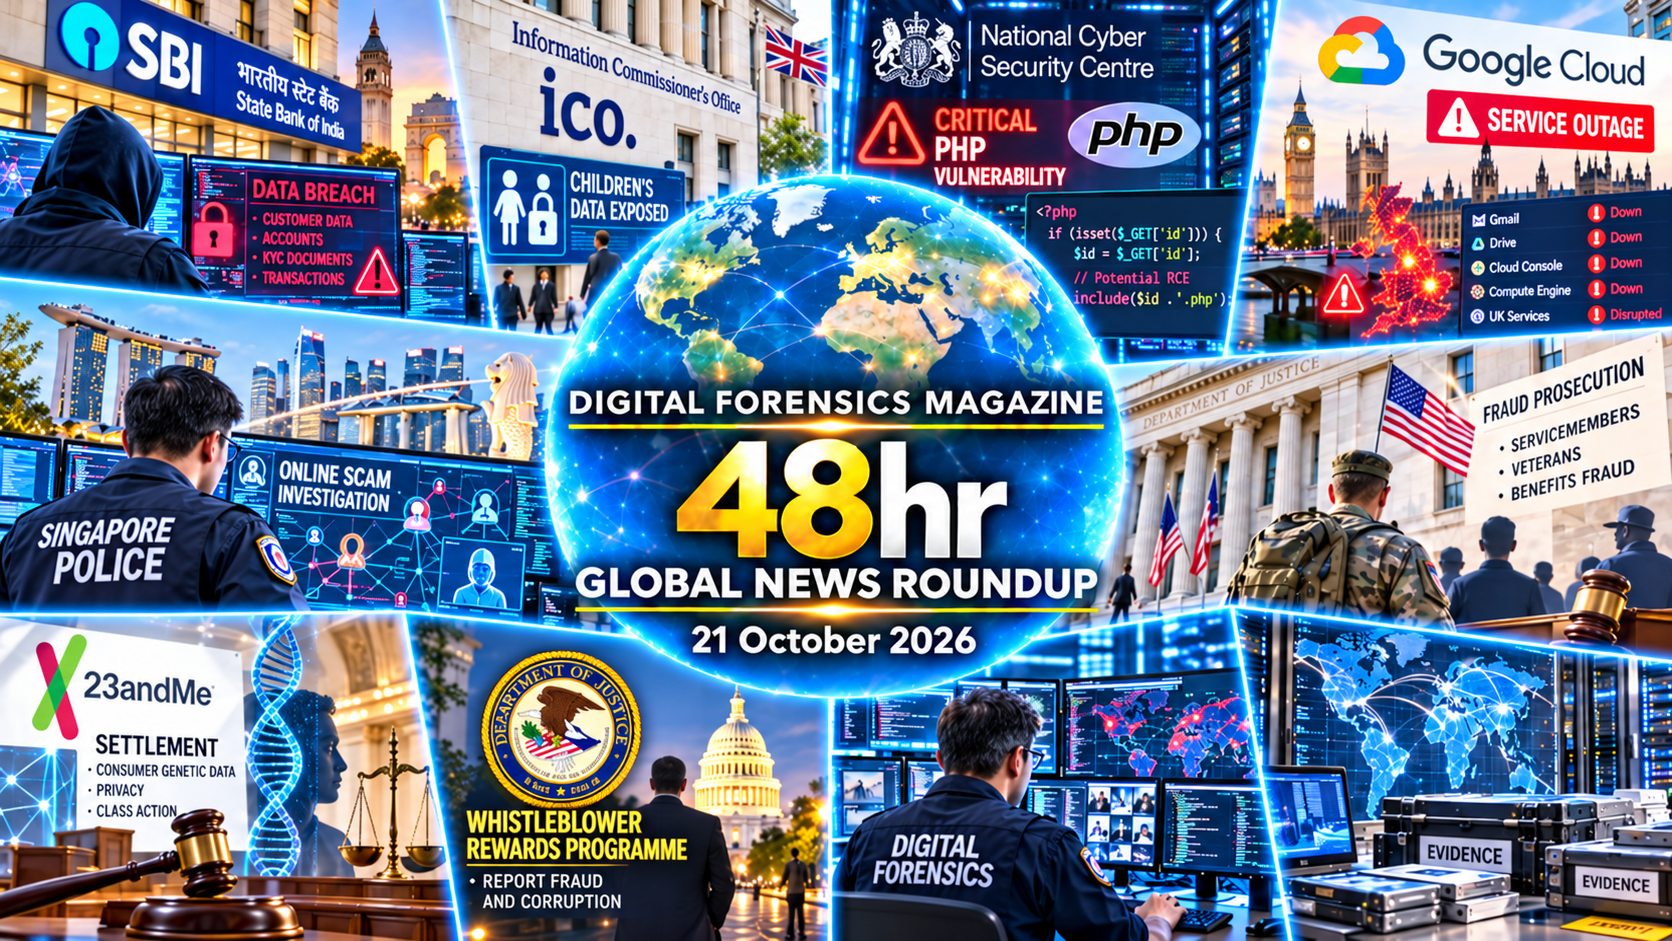
→The UK information regulator disclosed on 20 October that a 2024 ransomware intrusion affecting two Welsh organisations exposed information about approximately 3,300 people, predominantly children, after attackers exploited a longstanding test account protected by the password Password1. Its published findings identify 42 gigabytes of material taken from Data Cymru and raise specific questions about account ownership, access-history retention, supplier oversight and the records required to reconstruct the intrusion accurately.
State Bank of India disclosed on 21 October that examination of material reportedly appearing on the dark web identified 3,897 customer records containing names, contact details, identifiers and loan-related information, while the bank said core operations remained unaffected. An independent cybersecurity agency has been engaged to investigate, making data provenance, the completeness of the sample, possible access paths and whether the material originated from bank-controlled systems central questions before wider impact is inferred.
Cybercrime investigators in Indore, India, secured the return of Rs 1.45 lakh to a textile trader within twenty-four hours after a fraudulent electricity payment link was sent over WhatsApp, reporting stated on 20 October. Police said the funds had been routed through a merchant intermediary but were recovered before onward transfer, showing how complaint timing, merchant records and payment tracing can preserve a recoverable financial trail in an active investigation.
Singapore Police reported on 20 October that Cyber Command enquiries identified and arrested two Malaysian men suspected of collecting cash and jewellery for a government-official impersonation scam, with a hotel search recovering further valuables and cash. The investigation links WhatsApp communications, victim-directed banking access and physical collection activity, while police allegations about unidentified syndicate organisers will require transaction evidence and device records to establish individual roles and support any subsequent charges.
A Google Cloud disruption on 20 October affected services hosted in its London region and coincided with interruptions reported by British banks, retailers, delivery companies and remote court hearings, with Google attributing the failure to a power event rather than an established intrusion. Reconstructing the outage requires correlating provider infrastructure timelines with customer application logs and failover records, rather than treating widespread unavailability as evidence that the affected organisations were separately attacked.
US supermarket chain Stop & Shop restored its website and application after interruptions affecting Ahold Delhaize, according to Connecticut reporting on 20 October, marking a material recovery development after the parent-company incident previously covered by DFM. Restoration of digital ordering establishes a changed operational status but does not itself establish the cause of the original security incident, and investigators must distinguish verified service recovery from unresolved questions about access and data exposure.
The UK National Cyber Security Centre warned organisations on 21 October to identify systems running PHP and prepare for an emergency security release responding to two critical vulnerabilities announced by the PHP Foundation, prioritising internet-facing servers and dependent products. Its advice calls for heightened monitoring, prompt updates and taking systems offline where mitigation is unavailable, while the presence of vulnerable software alone must not be represented as evidence of compromise or successful exploitation.
OVHcloud developers confirmed on 20 October that release assets for several versions of the OVHcloud command-line tool had been replaced through a compromised contributor account on 19 October, exposing downloaders during a limited distribution window to malicious binaries. The project subsequently issued a security advisory, making release-file hashes, download timestamps, local execution history and possible credential access essential to identifying affected environments without assuming every existing installation received the substituted files.
The US Department of Justice announced on 20 October that Robert Wayne Boling Jr pleaded guilty to an identity-theft scheme using information about US military personnel and veterans to access accounts and benefits. The admission establishes a criminal outcome in the case, while investigators must continue to distinguish proven conduct from the broader scale of victim losses and reconstruct which records connect transactions to the admitted scheme.
Singapore Police announced on 20 October that a 42-year-old man would face a charge relating to allegedly using an electronic device to obtain bank-card information after reports of suspicious activity on Syed Alwi Road. Officers seized an electronic device, power banks, a telephone and bank cards, creating a defined set of exhibits whose forensic handling and examination may help establish device capability, any captured data and the suspect’s alleged conduct.
California Attorney General Rob Bonta announced on 19 October a proposed settlement with Chrome Holding, formerly 23andMe, over a 2023 breach and genetic-data transfers during bankruptcy. The agreement remains subject to court approval and highlights the need for organisations handling sensitive forensic or identity data to document authorisation, retention, disposal and consent decisions across ownership changes, rather than treating sale of an organisation as a transfer of unrestricted data rights.
The US Department of Justice launched its Fraud Whistleblower Incentive Program on 20 October, offering qualifying informants accelerated financial awards for information leading to criminal charges and including cyber-enabled fraud investigations. The programme creates an additional intake channel for investigative leads, but corroboration, evidence provenance and secure handling of submitted records remain necessary before a tip can substantiate criminal conduct or support cross-jurisdictional tracing and prosecution.
Editorial Perspective
Across this cycle, investigators face evidence that is dispersed among hosting providers, customer databases, individual devices and financial accounts. Even when a public statement confirms an outage or a suspected leak, the statement does not establish the origin or full scope of unauthorised activity. Examination therefore depends on preserved logs, repeatable extraction methods and careful separation of observed actions from claims. These distinctions are essential when findings may later be scrutinised by regulators or courts.
Cross-border enquiries add further challenges when data retention periods, legal authorities and technical collection standards differ between custodians. Early preservation requests and consistent event timelines improve the prospect of linking systems, accounts and individuals without overstating attribution. The provenance of recovered credentials, records and communications should be documented alongside uncertainty and any gaps in the evidential sequence. Investigative readiness is ultimately measured by whether another examiner can reconstruct the same supported conclusions from the retained material.
Reference Reading
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM