
What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
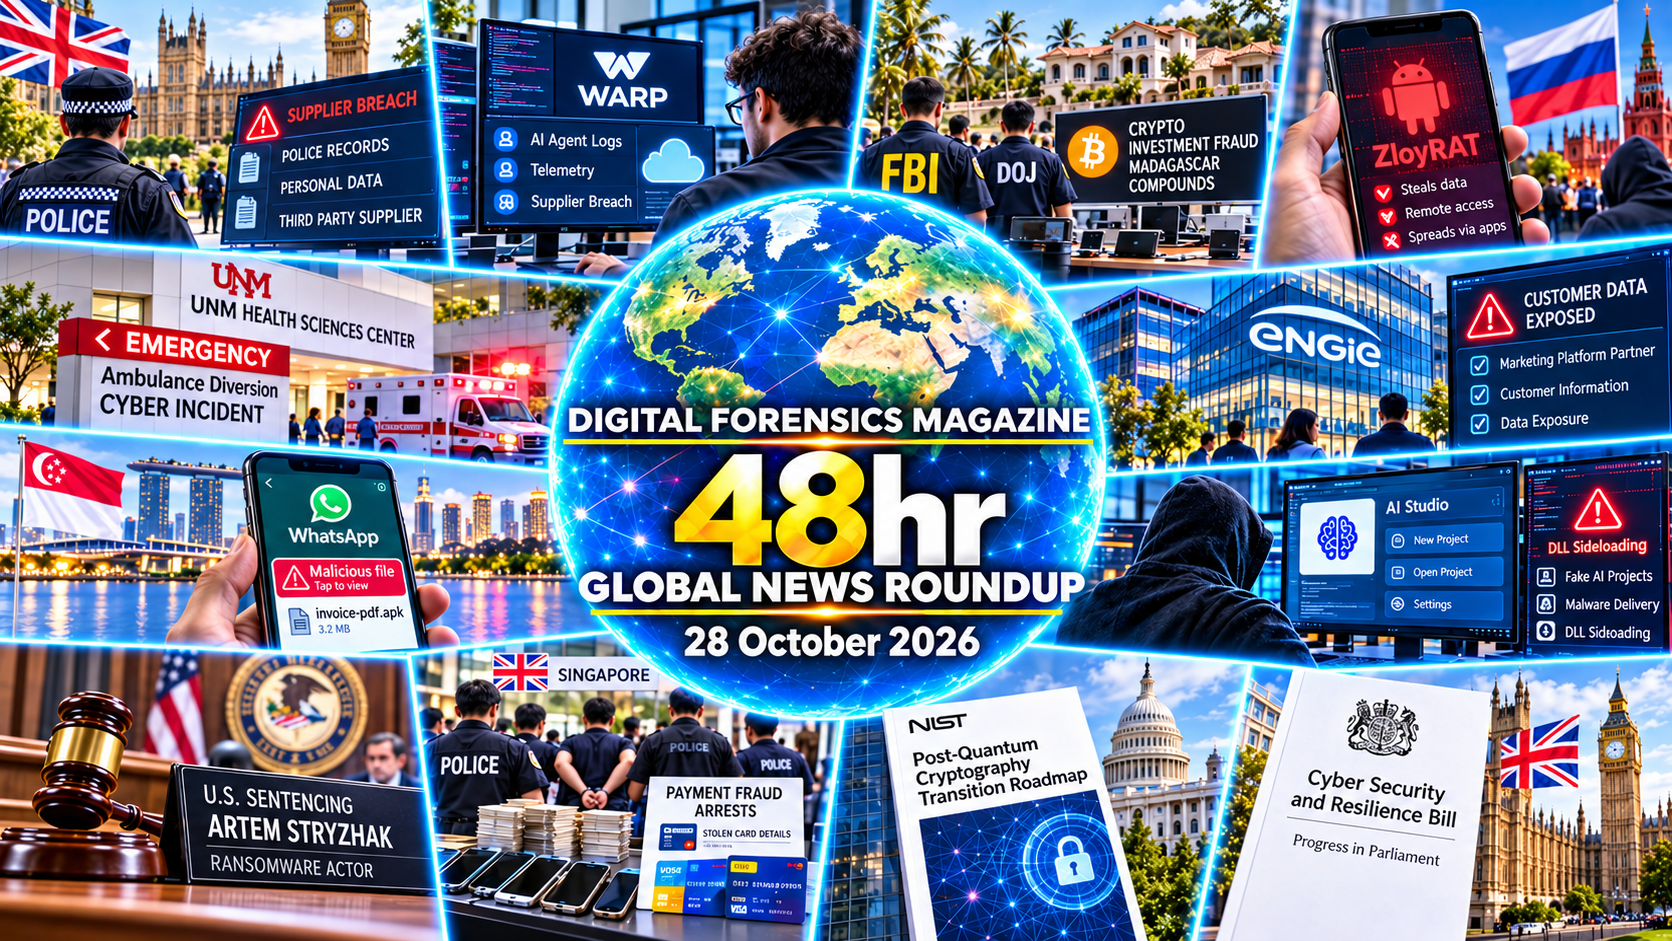
Police supplier attacks expose evidence-access gaps
Warp investigates exposure of agent activity records
→Cyber Investigations
FBI traces alleged Madagascar crypto scam network
Researchers trace deceptive Android apps targeting Russia
→Major Cyber Incidents
New Mexico hospitals resume care after cyber disruption
ENGIE confirms partner-platform customer exposure
→Exploits & Threat Intelligence
Singapore warns of WhatsApp attachment malware
Signed AI binaries abused in malware delivery chain
→Law Enforcement
Ransomware conspirator sentenced in New York
Singapore arrests suspects in mobile-wallet card fraud
→Policy & Standards
NIST releases post-quantum transition roadmap
Lords amend UK cyber-resilience legislation
→British police information held by third-party technology suppliers was put at risk in multiple cyberattacks between 2021 and 2025, according to an inspectorate report published in England and Wales on 27 October. Inspectors found that supplier security assurance was frequently inadequate and access to supplier-held logs could be limited, while the public report withheld operational details and did not establish how many incidents involved actual disclosure of investigative records.
US developer-tool provider Warp disclosed on 27 October that attackers exploited a supplier in its infrastructure, exposing some users’ AI agent decision logs and telemetry. The company estimated that roughly one per cent of users might be affected and engaged external specialists, but the precise population and sensitivity of exposed records remained under investigation, making distinctions between stored execution histories, customer credentials and confirmed downstream misuse particularly important.
US prosecutors announced charges on 27 October over alleged cryptocurrency investment fraud operated from compounds in Madagascar, following FBI examinations of devices and cryptocurrency transactions linking suspected perpetrators to American complainants. Authorities described access to more than 3,000 devices and difficulties interviewing suspects who had been repatriated, while the indictments do not establish guilt and questions about the roles of paid workers and possible trafficking victims remain unresolved.
Researchers examining malicious Android applications distributed to users in Russia identified a campaign exploiting concerns over fuel availability and drone strikes, according to reporting published on 27 October. The applications posed as fuel-location, drone-warning and government VPN tools but reportedly delivered the ZloyRAT trojan, creating investigative leads in package artefacts, permissions and command infrastructure; published findings did not independently establish the number of infected devices or identify the operators conclusively.
University of New Mexico Health Sciences Center said on 27 October that critical systems had returned online after a cyber incident temporarily diverted ambulances and suspended appointments in Albuquerque. The institution said some end-user devices were affected without penetration of core servers, while law-enforcement enquiries continued; investigators must distinguish the demonstrable interruption of healthcare services from unverified speculation about stolen information or the identity and method of the attacker.
French energy company ENGIE confirmed on 27 October that unauthorised access to a commercial partner’s marketing platform exposed information associated with customers in France. The company said its internal systems were not compromised and that affected individuals and authorities had been notified, but did not disclose a confirmed victim total; the separate supplier boundary and uncertainty around what was extracted complicate evidence preservation, customer notification and assessment of possible subsequent impersonation attempts.
Singapore’s cyber emergency response authorities warned on 27 October about malware circulated through compromised WhatsApp accounts using attachments presented as legitimate business files. SingCERT reported that some people who opened suspicious files later found similar messages sent from their own accounts without permission, indicating a potential propagation mechanism that investigators should examine through device artefacts and linked-session records rather than treating every received attachment as evidence of successful compromise.
Check Point Research reported on 27 October that an malware campaign used fake AI desktop projects and legitimate signed application binaries to load malicious components by DLL sideloading. The researchers labelled the activity Yoba and described Telegram, Tor and DNS-over-HTTPS communications, while indicators offered only a tentative assessment of the actor’s origins; analysts can test the reported execution chain against file provenance, process relationships and endpoint telemetry before drawing attribution conclusions.
A federal court in Brooklyn sentenced Ukrainian national Artem Stryzhak on 27 October to 70 months in prison after his plea in a case involving ransomware extortion against organisations in several countries. US prosecutors linked the conspiracy to attacks on hospitals, businesses and government organisations and said a co-conspirator remained at large, while the prosecution illustrates the importance of preserving victim-system records, payment trails and defendant-specific evidence across national boundaries.
Singapore Police announced on 27 October that three men had been arrested in a suspected payment-fraud operation involving stolen card details and high-value electronics purchases. Officers said retail staff reports, CCTV and police camera images helped trace two suspects to Changi Airport, where they were arrested, and seized phones and graphics cards as exhibits; the allegations still require proof connecting each device, payment credential and transaction to individual conduct in court.
The US National Institute of Standards and Technology published NIST IR 8547 on 27 October, setting out an official transition roadmap from quantum-vulnerable cryptography to post-quantum standards. Its guidance provides migration milestones relevant to agencies and industry, requiring organisations to establish inventories of algorithms, certificates and dependent systems before changes are made; such records can also protect evidential continuity where archived signatures, long-lived records or encrypted investigative material must remain verifiable.
The UK House of Lords completed a report-stage examination of the Cyber Security and Resilience Bill on 26 October, agreeing numerous amendments and rejecting another during recorded divisions. Parliamentary records confirm legislative progress rather than an enacted compliance duty, and organisations tracking proposed incident reporting and supplier oversight obligations should retain a clear record of which text was amended, what remains under consideration and when any eventual requirements actually take legal effect.
Editorial Perspective
Across the selected coverage, investigative certainty depends on records held by organisations that do not always control the systems where those records originate. Supplier logs, cloud execution histories, mobile device artefacts and payment records require preservation with acquisition times and scope clearly identified. Without that context, a claimed intrusion can be confused with verified disclosure, and suspicious activity with demonstrated compromise. Investigators should document evidential gaps as carefully as established findings.
Several developments also show why the distinction between an operational announcement and an evidential conclusion matters. Criminal allegations, technical attribution hypotheses and preliminary victim estimates are not interchangeable with proven facts. Cross-border enquiries need reproducible links between devices, communications, transactions and identified actors, while cryptographic transitions may affect the later verification of preserved evidence. Reliable investigative readiness therefore requires accessible logging, clear supplier obligations and documented methods for validating the provenance of digital records.
Reference Reading
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM