
What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
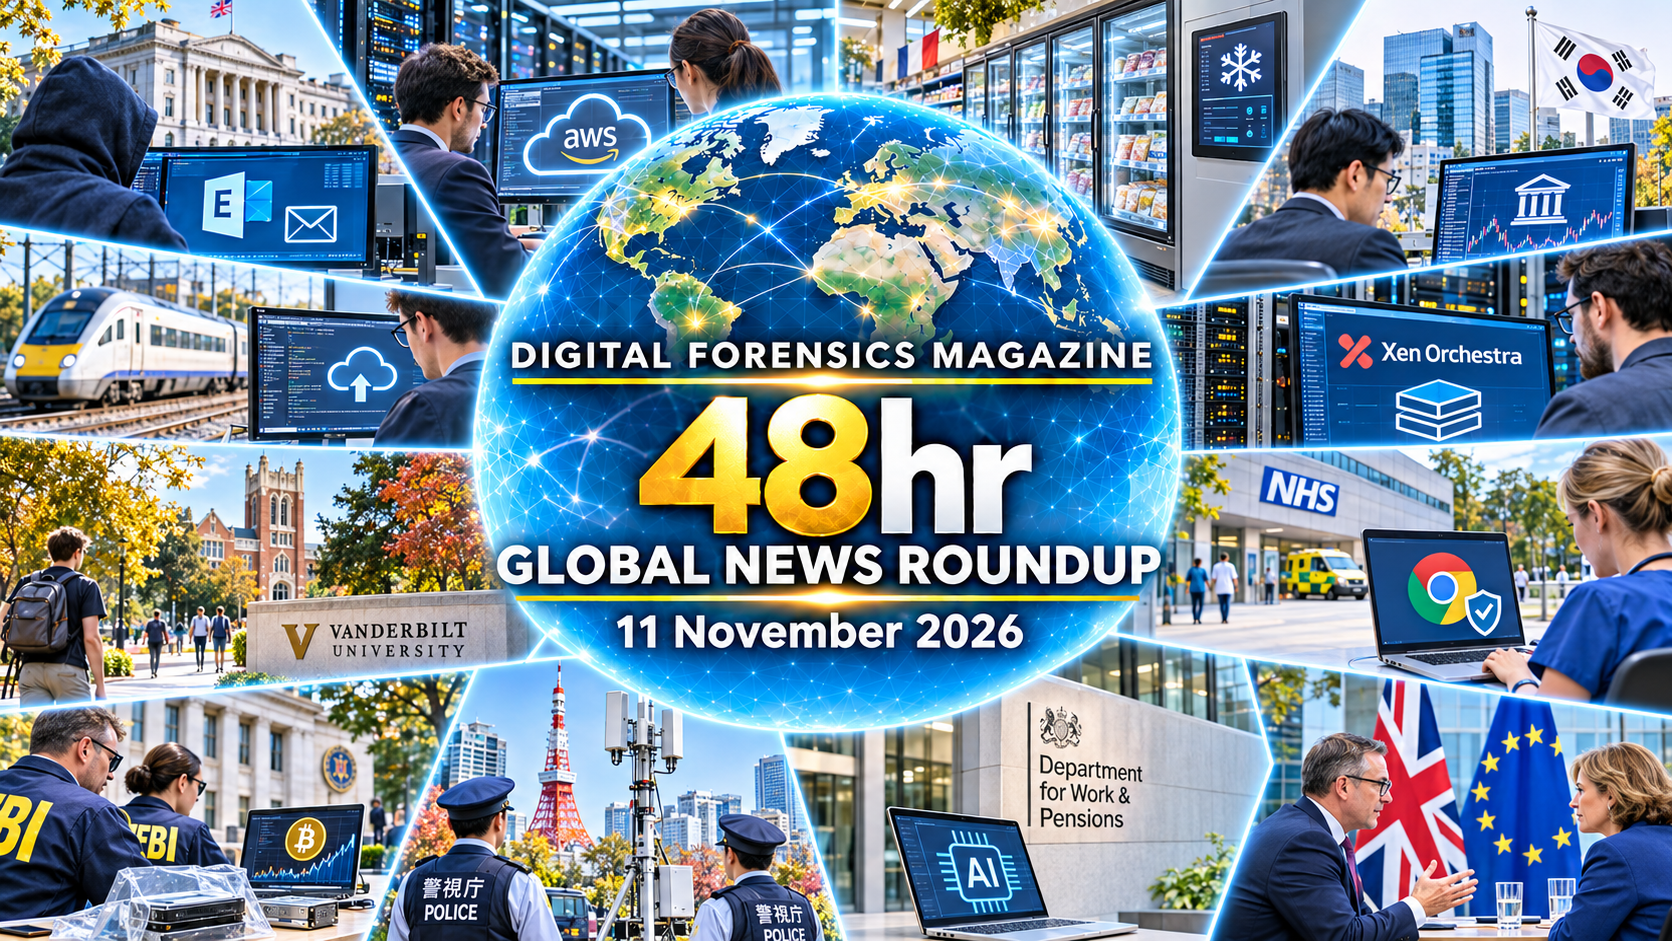
Turla Exchange tool exposes government mail flows
Cloud role-assumption logs trace Qubole intrusion
→Cyber Investigations
France attributes refrigeration sabotage to Iranian unit
Korean financial-security assessment portal breached
→Major Cyber Incidents
Railway quantifies stolen secrets and AI misuse
Vanderbilt restores services while investigating intrusion
→Exploits & Threat Intelligence
Xen Orchestra authentication bypass under exploitation
NHS issues alert on exploited Chrome flaw
→Law Enforcement
FBI cryptocurrency trail leads to device seizure
Tokyo suspect referred over rogue mobile transmitter
→Policy & Standards
DWP introduces AI security standard for suppliers
UK and EU revisit Cyber Resilience Act alignment
→ESET researchers published findings on 10 November identifying a modular Exchange surveillance toolkit, named Cereal, at government organisations in Kazakhstan and Romania, with the latter collecting correspondence involving European Union and NATO contacts. The researchers attributed the activity to the Russia-aligned Turla group and described components embedded in Exchange transport processing, making server-side mail-flow records and evidence of module injection important to reconstructing collection and access.
Wiz published a technical reconstruction of intrusions involving AWS access roles trusted by Qubole customers, reporting that compromised credentials associated with the provider enabled access across multiple customer environments during October. Its examination of CloudTrail role-assumption records, Secrets Manager queries and S3 object activity identified credential harvesting and data access, while noting that absent object-level logging could prevent investigators from establishing precisely which files were taken.
France formally attributed the October compromise of refrigeration controls at more than 700 domestic retail sites to the Iranian-linked Shahid Kaveh cyber unit in a government statement published on 10 November. Authorities said the disruption caused fires and food spoilage, but Iran rejected the accusation, leaving investigators and prosecutors to distinguish technical indicators, official attribution assessments and independently demonstrable responsibility as the cross-border case develops.
South Korea’s Financial Security Institute reported an intrusion into the web system used to assess information protection at financial firms, with the incident detected on 9 November and disclosed the following day. According to Yonhap’s reporting from financial authorities, leaked material included assessment forms and some personal and system-user information, while the method of entry and complete exposure remain important subjects for technical investigation rather than established conclusions.
US cloud platform Railway published its forensic report on 10 November concerning an October intrusion, describing attacker access to decrypted environment variables and approximately 740,000 dollars in unauthorised AI-provider usage. The company said the maximum possible exposure was around 100,000 workspaces rather than a verified number of compromised accounts, and its reconstruction connects stolen build credentials, service trust weaknesses and subsequent use of customer secrets.
Vanderbilt University continued issuing updates on 10 November after an active cybersecurity incident disrupted university systems and prompted restrictions on devices, wireless access and cloud-based services in Tennessee. Its published updates describe phased restoration while staff investigate whether any data was accessed, meaning operational recovery must not be interpreted as confirmation of the intrusion route, the extent of exposure or the attacker’s publicly claimed activity.
Vates disclosed on 10 November that attackers were actively exploiting VSA-2026-062, a critical authentication bypass in Xen Orchestra and its appliance, potentially granting administrative access to managed virtualisation environments. The advisory identifies malformed authentication-token handling, provides indicators of compromise and states that corrected releases are available, so investigators should preserve management logs and check for the described host artefacts before treating patch installation as evidence that no intrusion occurred.
NHS England published a security alert on 10 November following Google’s Chrome updates for CVE-2026-125350, a high-severity use-after-free weakness in the browser’s XML component for which exploitation had been reported. The NHS alert identifies affected desktop versions and recommends installing updated releases, while the limited public exploit details mean any suspected compromise still requires endpoint evidence and correlation with browsing and execution records rather than inference from version alone.
US federal prosecutors announced on 10 November that an Albuquerque man had been charged after investigators traced alleged cryptocurrency payments to an illicit dark-web child sexual abuse material service and obtained a search warrant. FBI agents seized a mobile telephone on 9 November, and the prosecution remains an allegation; subsequent forensic examination and the relationship between payment records, account ownership and device contents will be central to the evidential case.
Japanese police referred a suspect to prosecutors after discovering an allegedly unauthorised mobile base station operated from a car in Tokyo’s Ginza district, according to Kyodo reporting published on 10 November. Investigators suspect the equipment disrupted normal mobile service and could have forced nearby devices onto a counterfeit network carrying phishing messages, although the suspect’s liability and links to credential theft remain allegations subject to examination of seized transmission equipment.
The UK Department for Work and Pensions updated its published procurement security requirements on 10 November, adding Security Standard SS-040 on artificial intelligence and machine learning to its supplier-facing catalogue. The new standard sits within a wider contractual security framework and makes documentation of permitted AI systems, access, data handling and assurance relevant to organisations supplying government services, although applicability still depends on the terms of each agreement.
The UK and European Union said on 10 November that their Withdrawal Agreement Joint Committee had considered the Cyber Resilience Act’s relationship to the Windsor Framework and agreed to examine ways of preserving its effective operation. No final extension or implementation decision was announced, so vendors and public bodies assessing connected-product obligations should distinguish the committee’s stated intent to examine options from any legally operative change in requirements.
Editorial Perspective
Across government mail systems, third-party cloud access and infrastructure controllers, an investigative finding depends on the quality of records that join an identity to a specific action. Evidence from identity-provider logs, management interfaces, application telemetry and physical devices should be correlated without treating a successful sign-in as proof of data extraction. Investigators also need to document where logging was disabled or retention has expired, because those absences constrain the strength of any negative finding. Preserving original timestamps and collection methods makes the reconstruction reproducible across jurisdictions.
This cycle also highlights the distinction between a public allegation, a technical assessment and an evidentially established fact. Impact estimates, attribution statements and claimed volumes of compromised material require separate verification against system records and independent evidence. Organisations should retain original exports and document any transformations used to prepare analytical datasets, particularly when evidence moves between cloud providers, regulators and police. A sound digital investigation identifies what the available evidence can establish, what remains uncertain and which records could resolve that uncertainty.
Reference Reading
- NIST SP 800-86 — Guide to Integrating Forensic Techniques
- NIST SP 800-92 — Guide to Computer Security Log Management
- NIST SP 800-61 Rev. 3 — Cybersecurity Incident Response
- RFC 3227 — Guidelines for Evidence Collection and Archiving
- MITRE ATT&CK T1078 — Valid Accounts
- AWS CloudTrail — Logging Data Events
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM