
What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
Bitdefender reconstructs 3AM activity across UK schools
Mandiant traces stolen cloud AI access and resale
→Cyber Investigations
NSW detectives investigate isolated health server breach
Mumbai investigators trace accounts linked to trading scams
→Major Cyber Incidents
GMO acknowledges earlier warnings about compromised service
cPGuard supplier details malicious update distribution
→Exploits & Threat Intelligence
Mozilla patches Firefox layout vulnerability
Canadian cyber centre flags exploited WordPress flaw
→Law Enforcement
European authorities dismantle investment-fraud infrastructure
US charges fourteen in alleged account-takeover network
→Policy & Standards
UK updates cyber resilience bill implementation factsheets
UK cyber authority publishes findings from 337 incidents
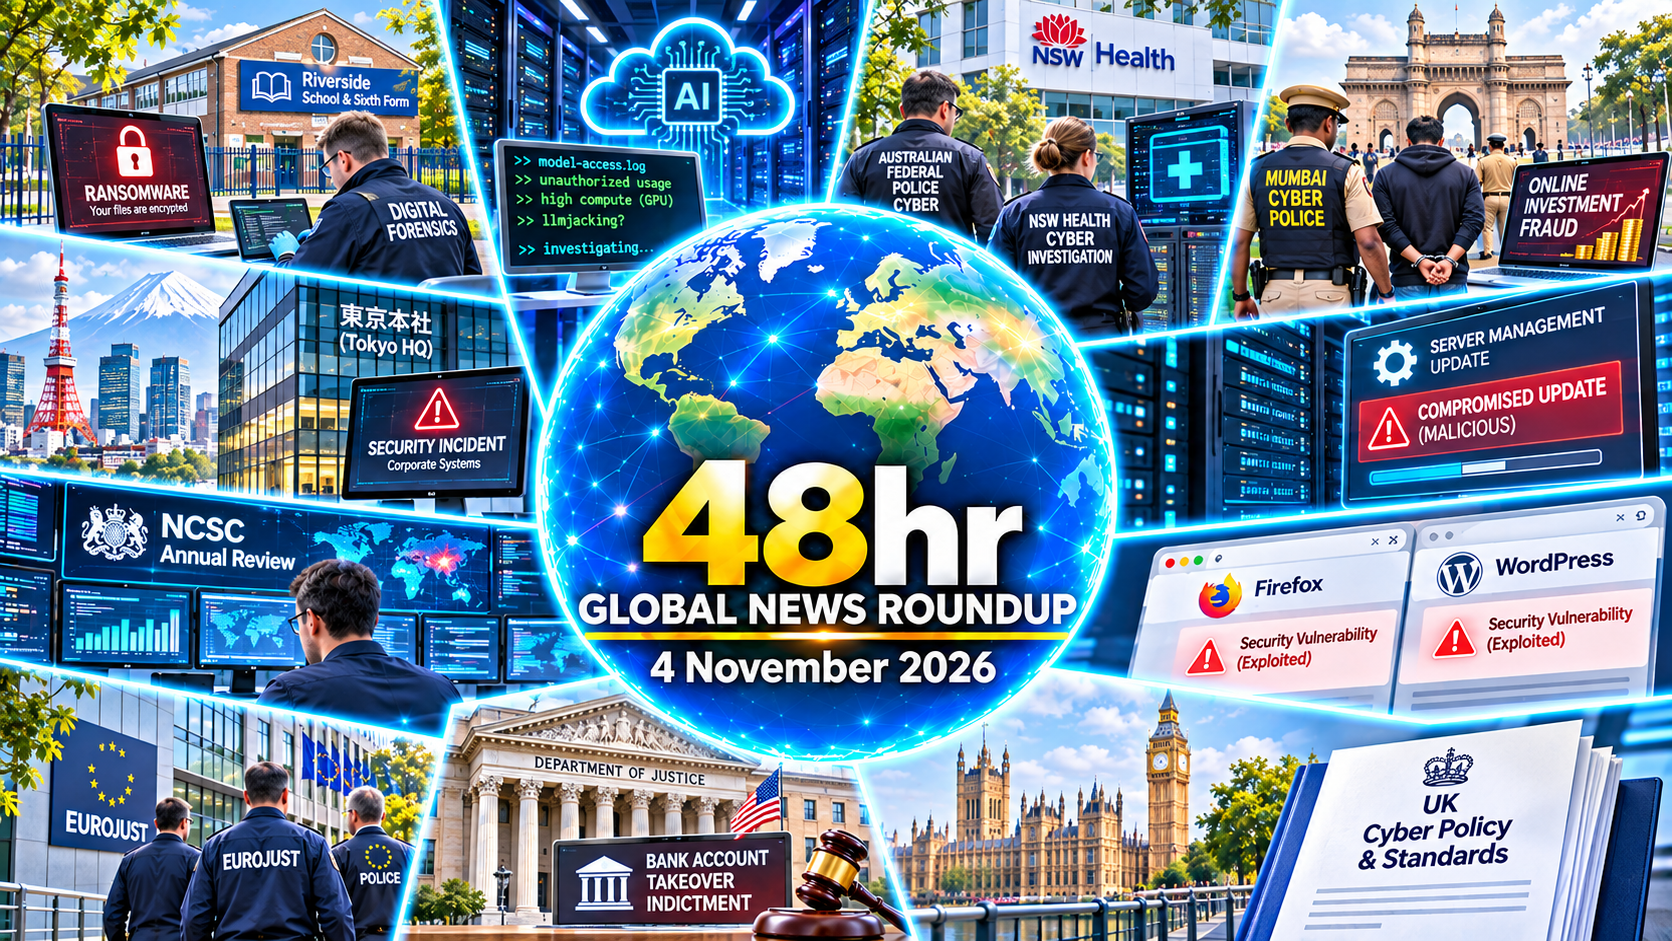
→Bitdefender researchers published their reconstruction of a 3AM ransomware intrusion into a United Kingdom school estate, identifying encryption on approximately 37 machines and command sequences that appeared consistent with automated retry behaviour. Their technical account distinguishes observed command timing, domain-trust activity and lateral movement from the unconfirmed hypothesis that a language model controlled the activity, since the investigators did not examine the attacker’s originating computer or directly identify an AI service.
Google and Mandiant investigators described 2026 intrusions across several regions in which attackers exploited exposed artificial intelligence endpoints or stolen credentials to consume enterprise model services without authorisation. Their case evidence identified distinct access and resale roles, including intermediary services that route stolen model capacity, while reported charges exceeding $100,000 in a day in some investigations remain specific observed losses rather than an estimate of worldwide financial impact.
Australian authorities confirmed that the New South Wales Police Cybercrime Squad was investigating unauthorised access to an isolated NSW Health server, with Cyber Security NSW classifying the matter as a major incident. Although an alleged intruder claimed to have taken a large collection of documents, officials said no patient data had been affected or was currently at risk, leaving the claimed volume, contents and precise entry method unverified pending forensic examination.
Mumbai cyber police arrested three men in Nagpur during an investigation into alleged online trading fraud, reporting that accounts connected to the suspected operation appeared across 73 complaints in India. Investigators described a fictitious company and banking arrangements allegedly used to receive and redistribute proceeds, but the correspondence between individual transactions, device evidence and the three suspects must still be established through financial records and subsequent judicial proceedings.
At a Tokyo press conference on 2 November, GMO Internet Group acknowledged that it had failed to act adequately on security weaknesses identified internally in 2024 before the compromise of its Onamae.com Desktop Cloud service. Executives described missed opportunities to prioritise corrective work and announced reductions in remuneration, providing a material new governance finding while the separate questions of customer losses, unauthorised trading and the full technical intrusion chain remain under investigation.
Security supplier OPSSHIELD disclosed that attackers compromised its billing and licensing infrastructure and used a stolen update key to deliver a malicious cPGuard update to customer servers on 2 November. Its subsequent reconstruction described compromised administrative credentials and files copied from affected systems, but installation counts and the scope of usable secrets require independent customer verification, including update histories, server logs and evidence of any subsequent account access.
Mozilla issued Firefox 159.0.1 on 3 November with a security correction for CVE-2026-120572, identifying incorrect boundary conditions in the browser’s block and inline layout component and assigning the issue a high impact rating. The advisory establishes the affected software and patched release, but does not by itself demonstrate exploitation against users, so investigators should distinguish browser version exposure from evidence of malicious content delivery or successful compromise.
Canada’s Cyber Centre issued an advisory on 3 November concerning a WordPress Core vulnerability affecting releases before 7.1.4, after United States authorities added CVE-2026-119977 to their Known Exploited Vulnerabilities catalogue. The alert gives defenders an evidence-backed basis for prioritising upgrades, while confirming that a weakness is exploited somewhere does not establish that any particular website was compromised without corroborating update, access and server-side artefacts.
European investigators coordinated action against a cross-border investment-fraud operation on 3 November, reporting seven arrests and the seizure or shutdown of more than 100 servers associated with fraudulent trading platforms. Eurojust said evidence from earlier investigations helped trace the suspected service providers and connected call centres, but the reported losses and international victim footprint remain investigative estimates and the individuals detained have not been convicted of the alleged conduct.
Federal prosecutors in Texas announced charges against fourteen defendants accused of participating in a nationwide bank-account takeover scheme involving alleged insiders at financial and telecommunications institutions and purported attempted fraud totalling hundreds of millions of dollars. The indictment outlines an investigative theory linking compromised identities, account access and money movements, but charges are allegations rather than findings of guilt and the precise losses must be distinguished from amounts attempted or claimed.
The United Kingdom updated its Cyber Security and Resilience Bill factsheets on 3 November, adding material on agentic artificial intelligence resilience and vendor risk management alongside revised explanations of existing proposals. The documentation outlines prospective duties and governance expectations rather than law already in force, while the associated incident-reporting provisions highlight the importance of preserving notification timelines, supplier records and technical evidence so that organisations can substantiate future regulatory disclosures.
The United Kingdom’s National Cyber Security Centre published its 2026 annual review on 3 November, drawing lessons from 337 incidents and emphasising familiar weaknesses including vulnerable internet-facing systems, credential theft and supply-chain dependencies. The review identifies logging, monitoring and preparation as recurring determinants of effective investigation, but its reported incident set reflects cases handled by the agency rather than a complete census of cybercrime or intrusions affecting the United Kingdom.
Editorial Perspective
Across this reporting window, investigators confront several kinds of compromised trust boundary: software updates, cloud model access, delegated administration and institutional identity. Reconstructing these events requires linking authenticated sessions, technical artefacts and financial activity to named accounts without presuming that an account identifier proves the human operator. Independent preservation of logs, immutable copies of configuration records and defensible timelines matters particularly when an upstream service can influence thousands of downstream systems. Assertions about automated attacks should remain separate from what command sequences and host evidence can establish.
International fraud cases and disputed breach claims show how quickly the evidential picture fragments across service providers, police jurisdictions and public disclosures. Investigative readiness depends on prompt preservation requests, agreed time standards and explicit documentation of who generated or handled each dataset. Reports should distinguish observed access, confirmed retrieval, estimated exposure and alleged criminal proceeds, rather than merging those concepts into a single impact figure. As prospective regulatory reporting duties evolve, the capacity to reproduce those distinctions from primary records will become increasingly consequential.
Reference Reading
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM