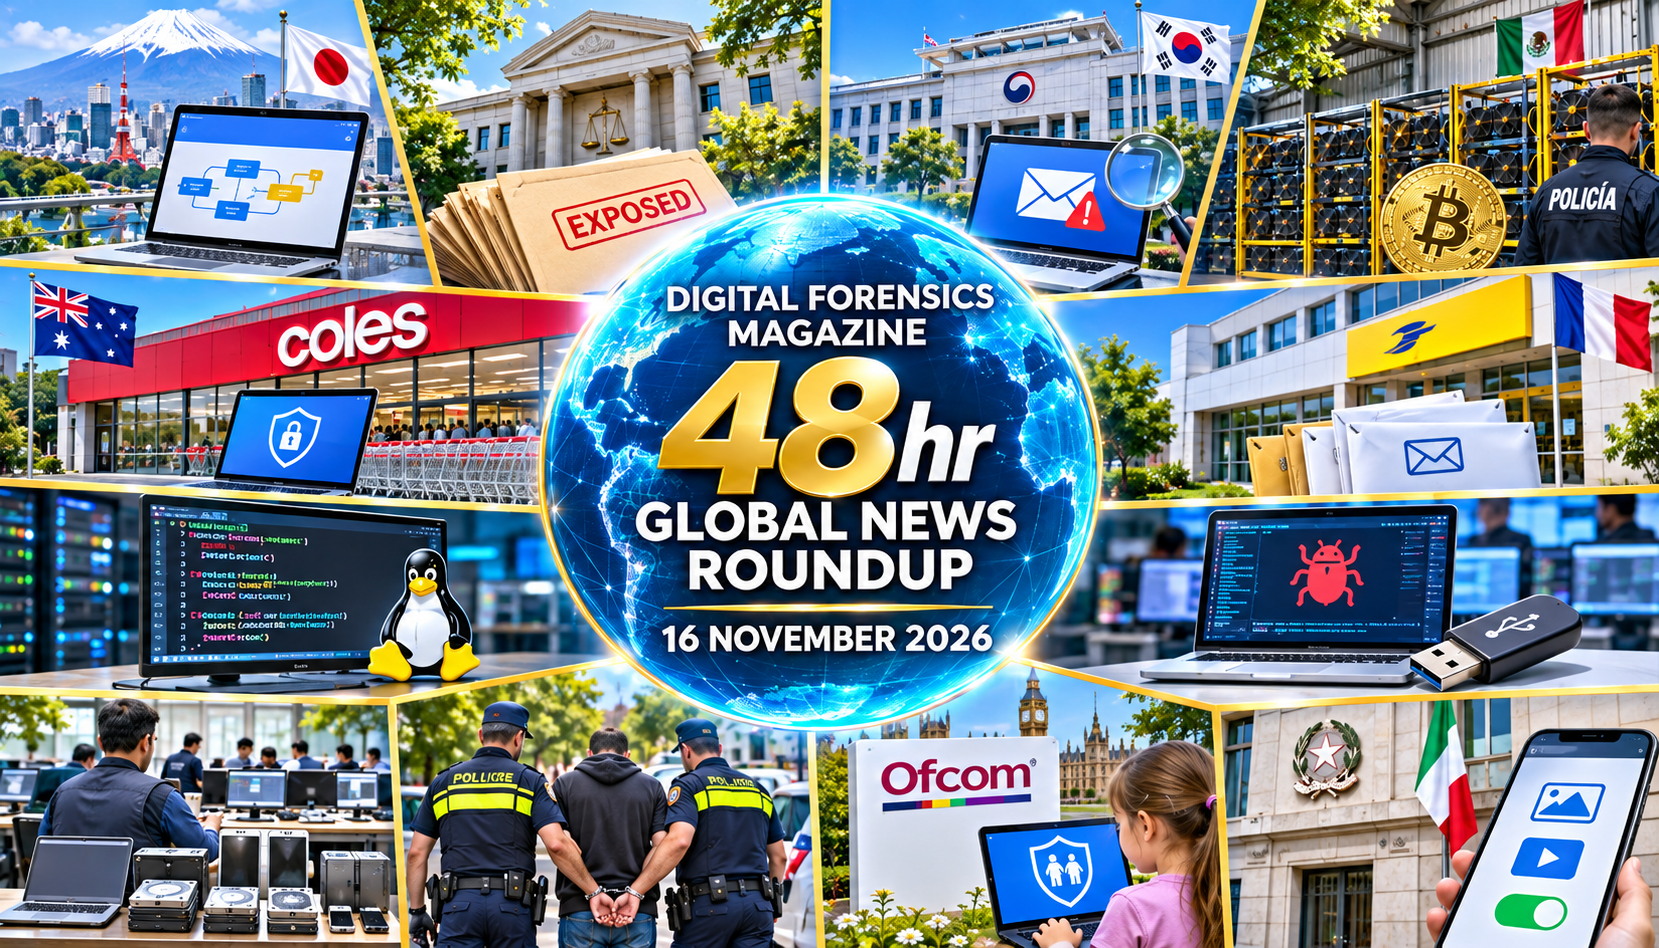

What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
Fugaku breach exposes research credential risks
Optimizely compromise traced through injected scripts
→Cyber Investigations
Google traces autonomous intrusion tooling
UK police trace repeat-victim investment fraud
→Major Cyber Incidents
Equinor reports attack on corporate IT systems
Korean attractions disclose supplier ticketing breach
→Exploits & Threat Intelligence
Oracle releases fixes for Java compiler flaw
Rwanda issues Apache HTTP/2 vulnerability warning
→Law Enforcement
Scattered Spider defendant receives six-year sentence
Indian police arrest suspect in online trading fraud
→Policy & Standards
NCSC urges boards to test investigative visibility
FCA publishes updated regulatory initiatives timetable
→On 17 November, Japan’s RIKEN published findings showing that intruders reached the Fugaku supercomputer’s internal operational network through a public status dashboard, tampered with servers and potentially accessed account details for thousands of research users. Investigators confirmed malicious programmes and attempted use of credentials against other systems, but distinguished possible exposure of stored files and keys from proven removal of research data, while the precise initial exploitation method remains under examination.
Research published on 16 November traced malicious JavaScript delivered through Optimizely Web Experimentation snippets embedded in websites belonging to numerous organisations, while the service provider separately acknowledged exploitation of a vulnerability in its platform. Report URI reconstructed the script deployment and clean-up chronology using captured website responses, providing evidence of attempted cryptocurrency address replacement and mobile exploitation without establishing that every visitor encountered or executed malicious code.
Google Threat Intelligence Group reported on 16 November that its investigations had observed adversaries adapting agentic security-testing frameworks for reconnaissance, exploitation and other stages of cyber intrusions against organisations in several regions. Its assessment distinguishes observed framework deployments and recorded activity from predictions about future autonomy, and notes that rapid automated execution can leave identifiable network and code artefacts which investigators may correlate with compromised credentials and infrastructure records.
City of London Police announced on 17 November that investigators had arrested fifteen people and searched seventeen addresses in an inquiry into an alleged recovery-fee scam targeting previous investment fraud victims across the United Kingdom. Investigators linked letters, emails and payment demands to a suspected organised group and identified approximately three thousand contacted people, although the suspected £1.5 million losses and individuals’ alleged roles remain matters for investigation rather than established judicial findings.
Norwegian energy company Equinor disclosed on 17 November that it had detected an ongoing cyberattack affecting certain information technology systems and had mobilised resources to contain the activity and restore system integrity. The company said there was no indication of stolen data and that operations and production were unaffected, leaving the intrusion method and scope unconfirmed while authorities were being informed and technical work continued.
LEGOLAND Korea Resort notified customers on 16 November that a security incident affecting its ticketing supplier accesso had allowed an unauthorised party to view some season-pass records, potentially exposing contact details and encrypted birth dates. The resort said the precise number of affected customers and individual exposure remained under investigation, while available findings had not identified exposure of payment card or bank details and the supplier had blocked the affected endpoint.
Oracle published its November 2026 security update on 17 November, listing CVE-2026-114938 among vulnerabilities affecting Java SE and GraalVM products and identifying network exposure under specified application conditions. Its risk table assigns the flaw a CVSS 3.1 base score of 8.1 and notes that exploitation depends on data reaching vulnerable component APIs, making software inventory and the actual application attack surface essential before assessing exposure or claiming compromise.
Rwanda’s National Cyber Security Authority issued a warning on 17 November concerning CVE-2026-119618, a race condition in Apache HTTP Server’s mod_http2 module that could permit remote code execution on affected installations. The advisory identifies versions 2.4.55 through 2.4.70 with HTTP/2 enabled and recommends updating to 2.4.71 or later, but describes potential exploitation rather than demonstrating that the vulnerability has been used against any named organisation.
United States prosecutors announced on 17 November that a British national had received a six-year federal prison sentence in California after pleading guilty in a conspiracy involving company intrusions, text-message phishing and cryptocurrency theft. Court filings described attacks on at least twelve companies and losses exceeding $11.6 million, with investigators linking identity manipulation and SIM swapping to digital asset transfers while a further restitution hearing remained scheduled for December.
Regional reporting on 17 November said cybercrime police in Bijnor, India, had detained a man suspected of involvement in an online share-trading fraud after immigration officials intercepted him at Delhi airport on his return from Dubai. Police linked the arrest to a previous complaint alleging losses of approximately ₹1.99 crore and an outstanding lookout notice, but the report describes an ongoing prosecution and does not establish the suspect’s criminal liability.
The United Kingdom National Cyber Security Centre published board-level guidance on 17 November arguing that monitoring alerts alone cannot establish whether an organisation could detect novel attacker techniques. It recommends hypothesis-led threat hunting supported by appropriate logs and observability, explaining that a negative hunt may still uncover missing evidence sources or weaknesses in detection coverage and should therefore inform governance and investigative preparedness.
The United Kingdom Financial Conduct Authority published the eleventh Regulatory Initiatives Grid on 17 November, mapping expected financial-sector regulatory developments across the following twenty-four months and highlighting fast-changing cyber and technology risks. The forum’s publication sets out projected implementation milestones rather than imposing new requirements itself, helping regulated organisations identify future changes affecting resilience, third-party dependencies and evidential records without mistaking planned consultations or proposals for law already in force.
Editorial Perspective
The clearest investigative distinction across these disclosures is between unauthorised access, observed misuse and independently established data extraction. Research platforms, customer-facing scripts and outsourced ticketing services produce different collections of account records, application traces and network artefacts that cannot safely be treated as interchangeable. Where organisations identify possible exposure, investigators should preserve competing hypotheses and record which logs or retained images could resolve them. This discipline is especially important when stolen credentials may enable movement from one service into another.
The enforcement and technical findings also show why investigative readiness depends on routine collection arrangements rather than retrospective reconstruction alone. Proactive examination of identity activity, externally loaded code and configuration changes can reveal evidential gaps before an intrusion becomes public. Cross-border investigations additionally require careful separation of attributed claims, forensic observations and judicially established facts. Boards and investigators should therefore prioritise verifiable provenance, meaningful retention and documented confidence levels when turning security events into defensible findings.
Reference Reading
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM