
What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
Nulab confirms Cacoo credential misuse
Brazilian court confirms leaked files
→Cyber Investigations
Korean government investigates email intrusions
Mexican authorities trace illicit cryptomining sites
→Major Cyber Incidents
Coles investigates cybersecurity incident
La Poste confirms Maileva recipient exposure
→Exploits & Threat Intelligence
NoisyTCP flaw threatens Linux availability
Retadup returns as CoffeeLoader distributor
→Law Enforcement
Pakistan cybercrime agency reports 130 arrests
Dutch police arrest impersonation suspect
→Policy & Standards
Ofcom strengthens online child-safety requirements
Italian regulator fines Meta over gallery access
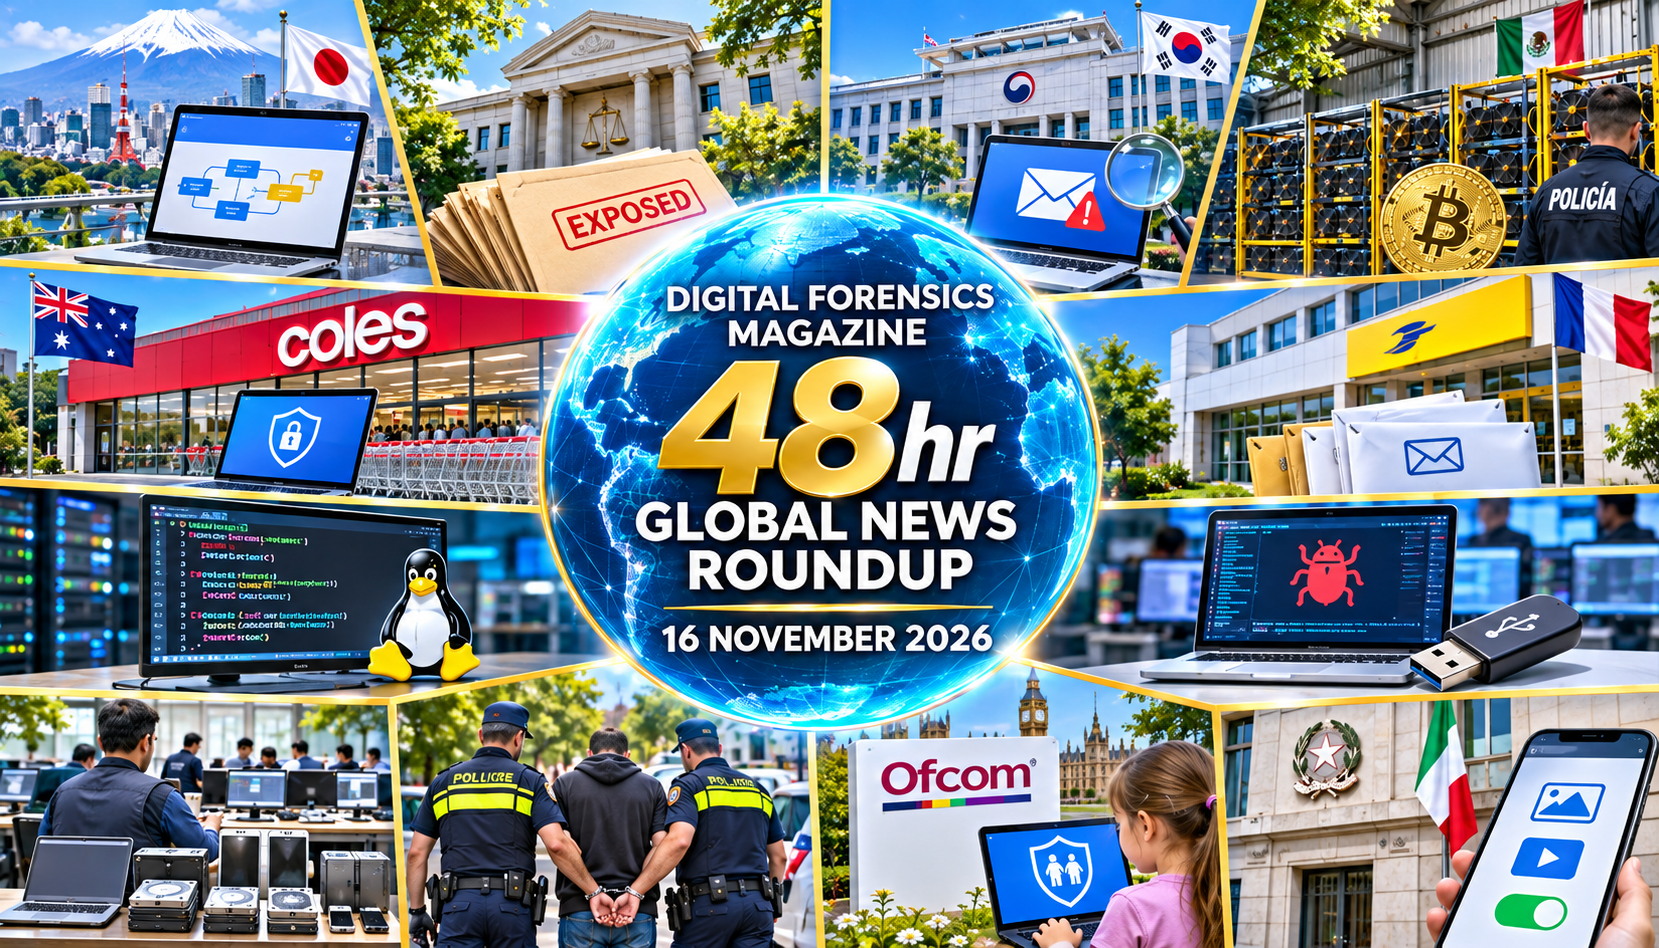
→On 16 November, Japanese software provider Nulab disclosed that an intruder had misused authentication credentials to access the operating environment of its Cacoo collaboration service on 14 November, with approximately 792 customer enquiry records confirmed as exposed. The company says the records included contact information and occasionally partial payment card details, while investigators are still establishing the full access path and scope and have not identified unauthorised access to its separately operated Backlog service.
Brazil’s Minas Gerais Court of Justice confirmed in an update circulated on 15 November that files associated with a previously disclosed cybersecurity incident had been published, a development beyond its initial acknowledgement. The court says its judicial and administrative databases remain intact while technical teams assess the leaked material, reset potentially exposed credentials, contact affected individuals and work with police and the national data-protection authority to establish the extent of disclosure.
South Korea’s Ministry of the Interior and Safety announced on 16 November that attackers had gained abnormal access to more than 300 government email accounts after moving through weaknesses in local networks and exploiting a single sign-on authentication weakness. A joint investigation involving national security and internet agencies is examining entry points, account activity, potential data loss and malware, while authorities have restricted connections between affected local networks and central email infrastructure.
Mexican reporting on 16 November examined investigations into clandestine cryptocurrency-mining installations in Puebla and Sinaloa, where police seized computing equipment and electrical infrastructure and detained at least one suspect during earlier raids. Investigators are examining allegedly stolen electricity, the provenance of equipment and possible organised-crime connections, while financial specialists caution that linking the machines to criminal proceeds requires identifying actual cryptocurrency wallets and tracing transactions rather than assuming money laundering.
Australian supermarket operator Coles Group disclosed on 16 November that it was investigating a cybersecurity incident and had engaged the Australian Cyber Security Centre and external specialists to secure its information technology environment. The company reported no evidence at that stage that customer, employee or supplier data had been compromised or removed and said its stores and online services remained operational, leaving the cause, attempted access and any wider impact subject to continuing investigation.
France’s La Poste Group stated on 15 November that a September cyberattack affecting its Maileva document-dispatch subsidiary exposed identification information concerning approximately 22 million recipients, including names and postal addresses. La Poste says it notified the French data-protection authority, informed affected client organisations and filed a criminal complaint, while the document contents and consequences for recipients require separate examination rather than assumptions about uniform data exposure.
A technical disclosure circulated on 15 November described NoisyTCP, tracked as CVE-2026-99288, a Linux kernel TCP race condition that a remote attacker may trigger before authentication on systems using multiple packet-receive processing contexts. The researcher demonstrated conditions capable of causing a kernel panic or memory corruption and identified an upstream fix, but the advisory does not establish exploitation in the wild or code execution, so assessments should distinguish demonstrable denial-of-service exposure .
Kaspersky researchers reported on 16 November that the older Retadup removable-media worm is being repurposed to distribute CoffeeLoader malware, with a modified 7-Zip library and an updated Armoury packer concealing the malicious execution chain. Their reverse engineering documents registry persistence, command-and-control communications, GPU-assisted unpacking and observable indicators that support forensic triage, while the reported infection detections represent the vendor’s visibility rather than an independently confirmed count of all compromised systems.
Pakistan’s National Cyber Crime Investigation Agency reported through regional media on 16 November that operations in Lahore had resulted in the arrest of approximately 130 suspects suspected of online fraud and call-centre offences. Investigators reported seizing numerous electronic devices and working to identify victims and reconstruct payment flows, but the figures and allegations remain attributable to the agency’s account and do not themselves establish guilt or the role of seized devices.
Dutch police announced on 15 November that officers arrested a 28-year-old man in Beverwijk after a resident reported a telephone caller posing as a national police investigator and seeking valuables under a fabricated criminal-investigation pretext. The resident kept the caller engaged while officers arranged surveillance at the proposed collection point, and investigators are now examining whether other victims were targeted, illustrating the evidential value of communications and controlled observations.
The United Kingdom communications regulator Ofcom announced on 16 November additional online-safety measures requiring covered platforms to strengthen detection and removal of child sexual abuse material, including expanded hash matching and automated tools for specified services. Subject to the parliamentary process, the new duties are expected to take effect from early 2027, raising requirements for auditable content-identification systems and careful handling of potentially evidential material without suggesting the prospective rules are already legally operative.
Italy’s data-protection authority announced on 14 November a fine of €805 million against Meta concerning access by the Facebook Android application to users’ photographs, videos and associated metadata without sufficiently specific, informed consent. The regulator says its technical examination concerned approximately 20 million Italian users and ordered changes to consent and default settings, while Meta disputes the findings and intends to appeal, pending any judicial review.
Editorial Perspective
Across this reporting window, the investigative challenge is not simply to identify an intrusion but to distinguish exposed records, accessed accounts and confirmed extraction. Government email, commercial platforms and judicial systems each create different logging and custody requirements, making reliable reconstruction dependent on preserved authentication histories, access trails and documented data provenance. Where public disclosures describe possible exposure rather than demonstrated exfiltration, investigators should preserve that distinction in both findings and notifications. Consistent documentation of evidence sources also allows later statements about scope or attribution to be tested rather than assumed.
The technical reporting reinforces the need to correlate endpoint artefacts with network, identity and third-party service records before assigning a single cause or actor. Removable-media propagation, kernel-level availability weaknesses and fraudulent communications present different evidential questions, despite sharing familiar security terminology. Enforcement and regulatory developments add another requirement: evidence-handling decisions must remain defensible when information crosses organisational or national boundaries. Sound investigative readiness therefore depends on retention arrangements, provenance records and explicit confidence levels established before an incident becomes public.
Reference Reading
- NIST SP 800-86 — Guide to Integrating Forensic Techniques into Incident Response
- RFC 3227 — Guidelines for Evidence Collection and Archiving
- MITRE ATT&CK T1078 — Valid Accounts
- NIST Cybersecurity Framework
- NIST SP 800-61 Rev. 3 — Incident Response Recommendations
- Ofcom — Online Safety Additional Safety Measures consultation
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM