
What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
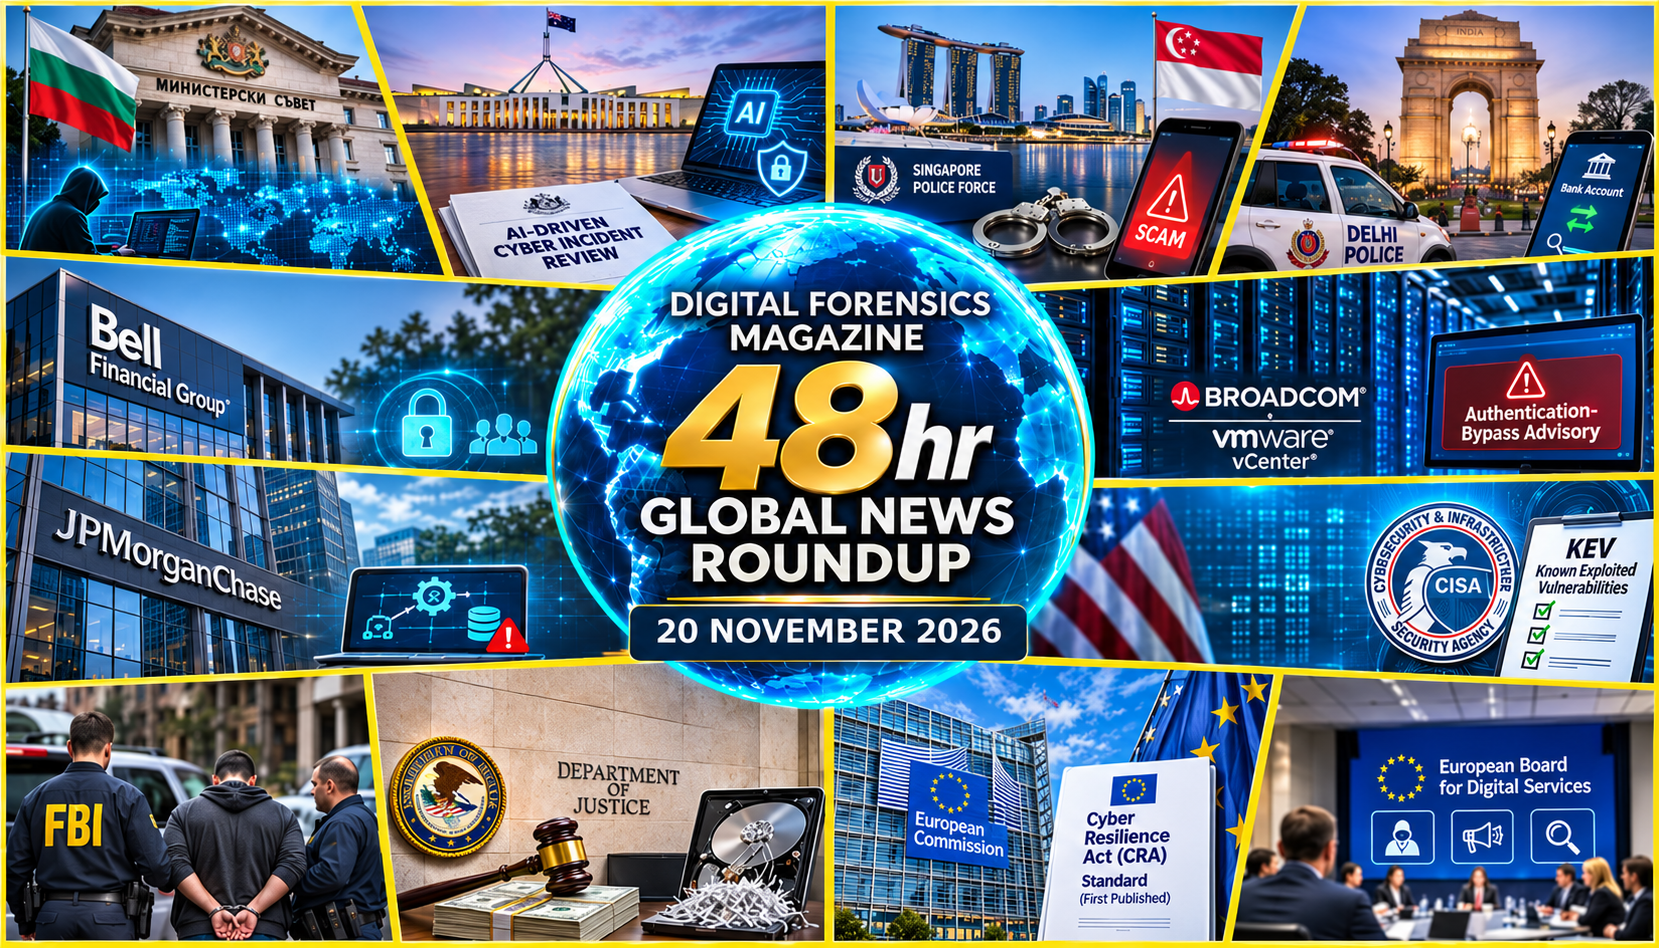
Bulgaria identifies five-year government espionage
Australia publishes AI incident review
→Cyber Investigations
Singapore investigates 235 suspected scam participants
Delhi investigators trace alleged impersonation fraud transfers
→Major Cyber Incidents
Bell Financial investigates client data access
Chase reports exposure through marketing suppliers
→Exploits & Threat Intelligence
Broadcom patches critical vCenter authentication bypass
CISA adds four actively exploited vulnerabilities
→Law Enforcement
US account-takeover operation produces coordinated arrests
Georgia prosecution alleges transfers and evidence destruction
→Policy & Standards
EU publishes first Cyber Resilience Act standard
European digital services board examines scam transparency
→On 18 November, Bulgarian officials said investigators had uncovered a five-year intrusion into government systems, reporting extraction of at least 130 gigabytes of documents from state networks and administrative databases. The authorities said monitoring introduced this year revealed the activity, while analysis of compromised servers, workstations and data-transfer records continues and officials have not established whether those responsible were independent criminals, an organised group or a foreign intelligence service.
Australia’s Department of the Prime Minister and Cabinet published its review of a cyber incident involving an AI agent and a Services Australia public statistics service on 20 November, with eighteen accepted recommendations. The review examines vulnerability disclosure, escalation between agencies and the evidence required to establish what information was accessed, concluding that clearer reporting triggers and cross-government coordination are needed for future AI-related incidents.
Singapore police said on 19 November that 235 people were under investigation following a two-week operation involving Cyber Command and seven police divisions, linked to more than 536 suspected scam cases and reported losses of about S$4.2 million. The inquiry covers alleged money-mule activity and impersonation, phishing, employment and investment fraud, requiring investigators to correlate victim reports, communications, account movements and individual conduct before any particular suspect’s responsibility can be established.
Delhi Police investigators arrested three suspects in Lucknow in a case reported on 19 November concerning alleged digital-arrest impersonation of a 66-year-old victim and transfers totalling approximately ₹2.02 crore. Investigators reportedly traced beneficiary bank accounts and recovered mobile telephones, debit cards and a cheque book, although the precise roles of other network members and the criminal allegations remain subject to further inquiry and judicial determination.
Australian financial services company Bell Financial Group disclosed on 20 November that an unauthorised party accessed a limited number of its information technology systems and that some client data was believed to have been accessed. The company said the incident was contained, client assets remained safe and operations continued, while specialist investigators assessed the scope and notifications were made to national cyber, police and privacy authorities.
JPMorgan Chase confirmed on 19 November that third-party vendors had been targeted in a cyberattack involving marketing data, with some customer names and email addresses potentially exposed in America. The bank distinguished this incident from a separate service outage earlier in the week, while reports of leaked contact information and statements by other affected payment organisations highlight the need to verify supplier-level access, the actual records obtained and individual notification scope.
Broadcom published security advisory VMSA-2026-0009 on 19 November for VMware vCenter, SDDC Manager and VMware Tools, including CVE-2026-123890, an authentication-bypass vulnerability affecting the VMware Directory Service with a maximum CVSS score of 9.8. The vendor says a network-connected attacker could gain unauthorised access and lists fixed product versions without a workaround, making version inventories, exposure assessment and preserved authentication and management activity vital to evaluating any suspected exploitation.
The United States Cybersecurity and Infrastructure Security Agency added four vulnerabilities to its Known Exploited Vulnerabilities catalogue on 18 November, covering Synology DiskStation Manager, BerriAI LiteLLM, Apache Axis and Vanderbilt University REDCap software. CISA says the additions are supported by evidence of exploitation, rather than by severity scoring alone, and affected organisations should reconcile actual deployments, patch status and relevant system logs before determining whether any particular environment was attacked.
United States prosecutors announced on 18 November that five people were arrested in Florida in a federal inquiry into alleged account-takeover fraud associated with losses exceeding $54 million across more than sixty-five financial institutions. A Miami defendant faces charges concerning thirty-two allegedly fraudulent outgoing transfers, while investigators must distinguish the broader nationwide loss estimate from transactions attributed to particular suspects and present authenticated account, communications and banking records in court.
US prosecutors announced on 19 November that a Georgia resident faced criminal charges of international money laundering and destroying evidence following an FBI investigation into alleged transfers exceeding $26,000 to people or groups linked to ISIS. Prosecutors said agents searched electronic devices and other locations following the suspect’s arrest, but the reported financial links, alleged destruction and individual responsibility remain prosecutorial allegations requiring evidential testing and adjudication.
The European Commission said on 19 November that the first standard supporting the Cyber Resilience Act had been published, establishing generic cybersecurity principles for products with digital elements across development, operation and decommissioning. The standard helps manufacturers document product risks, security processes and lifecycle decisions, although further product-specific standards remain under development and publication alone should not be mistaken for a new enforcement deadline or immediate certification requirement.
The European Board for Digital Services met in Brussels on 19 November and discussed online fraud, advertising transparency, a prospective code of conduct on scams and incident and crisis procedures under the Digital Services Act. The Board welcomed planned Commission guidelines to improve advertising-library consistency and independent scrutiny, while its programme remains development rather than evidence that proposed measures are already binding or that individual platform misconduct has been established.
Editorial Perspective
The disclosures underline how often the decisive investigative question is not whether an alert was raised, but which records can substantiate an account of access, extraction and subsequent misuse. Government networks, financial service providers and third-party marketing platforms each retain different authentication, application and transaction artefacts. Preserving provenance and collection timestamps across those environments is essential if apparently related activity is to be correlated without overstating attribution. Investigators should also distinguish confirmed compromise from technical exposure and from allegations based on incomplete evidence.
As automation becomes more capable, the quality of disclosure and escalation processes increasingly determines whether an organisation can reconstruct a meaningful sequence of events. A durable investigation requires access to historical logs, documented changes, verified source material and a clear record of investigative uncertainty. Cross-border fraud cases additionally depend on dependable links between communications, accounts and devices rather than loss figures alone. Decision-makers should test those evidential dependencies before an incident, and ensure that policy obligations translate into usable records rather than merely completed compliance paperwork.
Reference Reading
- NIST SP 800-61 Rev. 3 — Incident Response and Risk Management
- MITRE ATT&CK T1199 — Trusted Relationship
- RFC 3227 — Guidelines for Evidence Collection and Archiving
- NIST — Cybersecurity Framework 2.0
- CISA — Known Exploited Vulnerabilities Catalogue
- Australian Government — AI Incident Review Recommendations
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM