
What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
OPAN completes forensic review of appeal email
Joyner phishing inquiry finds no compromise
→Cyber Investigations
Lahore raid yields 80 devices for examination
₹3.4 crore fraud traced through 8,574 accounts
→Major Cyber Incidents
Ahold Delhaize takes systems offline
St Andrew’s confirms patient-data download
→Exploits & Threat Intelligence
SonicWall flaw moves to observed exploitation
Critical Floci flaw enables remote commands
→Law Enforcement
Singapore charges six over money-mule activity
Ghana arrests eight in alleged fraud operation
→Policy & Standards
US restores UK access to pre-release AI models
EU digital simplification talks postponed
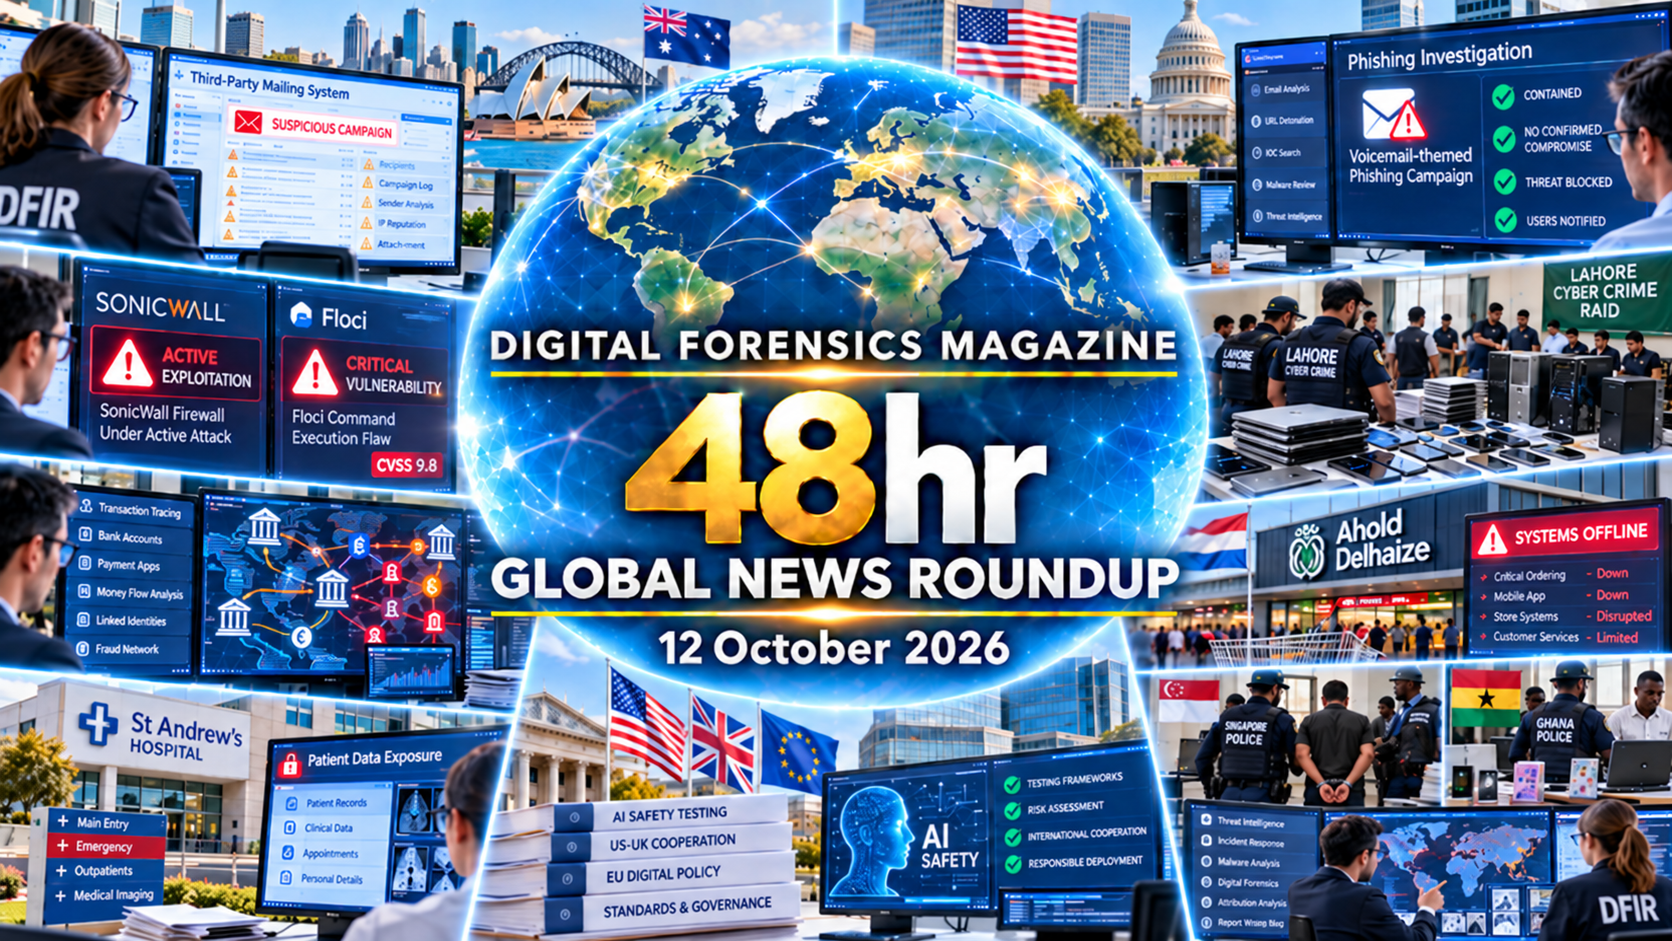
→OPAN said on 12 October that independent forensic investigators, legal advisers and cyber specialists had completed their examination of an unauthorised fundraising email sent through a third-party mailing system to its Australian mailing list. The organisation said it strengthened security after the inquiry and is contacting a small number of people where privacy laws require notification, narrowing the confirmed consequences of the September incident.
Joyner Companies said its investigation into a voicemail-themed phishing campaign affecting US staff between 8 and 10 October had identified and blocked the malicious sending infrastructure. Account reviews found no evidence of unauthorised access, credential compromise or customer and partner data exposure, while additional email safeguards were implemented, providing a documented endpoint to the investigation rather than leaving exposure assumptions unresolved.
Pakistan’s National Cyber Crime Investigation Agency arrested 37 people during a Lahore raid on a call centre allegedly used to defraud victims in the United States and Canada through fake mobile-phone sales. Investigators seized 40 laptops, 35 mobile phones and five CPUs for forensic examination, while the alleged use of VoIP services and captured payment-card details gives the inquiry multiple device, communications and transaction evidence sources.
Chennai cybercrime investigators traced money from an alleged ₹3.4 crore investment fraud through 8,574 bank accounts spanning multiple institutions and payment applications, leading to one arrest. Police said the trail extended through about 20 transactional layers and 150 banks, illustrating the evidential challenge of reconstructing rapid fund movements across fragmented financial platforms while preserving links between the original victim payments and downstream accounts.
Ahold Delhaize said on 12 October that it was assessing a security issue within its network and had taken some systems offline as a precaution while stores remained open. Independent regional reporting showed disruption to websites, apps, customer service and online deliveries at several Dutch brands, but the company had not publicly established the cause or confirmed data exposure, leaving operational scope and evidential findings still under investigation.
A forensic investigation at St Andrew’s Hospital in South Australia confirmed that an intruder downloaded a subset of patient data after the hospital isolated systems and tightened controls. The hospital began contacting affected people and notified the Australian Cyber Security Centre and privacy regulator, turning an initially suspected incident into a confirmed data-loss finding whose precise records, access path and downstream misuse remain important investigative questions.
Security researchers reported exploitation attempts against SonicWall SMA1000 appliances using CVE-2026-102255, a critical pre-authentication server-side request forgery flaw disclosed on 6 October. The observed activity is a material development beyond the earlier vulnerability alert, changing the evidential question from whether systems were merely exposed to whether logs, appliance telemetry and network traces show attempts or successful unauthorised operations against unpatched devices.
CVE-2026-108598, published on 10 October, affects Floci versions before 2.2.0 and allows unauthenticated command execution through unrestricted Velocity mapping templates in the VtlTemplateEngine. The record carries a critical CVSS score and identifies version 2.2.0 as the fixed release, giving investigators a clear version boundary while also distinguishing technical exploitability from evidence that any particular deployment has actually been compromised.
Singapore Police arrested four men and two women aged 23 to 40 for alleged involvement in scam-related money-mule activity, with charges scheduled between 12 and 16 October. Investigators said the conduct included relinquishing bank accounts, transferring funds, disclosing Singpass credentials and supplying fraudulently registered SIM cards, creating linked banking, identity, device and telecommunications evidence that can help reconstruct how criminal syndicates moved proceeds and enabled scams.
Police in Ghana’s Bono Region arrested eight people after an alleged assault connected with initiation into an internet-fraud operation, according to regional reporting on 11 October. Preliminary inquiries allege the group used downloaded images of foreign military personnel to impersonate soldiers serving in Yemen and solicit money, giving investigators potential image provenance, account, communications and payment evidence to test the suspects’ statements and identify any victims.
Reuters reported on 11 October that the US administration reversed earlier guidance that had discouraged American AI developers from providing pre-release models to the UK’s AI Security Institute for safety testing. The policy shift restores a cross-border evaluation route for frontier systems, making testing records, model-access conditions and incident-reporting arrangements more important evidence of what was assessed before deployment and how identified security risks were handled.
EU negotiations on the digital simplification package were removed from the 11 October ambassadors’ agenda, with no replacement date or revised text prepared, according to MLex. The package affects the direction of several digital compliance regimes, so the postponement leaves organisations without a settled negotiating position and reinforces the need to preserve evidence against current obligations rather than assuming proposed simplifications will change regulatory requirements on a predictable timetable.
Editorial Perspective
Across this cycle, the most useful investigative signal often comes from organisations that move beyond the initial disclosure and publish what their examination actually established. Confirming whether data was downloaded, accounts were compromised or exploit attempts were observed changes the evidential question from hypothetical exposure to demonstrable activity. That distinction depends on preserving logs, device images, identity records and third-party telemetry before containment or recovery alters them. Investigative readiness therefore means knowing in advance which systems can supply trustworthy evidence and how those records will be correlated.
Several stories also show how investigations increasingly cross organisational and jurisdictional boundaries, from multi-layer bank transfers and SIM credentials to supplier platforms and internet-facing appliances. Attribution is strongest when technical indicators can be connected to transaction records, account ownership, communications and independently preserved infrastructure evidence rather than treated as isolated clues. Policy changes around AI and digital regulation add another evidence problem: organisations may soon need to demonstrate not only what autonomous systems did, but what safeguards, oversight and near-miss records existed at the time. Building those records now improves both investigative confidence and the ability to explain decisions later.
Reference Reading
- NIST SP 800-61 Rev. 3 — Incident Response Recommendations and Considerations for Cybersecurity Risk Management
- NCSC — Plan your cyber incident response processes
- CISA — Known Exploited Vulnerabilities Catalog
- NCSC — Recovering from a highly disruptive cyber attack
- NIST SP 1347 — Cybersecurity Framework 2.0 Informative References Quick-Start Guide
- NIST IR 8374 Rev. 1 — Ransomware Risk Management: CSF 2.0 Community Profile
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM