
What’s in this roundup?
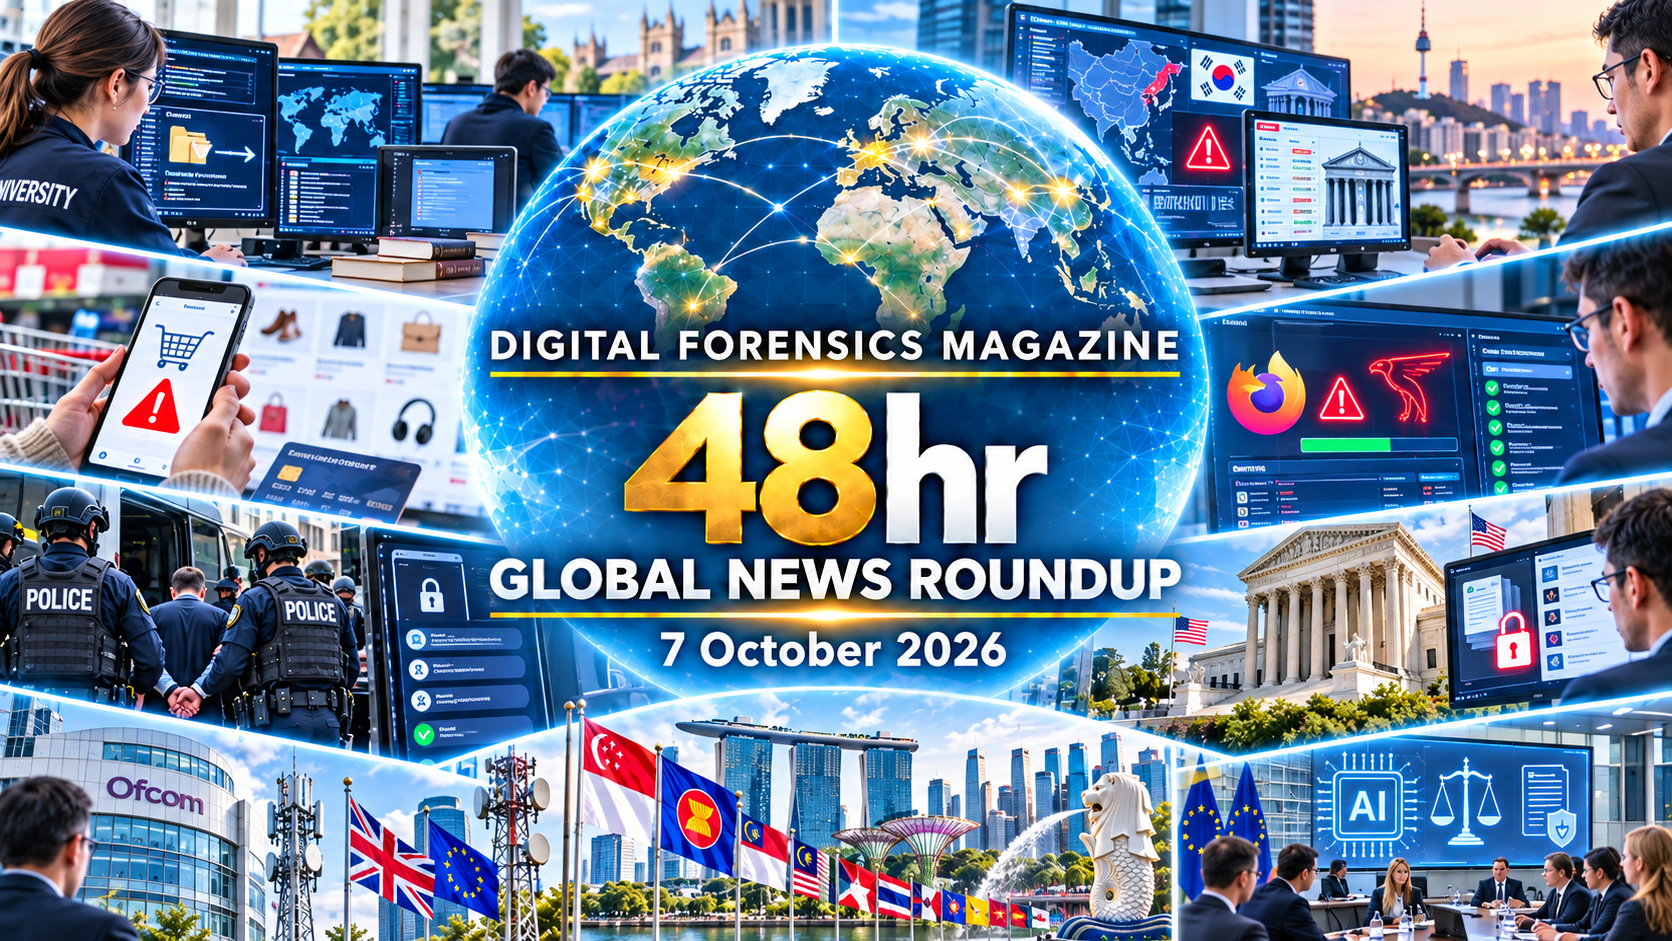
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
On-scene forensics supports Fonthill arrest
Publica supplier data leak investigated
→Cyber Investigations
Decoy evidence drives luring investigation
Mule network tracing reaches guilty plea
→Major Cyber Incidents
Ransomware disrupts 495 IDCF customers
Church examines 850,000-record exposure
→Exploits & Threat Intelligence
SonicWall SMA1000 flaw scores 10.0
NetScaler RCE risk triggers urgent alert
→Law Enforcement
SIM-swap crypto fraudster jailed
Flax Typhoon tools and domains seized
→Policy & Standards
NIST revises SHA-3 derived functions
NIST maps O-RAN security controls
→Niagara Regional Police executed a search warrant at a Fonthill residence on 8 October after an investigation by its Internet Child Exploitation Unit identified a suspect in a child sexual abuse material case. Police said an on-scene digital forensic examination supported the arrest of a 46-year-old man, who faces charges including accessing, possessing and making such material available.
Swiss authorities confirmed a data leak after a cyberattack on an external software supplier used by the Federal Pension Fund Publica, with the affected company and federal bodies still determining the scope of exposed information. The Office of the Attorney General has opened an investigation, making preservation and correlation of supplier, customer and government records central to establishing what data was accessed or removed.
Niagara Regional Police took over an online child-luring investigation after a third-party decoy group confronted a Niagara Falls resident and handed its evidence to officers on 7 October. Detectives from the Internet Child Exploitation Unit arrested a 36-year-old man the following day, with the provenance and handling of externally collected digital evidence likely to be important as the criminal case progresses.
Oleg Korniev, a Ukrainian-Russian dual citizen, pleaded guilty in the United States to running an international laundering organisation used by cybercriminals, which prosecutors say recruited more than 15,000 US money mules. The FBI investigation traced at least $10 million stolen from over 750 bank accounts, illustrating how financial records, mule networks and cross-border evidence can connect cyber intrusions to the movement of criminal proceeds.
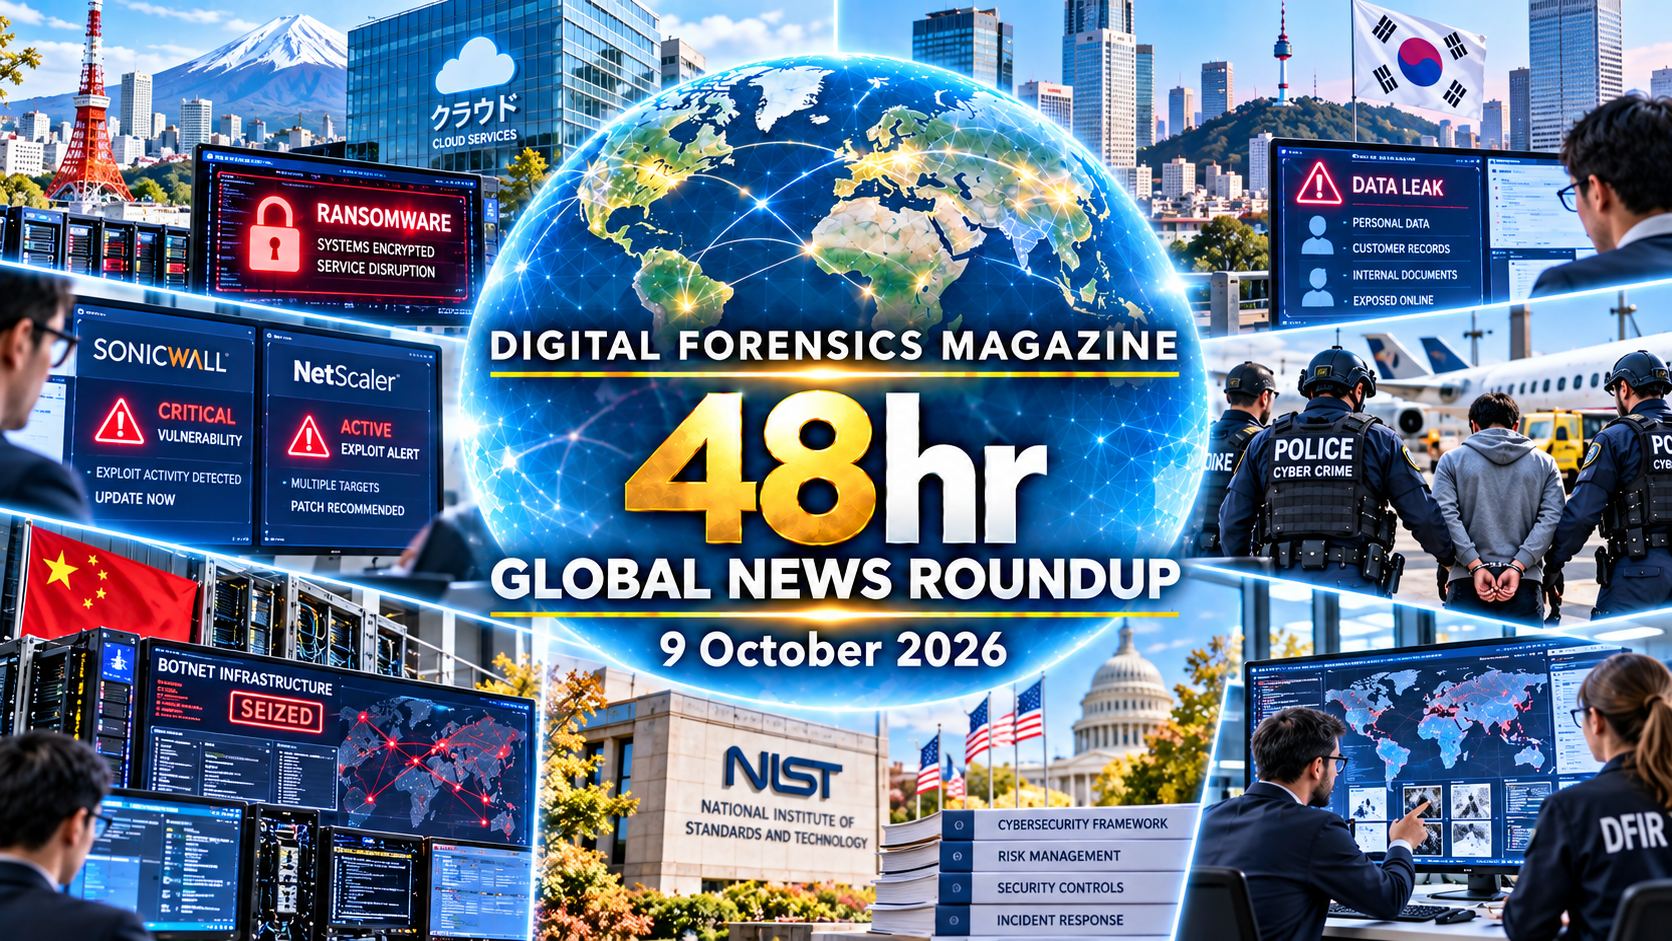
IDC Frontier said unauthorised access involving ransomware disrupted parts of its IDCF Cloud East Japan Region 1 service from 7 October, stopping virtual servers and preventing some restarts for 495 companies and local authorities. The provider said affected-zone data may be difficult to retrieve or restore, leaving customer-held backups as an important recovery route while the scope and cause of the intrusion remain under investigation.
South Korea's Yoido Full Gospel Church said circumstances indicate personal information relating to about 850,000 members may have leaked after KISA alerted it to suspected unauthorised access, prompting emergency inspections and access restrictions. The church is considering a police investigation, while analysis of system access logs and suspected leaked data will be central to confirming the affected records, intrusion path and actual scale of exposure.
NHS England Digital warned that four vulnerabilities affect SonicWall SMA1000 appliances, including CVE-2026-102255, an unauthenticated server-side request forgery flaw carrying a CVSS score of 10.0. The alert identifies affected software releases and directs organisations to apply vendor updates, giving investigators and defenders concrete version evidence to determine exposure while avoiding assumptions that vulnerable appliances were necessarily compromised.
NHS England Digital issued a high-severity alert for CVE-2026-107406, a memory-overflow vulnerability that can permit remote code execution or denial of service on affected NetScaler ADC and Gateway appliances using SAML authentication. The advisory lists vulnerable and fixed releases and notes that exploitation is considered likely, making configuration state, version history and edge-device logs important evidence when assessing whether an organisation was exposed or attacked.
A London man who used SIM-swapping to help steal almost £200,000 in cryptocurrency was sentenced to two and a half years in prison on 8 October after pleading guilty to fraud and transferring criminal property. City of London Police said further evidence led to his re-arrest in 2023, showing how telecommunications, account-control and cryptocurrency records can sustain a prosecution years after the original arrest.
The US Justice Department and FBI seized seven domains supporting the Microscan and FishHub tools used in cyber operations that authorities associate with China's Integrity Technology Group and the activity known as Flax Typhoon. Court documents allege the infrastructure scanned and compromised networks, while confirmed FishHub victims included about 20 Taiwanese universities, providing investigators with seized infrastructure and technical indicators for continuing international attribution work.
NIST released a draft revision of Special Publication 800-185 on 8 October, updating SHA-3 derived functions including cSHAKE, KMAC, TupleHash and ParallelHash and opening public comment until 7 December. The revision introduces streaming interfaces for extendable-output functions, a change relevant to implementers and investigators who rely on consistent cryptographic processing, validation and reproducibility when protecting or verifying digital evidence and security tooling.
NIST published two reports on Open Radio Access Network security on 8 October, including a final report on RAN Intelligent Controller security and a draft Cybersecurity Framework profile for US federal O-RAN deployments. The work maps authentication, authorisation and confidentiality controls to risk-management outcomes, giving investigators and security teams a structured basis for assessing configuration, control evidence and security responsibilities across complex 5G environments.
Editorial Perspective
Across this cycle, the strongest investigative value comes from evidence that can be correlated across systems rather than from any single alert, disclosure or allegation. Search-warrant examinations, cloud-service records, access logs, financial trails and seized infrastructure each provide different parts of the evidential picture, but their usefulness depends on preserving provenance and timing. Third-party services again feature prominently, meaning investigators may need evidence held outside the directly affected organisation. Cross-platform correlation should therefore be planned before data is lost, overwritten or dispersed across jurisdictions.
Attribution also remains a matter of evidential discipline: infrastructure seizures and guilty pleas can materially strengthen a case, while vulnerability disclosure alone does not demonstrate compromise. Version history, configuration state and retained telemetry are essential for distinguishing theoretical exposure from observed activity. The same principle applies to large breach claims, where affected-record estimates should remain qualified until log analysis and data comparison establish scope. Investigative readiness increasingly depends on retention, lawful access, chain-of-custody controls and the ability to reconcile technical evidence with financial, identity and provider records.
Reference Reading
- NIST SP 800-86 — Guide to Integrating Forensic Techniques into Incident Response
- NIST SP 800-61 Rev. 3 — Incident Response Recommendations and Considerations
- NCSC — Introduction to logging for security purposes
- ISO/IEC 27037 — Guidelines for identification, collection, acquisition and preservation of digital evidence
- NIST Cybersecurity Framework 2.0
- NIST SP 800-101 Rev. 1 — Guidelines on Mobile Device Forensics
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM