Critical Infrastructure
Telco Resilience
 admin
13/05/2026
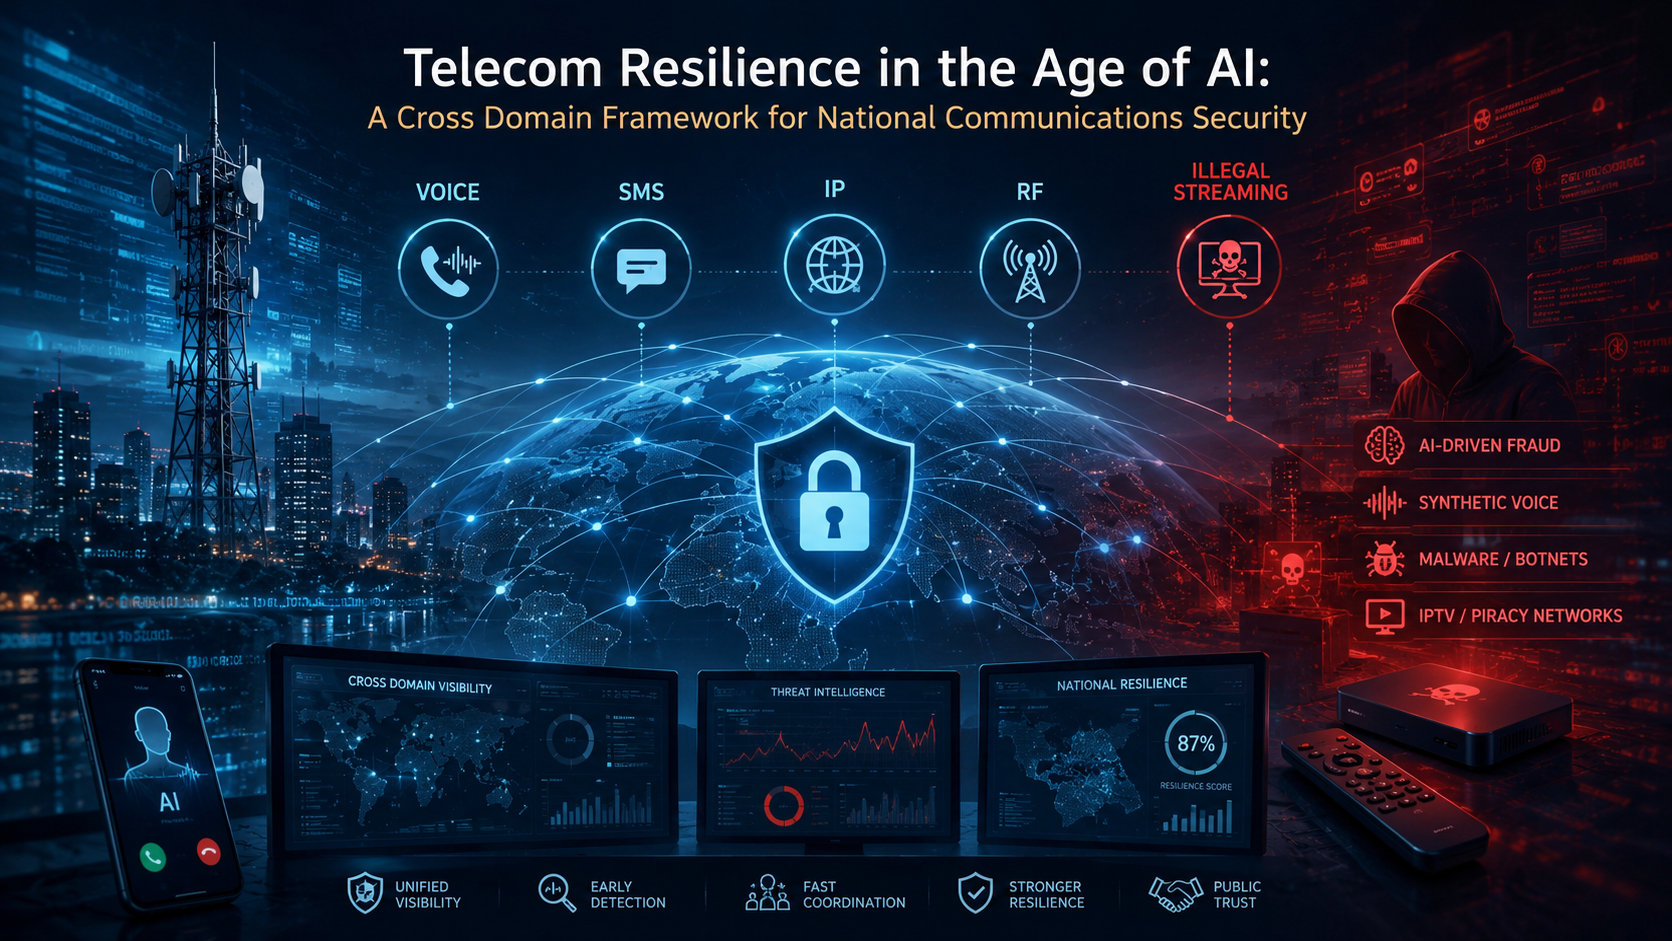
Telecommunications networks are facing a new generation of AI-driven threats spanning Voice, SMS, IP, RF, and illegal streaming infrastructure. This briefing examines the convergence of telecom fraud, compromised IPTV ecosystems, AI-enabled attack automation, and cross-domain resilience failures, highlighting the operational, regulatory, and national security implications for carriers, regulators, DFIR professionals, and critical infrastructure stakeholders operating within increasingly interconnected communications environments.

NEWS ROUNDUP – 4th May 2026
admin
04/05/2026
Investigations span exposed property records in Tasmania, stolen Canvas student data, and a breach affecting Asian football organisations. Authorities warn of cyber-enabled cargo theft, while researchers link Shadow-Earth-053 to infrastructure targeting. Active cPanel exploitation and OAuth abuse campaigns expand attack surfaces, as new guidance highlights risks from autonomous AI systems and investigative challenges in evidence attribution.
NEWS ROUNDUP – 2nd March 2026
admin
02/03/2026
CISA updated hunting guidance for RESURGE malware lingering on Ivanti appliances, while Juniper warned of a critical PTX router takeover flaw. Reuters tracked cyber operations hitting Iranian apps and sites after strikes, as Sophos monitored Iran-linked hacktivist claims. In the US, UH Cancer Center reported SSN exposure affecting up to 1.15 million people. Substack disclosed stolen emails and phone numbers.
NEWS ROUNDUP – 27th February 2026
admin
27/02/2026
Joint NSA-partner guidance and an NHS alert urge urgent hunting and hardening for actively exploited Cisco Catalyst SD-WAN flaws. Dutch telco Odido reports attackers publishing stolen customer data, while ManoMano notifies 38 million users after a third-party breach. Trend Micro patched critical Apex One console RCE. DOJ says scam-center crypto freezes exceeded $580m. EU advanced an undersea cable protection plan.
NEWS ROUNDUP – 26th January 2026
admin
26/01/2026
Microsoft issued out-of-band Windows fixes for Outlook freezes and probed post-update boot failures as investigators tracked Cambodia-based scam networks repatriated to South Korea. ESET tied Sandworm to a DynoWiper power-sector attempt, while Fortinet and CISA warned on FortiCloud SSO abuse and exploited vCenter flaws. Policy moves spanned NHS supplier assurance, Australian smart-device rules, and Korean breach scrutiny in this window.