
What’s in this roundup?
Select a section to explore both featured developments and their original sources.
Digital Investigations
FTC challenges claimed sextortion investigation services
Icon Oncology Group investigates supplier data exposure
→Cyber Investigations
Delhi police trace international digital arrest fraud
Korean regulator widens financial hacking inquiry
→Major Cyber Incidents
Cyber incident disrupts UK fashion retailers
French supermarkets lose refrigerated stock to cyberattack
→Exploits & Threat Intelligence
Firefox 158 fixes sandbox and memory flaws
Canadian cyber agency flags Fortinet fixes
→Law Enforcement
OpenAI employee charged over concealed recorder
West African scam operation yields arrests
→Policy & Standards
Singapore publishes national cybersecurity strategy
Singapore proposes professional accreditation framework
→The US Federal Trade Commission filed a complaint on 13 October alleging that an operator selling sextortion assistance misrepresented its digital investigation services, including promises to trace offenders, document findings and report crimes to police. The regulator alleges that some supposed investigative reports contained fabricated information and that promised work was not completed, raising questions about the authenticity, auditability and independent verification of evidence supplied to distressed victims.
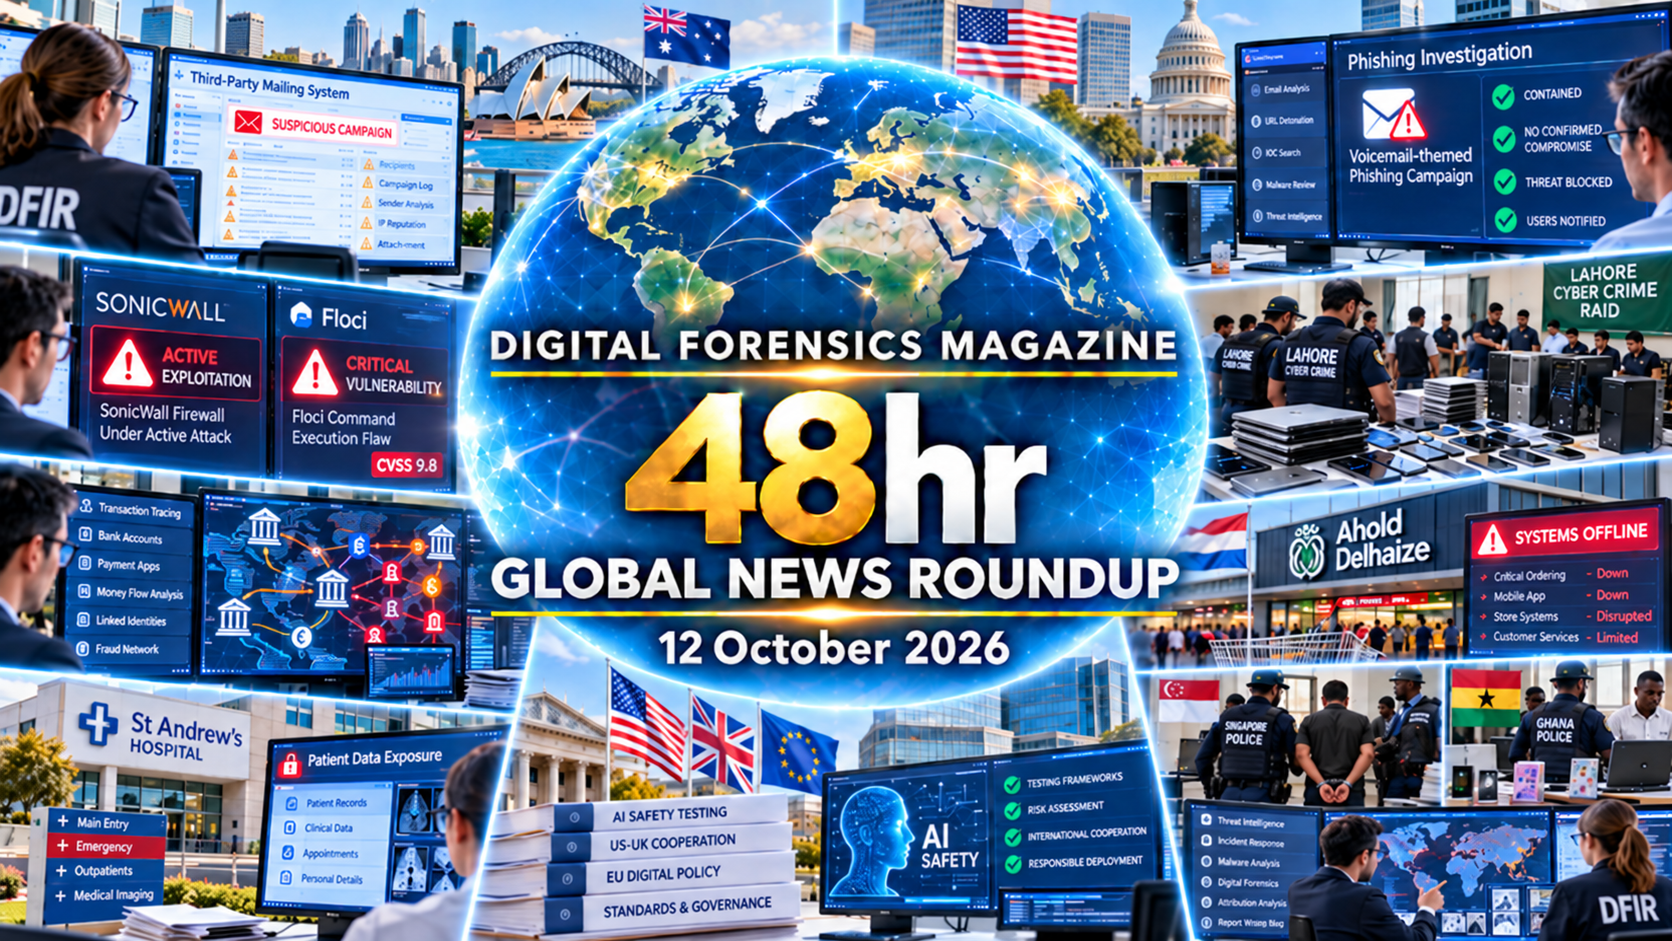
Australia’s Icon Oncology Group disclosed on 12 October that an intruder had accessed patient-related information held in a supplier’s system, prompting forensic specialists to examine the incident and the organisation to notify police and regulators. The provider said it had obtained the affected records and was determining which patients and documents were involved, while stressing that its own systems remained operational and that the material did not appear to comprise complete patient files.
Delhi Police in India announced on 13 October that investigators had arrested 11 suspects in an alleged digital-arrest fraud network with links to handlers in Cambodia and other Southeast Asian countries. Investigators reported connecting the operation with multiple complaints and freezing funds in linked bank accounts, illustrating how cross-border attribution depends on matching victim statements, communications, identity records and transaction trails rather than treating transfers as proof of individual culpability.
South Korea’s Financial Services Commission reported on 14 October that hacking incidents had affected 16 financial institutions, with around 100,000 suspected exposures of personal information across the sector. Officials said investigators were examining intrusion methods and possible use of artificial intelligence, while the still-developing victim and record counts require correlation of affected-company logs, compromised accounts and notifications before a common attacker or mechanism can be asserted.
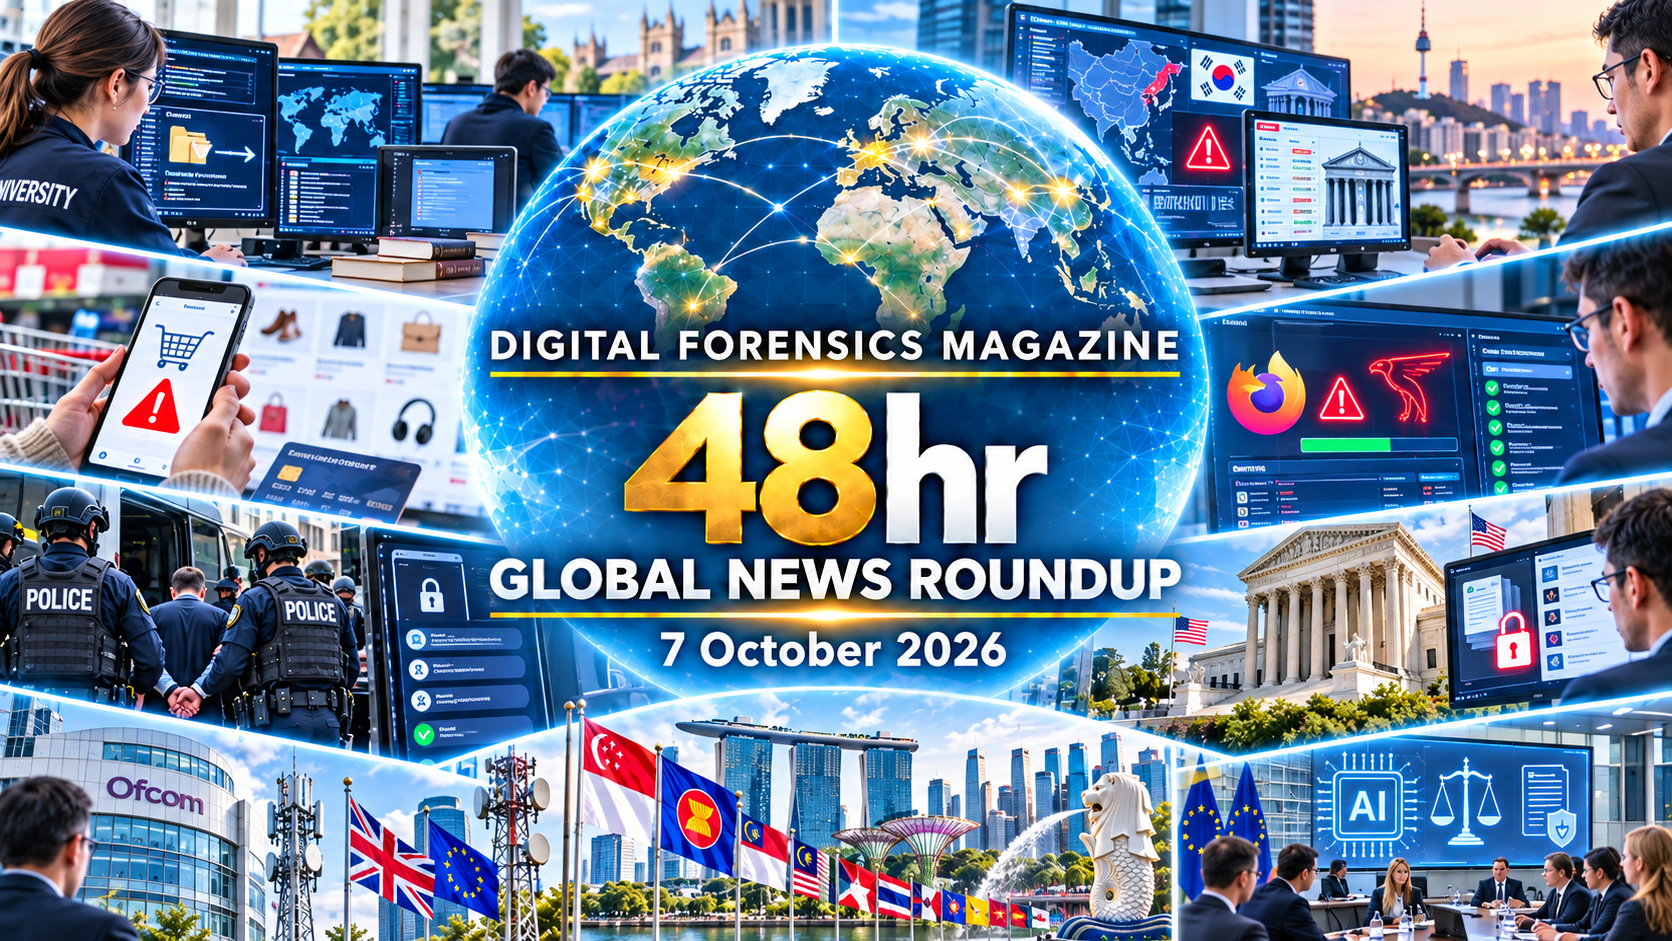
The Foschini Group disclosed on 13 October that a cybersecurity incident had affected IT systems supporting its UK fashion brands Hobbs, Whistles and Phase Eight, with online services and some orders disrupted. The group said it had no reason to believe payment information was at risk while external specialists assessed the incident, leaving the precise entry point, affected systems and any wider exposure to be established through technical examination and customer notification decisions.
French investigators said on 13 October that cyber intrusions into connected refrigeration controllers had disrupted cooling equipment at hundreds of supermarkets, forcing stores to discard spoiled food. Reporting identified obsolete or poorly protected control software as a suspected pathway, but neither a responsible group nor a definitive motive had been established, and the extent of the affected estate remains subject to investigation across separate retailers and equipment suppliers.
Mozilla issued its Firefox 158 security advisory on 13 October, identifying high-impact vulnerabilities including privilege escalation, sandbox escape, use-after-free defects and JavaScript engine weaknesses across several browser components. The advisory identifies the corrected release and individual CVE records, giving organisations an evidence-based patch boundary while investigators must still look for local signs of exploitation rather than infer compromise from the presence of a vulnerable browser version alone.
The Canadian Centre for Cyber Security published a Fortinet advisory on 13 October covering affected management, analysis, mail and security products with identified vulnerable software branches. The notice directs administrators to vendor fixes for issues including SQL injection and access-control weaknesses; exposure inventories, configuration histories and contemporaneous access logs remain necessary to determine whether a vulnerable installation was reachable or misused, as an advisory does not by itself establish active exploitation.
US prosecutors announced on 13 October that an OpenAI employee had been charged after investigators found a concealed encrypted audio recording device in an executive conference room in San Francisco. The criminal complaint cites surveillance footage, chatbot enquiries and a second recovered device as investigative material, but the allegations have not been proved in court and the company reported no indication that model weights, source code or customer data were improperly accessed or extracted.
The US Department of Justice reported on 13 October that a multinational disruption targeting West African online scam networks resulted in 28 arrests and the identification of trafficking victims, alongside widespread removal of fraudulent accounts. Authorities also described device seizures and cooperation with technology companies, while the investigative value of the operation depends on preserving account histories, electronic exhibits and financial traces that connect particular suspects to individual victims and offences.
Singapore’s Cyber Security Agency launched Cybersecurity Strategy 2026 on 13 October, setting out government priorities for critical infrastructure defence, wider ecosystem security, emerging AI and quantum risks, international cooperation and professional capability. The strategy places greater emphasis on coordinated national capabilities and improved standards, providing a policy framework against which future information-sharing arrangements, investigative authority, evidence exchange and organisational assurance commitments can be evaluated as practical measures are introduced.
Singapore’s Cyber Security Agency announced on 13 October that it is developing a national professional accreditation framework to recognise cybersecurity competence, practical experience and professional conduct, with a voluntary pilot planned for 2027. The proposal may help organisations distinguish declared qualifications from assessed capability, although the eventual value for digital investigations will depend on published criteria for evidential methods, independent assessment, continuing competence and accountability rather than accreditation labels alone.
Editorial Perspective
Investigative confidence depends on separating reported impact from findings established through recoverable evidence. This cycle brings renewed attention to the integrity of investigative reports, the provenance of digital communications and the reliability of technical disclosures. Cross-border enquiries require defensible links between devices, accounts, operators and financial flows. Those links cannot be assumed from proximity, association or untested attribution claims.
Organisations should therefore retain source-system logs, contemporaneous configuration records, communications metadata and documented custody of recovered devices wherever lawful and proportionate. External providers need clear evidential standards because an impressive-looking report may not reflect genuine investigative work. Authorities and private platforms can improve attribution by recording which observations were independently verified and which originated with a complainant or third party. Regulatory and professional initiatives will be most valuable where they make those obligations testable and repeatable.
Reference Reading
- NIST SP 800-86 — Guide to Integrating Forensic Techniques into Incident Response
- NIST SP 800-101 Rev. 1 — Mobile Device Forensics
- NIST SP 800-61 Rev. 3 — Incident Response Recommendations
- NCSC — Technical response capabilities: logs and evidence
- MITRE ATT&CK Enterprise Knowledge Base
- NIST Cybersecurity Framework 2.0
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM