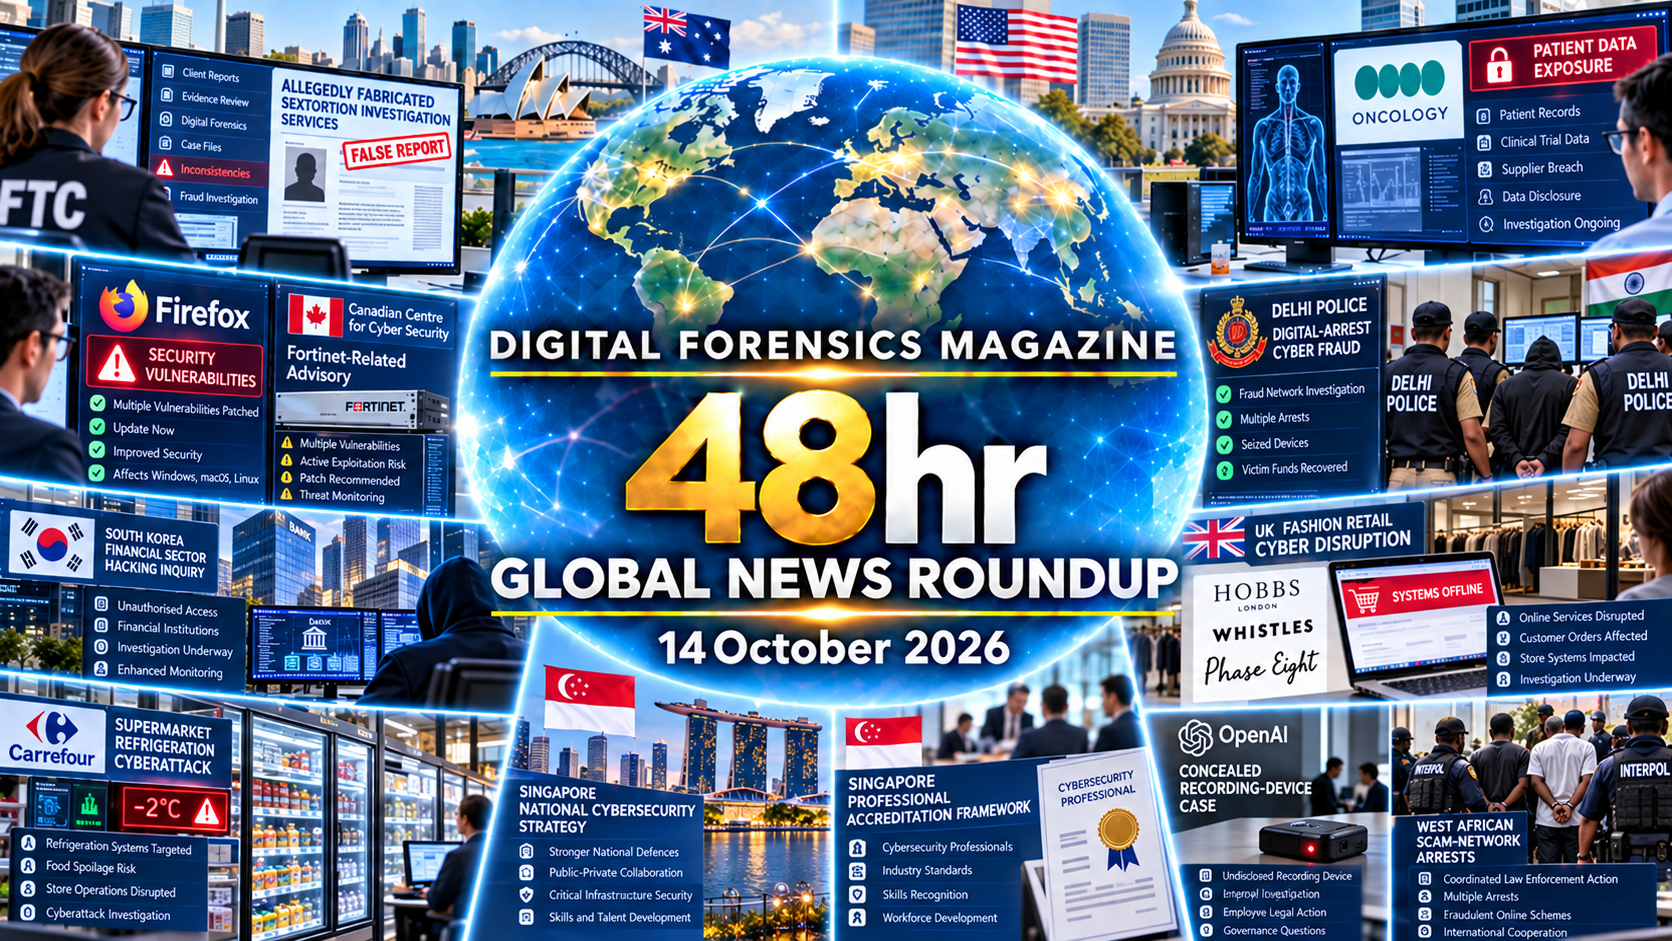

What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
Legal Aid Agency finds older stolen records
Confiant traces spyware delivery through ad infrastructure
→Cyber Investigations
Delhi police trace sextortion payments and phones
Researchers reconstruct malware network from two file hashes
→Major Cyber Incidents
CenterPoint breach notification reaches one million
US bankruptcy notice service halted after cyber incident
→Exploits & Threat Intelligence
BeyondTrust flaw linked to observed espionage intrusion
Cisco confirms Secure Email Gateway exploitation
→Law Enforcement
Singapore charges four after scam-proceeds tracing
Northern Ireland cybercrime enquiry leads to charges
→Policy & Standards
Ofcom details platform evidence and hash-matching duties
CISA adds exploited Atlassian flaw to federal catalogue
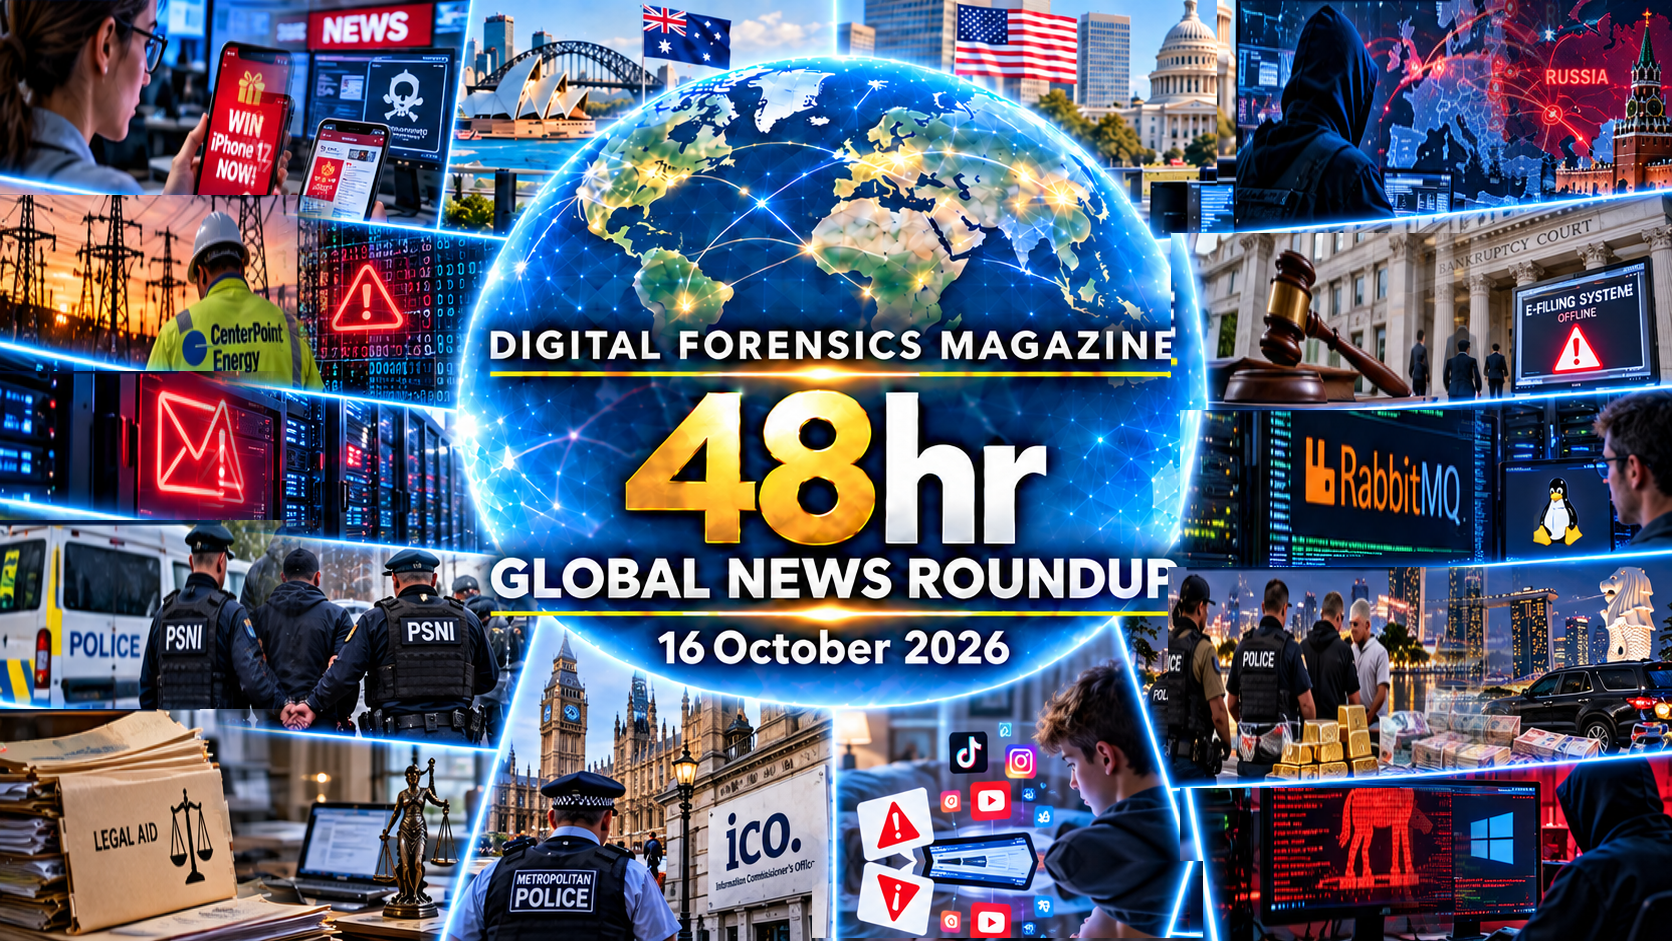
→The UK Legal Aid Agency reported on 14 October that continuing forensic analysis of its 2025 intrusion identified approximately 250,000 exfiltrated records predating 2007, some dating to 1978, and some probation information. Officials said the fragmented nature of the stolen material complicated reconstruction of its contents, stressed that historical contact with the justice system did not establish individual compromise, and reported no indication that the stolen information had been published or shared.
Confiant published technical findings on 15 October tracing Discover-Tech’s advertising scripts, delivery domains and hosting relationships to infrastructure identified in a joint spyware investigation with Citizen Lab researchers in Canada. The investigation correlated redirects, code fragments, certificates and domain records, while its partner independently documented targeted device infections, illustrating how investigators can reconstruct the delivery chain without treating widespread advertising exposure as evidence of infection on every reached device.
Delhi Police arrested four people in India after investigating an alleged WhatsApp sextortion scheme in which a complainant transferred approximately ₹14.6 lakh following threats from individuals impersonating police and platform representatives. Officers reportedly correlated mobile identifiers, telephone records, internet addresses and financial transactions across suspected beneficiary accounts, linked fifteen other complaints to the accounts under investigation, and seized phones and SIM cards for further examination of individual roles and payment trails.
ReversingLabs published a forensic reconstruction on 15 October showing how two previously disclosed malware hashes led analysts to a staging server, five related stager builds, two lure files and linked phishing infrastructure. The researchers compared sample relationships and historical telemetry to build a dated sequence beyond the originally published indicators, demonstrating a reproducible approach to infrastructure tracing while making clear that relationships between artefacts do not independently establish an operator’s identity.
Regional reporting on 14 October described a Texas attorney-general breach notice listing 1,062,060 individuals affected by an earlier cybersecurity incident at Houston-based CenterPoint Energy, while the company continued assessing whom it would notify. CenterPoint said electricity and gas delivery remained uninterrupted as advisers examined the personal information involved, distinguishing the reported customer data exposure from any evidence of compromised operational systems or independently verified claims of further unauthorised activity.
The Administrative Office of the United States Courts confirmed on 15 October that a cybersecurity incident at contractor BAE Systems had disabled the Bankruptcy Noticing Center, which prepares and distributes notices for federal bankruptcy courts nationwide. The judiciary said related websites and notice delivery remained unavailable while BAE investigated, creating documented gaps in court communications without establishing data theft, attacker attribution or compromise of the courts’ separate electronic filing systems.
Google Threat Intelligence Group disclosed on 15 October that investigators had observed exploitation of BeyondTrust Remote Support vulnerability CVE-2026-102764 during an August intrusion and attributed the activity to a suspected China-linked group it tracks as ARMORY CASTLE. Its technical account describes appliance log evidence, privilege escalation and deployment of the SAWFLY webshell and BARECLAW tunnelling tool, while distinguishing observed compromise from the possibility of wider exploitation after public disclosure.
Cisco published a critical security advisory on 14 October for CVE-2026-76519, a file-write vulnerability affecting the Advanced Malware Protection feature in Secure Email Gateway appliances, and acknowledged awareness of active exploitation. The notice identifies affected configurations and corrected software, giving administrators a basis for matching asset inventories to patch status, while forensic examinations must separately determine whether malicious attachments reached vulnerable installations or produced unauthorised file changes.
Singapore Police announced on 15 October that four men would face charges following a sixteen-hour investigation into the collection and laundering of cash, jewellery and gold allegedly obtained through transnational scams. Cyber Command and other units traced collection activity to two Malaysian and two Singaporean suspects and provisionally assessed at least S$300,000 in proceeds, with the allegations still subject to court examination and the financial trail requiring attribution to individual transactions.
Northern Ireland’s police announced on 15 October that a 21-year-old man had been charged after an investigation involving international law-enforcement partners into incidents dating from January, including alleged unauthorised computer access, blackmail and threatening communications. Police said the suspect was arrested again after earlier enquiries and was due to appear before Dungannon Magistrates’ Court, leaving the supporting electronic evidence and the allegations themselves to be tested through the criminal justice process.
The UK communications regulator Ofcom issued its October online safety bulletin on 15 October, outlining new compliance activity and expectations concerning illegal-content risk assessments, non-consensual intimate-image detection and transparency reports by categorised services. The bulletin emphasises records supporting service assessments and the use of hash matching or equivalent measures where required, creating identifiable evidence obligations for platforms without suggesting that every listed requirement is already in force.
The US Cybersecurity and Infrastructure Security Agency added Atlassian flaw CVE-2026-21589 to its Known Exploited Vulnerabilities catalogue on 15 October, citing evidence of exploitation and potential unauthorised access to files or directories. The agency linked the listing to risk-based federal remediation obligations under Binding Operational Directive 26-04, making the advisory a dated compliance and investigative reference without establishing victim numbers, intrusion methods or attacker attribution.
Editorial Perspective
Investigative certainty increasingly depends on identifying the original observation rather than repeating a conclusion drawn from it. Across online advertising infrastructure, court-notice systems, payment networks and breached records, apparently unrelated cases share a need to reconstruct provenance across several systems. Evidence must distinguish a confirmed compromise from a potential exposure, and an organisation’s attribution assessment from independently established identity. Reliable timelines depend on preserving the underlying logs, seized media and contemporaneous configuration records before the relevant context disappears.
The same discipline applies when regulators or police collect personal information for legitimate investigations. Teams need to document lawful access, the scope of each dataset, how records were acquired and whether analytical findings can be reproduced by another examiner. Technical advisories provide useful indicators and version boundaries, but they do not replace direct examination of the affected environment. More consistent evidence handling across public bodies, suppliers and international policing partners would make both operational decisions and eventual legal scrutiny more defensible.
Reference Reading
- NIST SP 800-86 — Guide to Integrating Forensic Techniques into Incident Response
- NIST SP 800-101 Rev. 1 — Guidelines on Mobile Device Forensics
- NIST SP 800-92 — Guide to Computer Security Log Management
- MITRE ATT&CK — Enterprise attack techniques and investigation mapping
- NIST SP 800-61 Rev. 3 — Incident Response Recommendations
- NIST Cybersecurity Framework 2.0 — risk governance and assurance
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM