
What’s in this roundup?
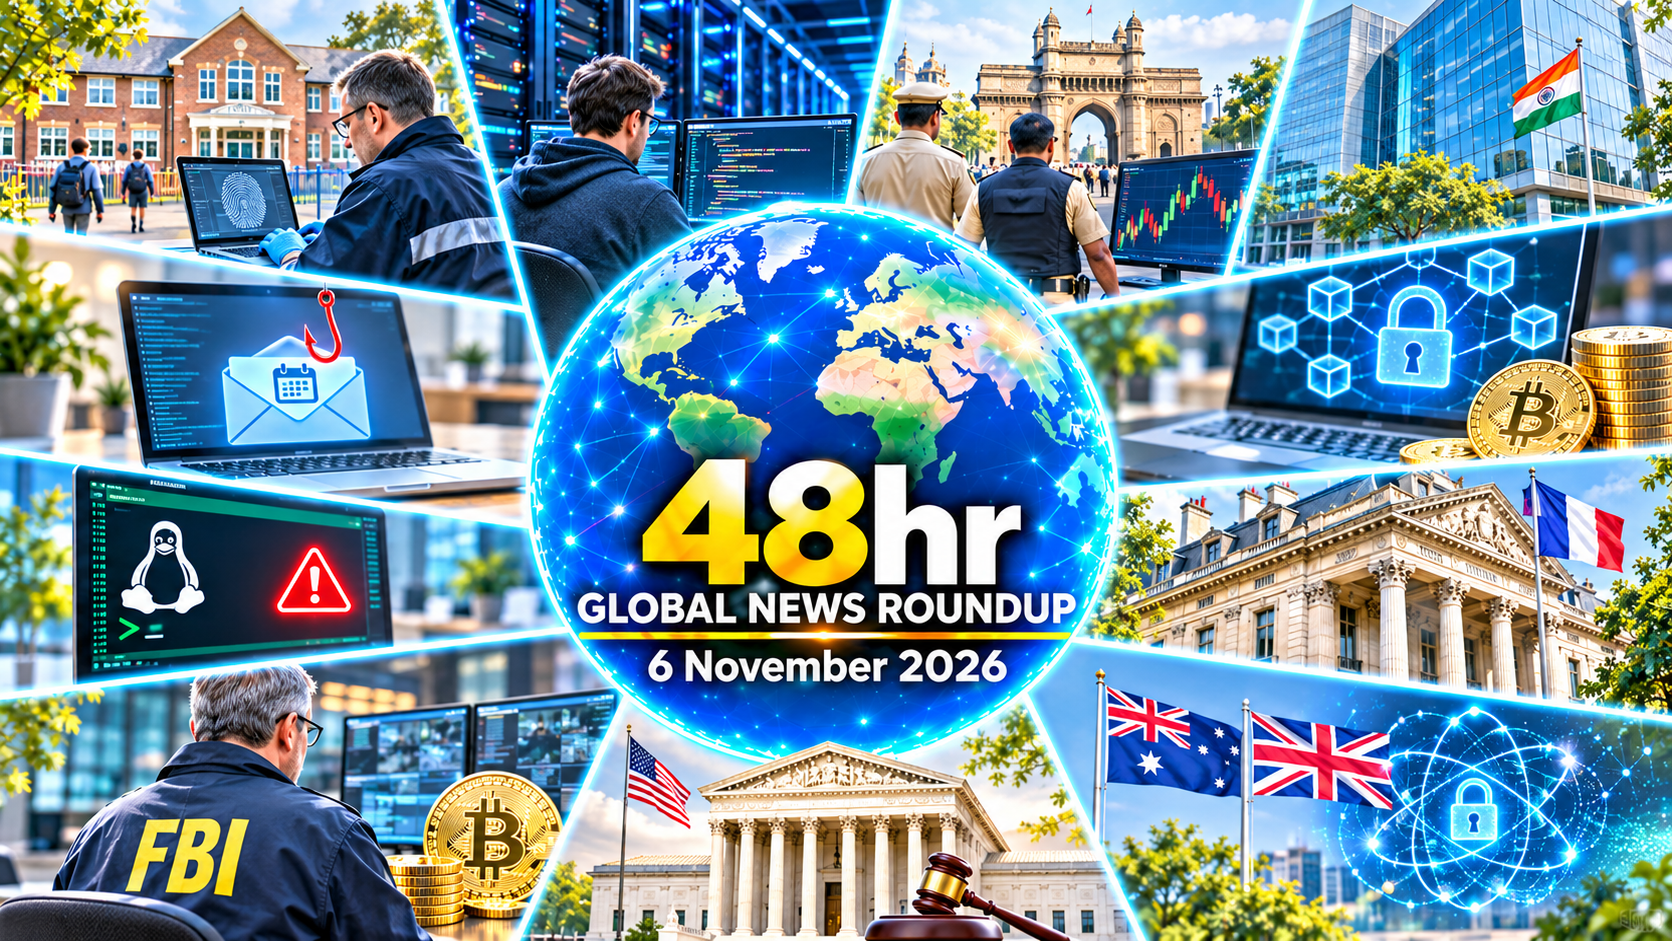
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
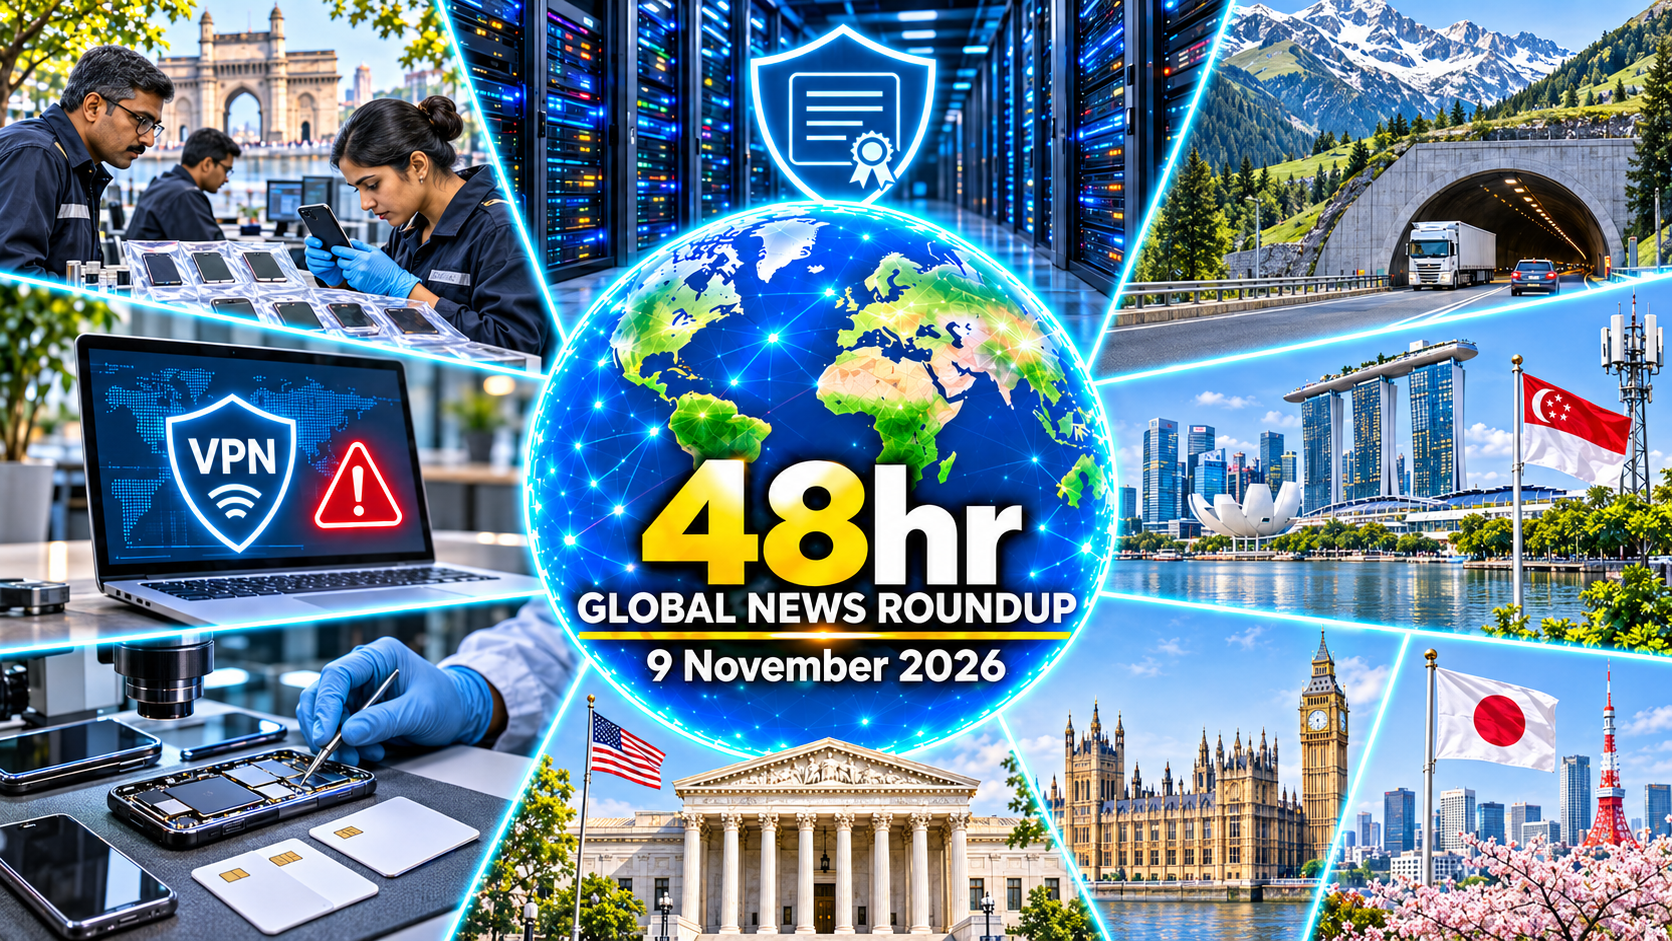
DigiCert closes breach audit actions
Mumbai examines seized phone evidence
→Cyber Investigations
Mumbai investigates police impersonation scam
Bogotá examines source of hoax email
→Major Cyber Incidents
Brenner tunnel operator confirms data access
Singapore telco discloses identity data breach
→Exploits & Threat Intelligence
SonicWall warns of VPN authentication bypass
AWS removes vulnerable deployment example
→Law Enforcement
Bihar police seize phones and cards
US arraigns suspect in access device case
→Policy & Standards
UK advances connected-device security labelling
Japan adopts emergency cybersecurity package
→DigiCert reported that it had finished auditing its US business system after unauthorised access to archived customer information, closing the last action in its public incident report. The company said retained logs and audit tables identified the account and access window, while separate certificate authority records showed that the account had performed no certificate issuance, revocation or validation actions.
Maharashtra Cyber police said they recovered suspected child sexual abuse material from a mobile phone examined in Mumbai after online monitoring led investigators to a suspect. The forensic examination is continuing to determine where the files originated, how they were downloaded and stored, and whether they were shared through online platforms or linked to other people.
Mumbai police are investigating an impersonation scam in which callers posing as Indian police and counterterrorism officers allegedly persuaded a woman to transfer around ₹1.9 crore. Investigators described a sequence spanning WhatsApp calls, instructions to use Signal and transfers to three bank accounts, with purported central bank letters used to make requests for payment appear official.
Authorities in Bogotá, Colombia, are investigating after a bomb hoax sent to a European airport appeared to come from a public hospital network in the city. A copy examined by The Record appeared to carry the network’s domain, but the available evidence leaves open whether the sender forged the address or gained access to an actual mailbox.
The company building the Brenner Base Tunnel between Austria and Italy confirmed that unauthorised parties accessed private data and said construction and operations had continued. It told ANSA that it isolated the affected systems, brought in external forensic specialists and alerted authorities, while the extent of access and the volume of data compromised remained undetermined in the account it gave ANSA.
Singapore telecommunications operator M1 disclosed a breach involving customer names, national identity or foreign identification numbers, dates of birth and contact details, saying services remained operational. The company said it had contained the breach and was working with authorities and outside specialists, while its disclosure identified the affected data categories without giving a customer count or identifying how the access occurred.
SonicWall issued a global advisory for CVE-2026-19868 after investigating a report of possible exploitation affecting the SSL VPN service on certain seventh and eighth generation firewalls. The flaw can allow someone holding valid credentials for a different login method to bypass SAML checks and potentially its multifactor authentication when SAML is enabled for VPN logins on the affected firewall.
Amazon Web Services removed a setup example from its global Trusted Remote Execution documentation after finding that it could introduce operating system command injection into customer deployments. The issue, CVE-2026-122193, affects Systems Manager documents created from the example, allowing someone already authorised to invoke such a document to pass crafted input and run commands outside the intended sandbox.
Police in East Champaran district in Bihar, India, arrested two people during a raid linked to a suspected mobile fraud scheme and seized two phones and five cash machine cards. Officers said their examination of the devices found WhatsApp messages and information about suspected illicit transactions, and they registered a case based on their enquiries.
A man was arraigned in Binghamton, New York, on charges including access device fraud and aggravated identity theft in a case involving Social Security payments to a deceased beneficiary. Federal prosecutors allege that he used an unauthorised cash machine card to make withdrawals over nearly six years and are seeking forfeiture of just under $110,000.
The UK published its statement on the London conference of the Global Cybersecurity Labelling Initiative, welcoming the European Union as a member and Japan as the next host. The initiative is working towards greater compatibility between security labels and standards for connected devices, and the meeting included industry input on putting those requirements and schemes into practice.
Japan adopted an emergency cybersecurity package that calls for stronger public and private sector information sharing, better investigative capacity and greater use of artificial intelligence to find vulnerabilities. The package sets out plans for a specialist testing team and earlier assessments of government systems, alongside measures to reduce the amount of personal information held by organisations.
Editorial Perspective
An account, a device and a network address each describe a different part of an event. Investigators need records that connect those layers, including the authentication method used, the permissions in force at the time and the action recorded by the target system. Preserving the original timestamps and recording clock offsets makes it possible to compare events across providers. Where only one layer is visible, the case record should say which links are still missing.
A defensible account of exposure separates the data present in a system, the data an account could reach and the data that logs show it accessed. Those distinctions shape the questions investigators can answer and the notices an organisation can support. Retention periods and supplier contracts determine whether the necessary records can still be obtained when an inquiry begins. Where investigators work from an export, retaining its original form and documenting any filtering or transformation lets another examiner test the same conclusions.
Reference Reading
- IETF RFC 3227 — Guidelines for Evidence Collection and Archiving
- IETF RFC 8601 — Email Authentication Results
- NIST SP 800-86 — Guide to Integrating Forensic Techniques into Incident Response
- NIST SP 800-92 — Guide to Computer Security Log Management
- NIST SP 1800-28 — Identifying and Protecting Assets Against Data Breaches
- ETSI EN 303 645 — Cyber Security for Consumer Internet of Things
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM