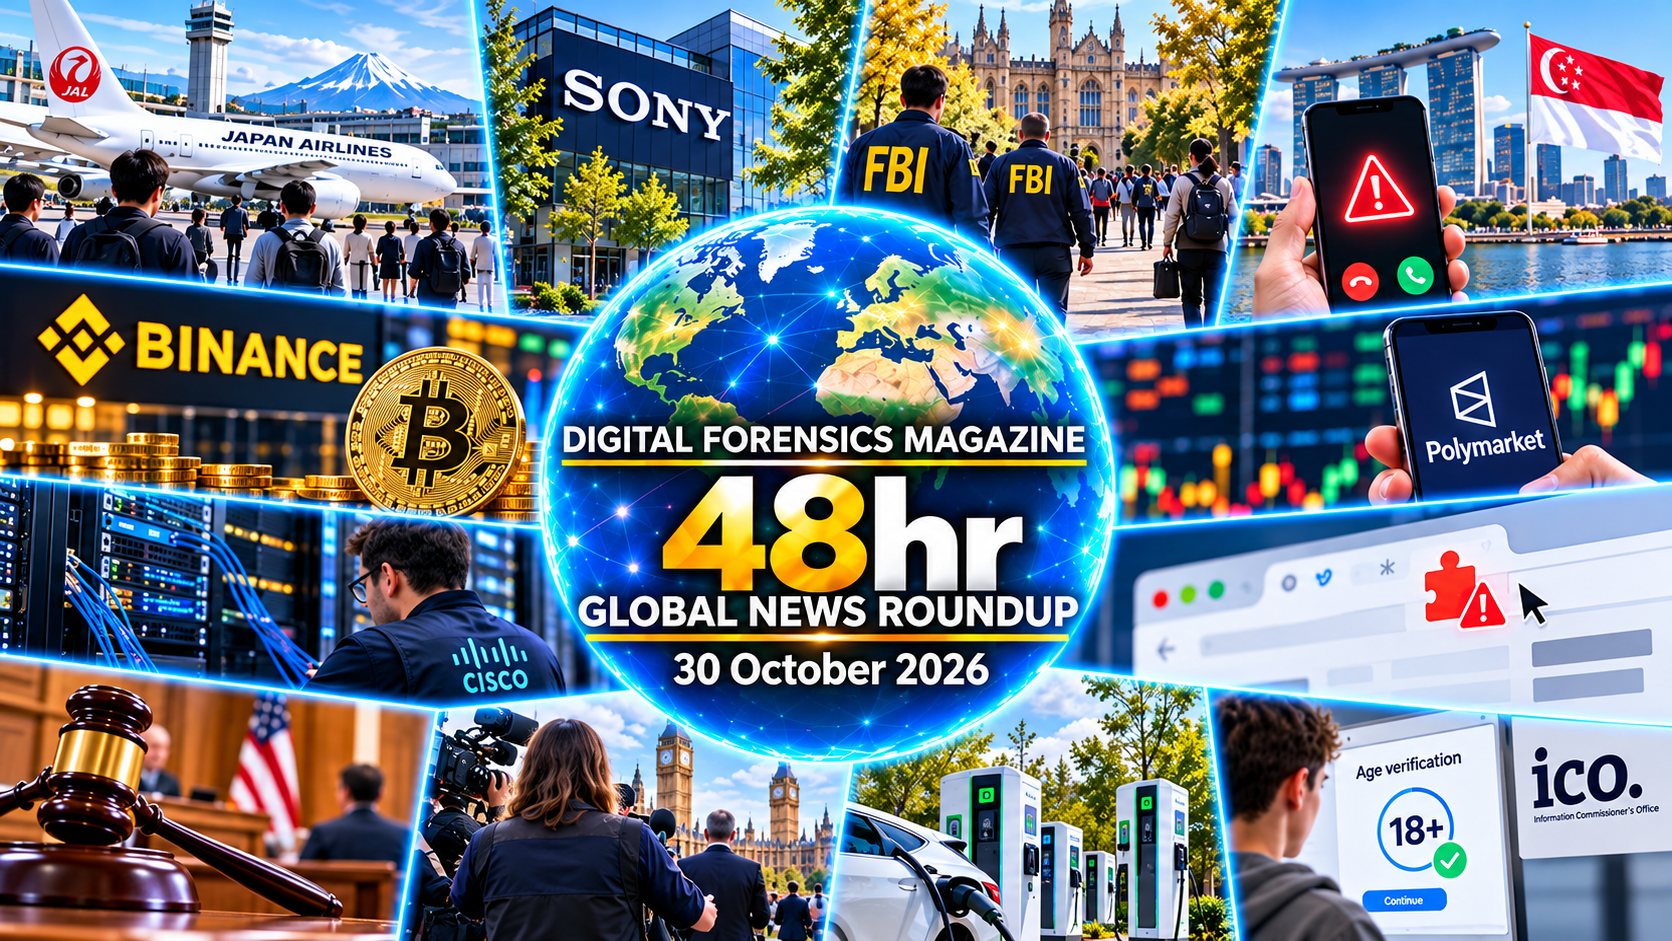

What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
Club Tourism identifies potential exposure of 4.32 million accounts
Applebee’s mobile application exposed a database credential
→Cyber Investigations
Mumbai investigates alleged sextortion and police impersonation
FBI attributes Binance theft to North Korean TraderTraitor group
→Major Cyber Incidents
Northflank expands credential rotation after hosting security incident
Japanese securities firm reports outsourced platform breach
→Exploits & Threat Intelligence
VOLTA infostealer uses AI to triage stolen information
Canonical documents certificate authentication bypass in LXD
→Law Enforcement
Delhi Police detail nationwide cyber-fraud enforcement operation
Kanpur police arrest suspect in impersonation fraud inquiry
→Policy & Standards
Singapore Police introduces verifiable outgoing caller identification
High Court upholds Ofcom’s online-safety information powers
→Japanese travel operator Club Tourism disclosed on 31 October that unauthorised access to its reservation infrastructure may have exposed approximately 4.32 million registered customer records, including names, contact information and emergency contacts. Its investigation separated the suspected disclosure from passwords, passport details and payment information, which it said were excluded, while the company’s containment measures and notifications leave the precise extent of external acquisition and subsequent misuse under examination.
US restaurant chain Applebee’s confirmed that it remediated a database exposure after independent researchers discovered an embedded credential inside its Android application that permitted access to customer records. The researchers reproduced access using test records and described names, contact details and other account fields, while the company said its investigation had found no evidence of unauthorised access and did not establish the total affected population or historical access-log completeness.
Mumbai East Cyber Police registered an investigation after a retired Indian resident alleged that online sextortionists obtained an intimate video and subsequently used threats and impersonated police identities to obtain payments totalling approximately ₹15.29 lakh. Investigators must correlate Facebook and WhatsApp accounts, video-call records, payment movements and purported official contacts to establish who operated each stage of the alleged scheme, without treating reported aliases as verified identities.
The US Federal Bureau of Investigation attributed the recent multibillion-dollar Binance cryptocurrency theft to the North Korean TraderTraitor operation in a new 31 October advisory, adding named wallet addresses and intelligence on laundering activity. Investigators reported movement of stolen assets into Ethereum and warned of possible further transfers through decentralised services, making the newly published addresses and transaction chronology materially different from earlier preliminary reports while attribution remains an official investigative assessment.
UK cloud platform Northflank expanded its security-incident response on 31 October by enabling secret rotation for additional database and infrastructure add-ons, after advising customers to treat stored environment variables as potentially compromised. The provider had also reported customer observations of unauthorised AI API-key usage, but its public status updates do not conclusively establish the initial intrusion mechanism or the number of affected deployments, making provider and customer audit records essential.
PhillipCapital Japan disclosed on 31 October that unauthorised access to an external contractor operating a digital-securities system had resulted in the leakage of customer information, while stating that unrelated company services were not involved. The firm said the contractor detected anomalous activity on 29 October and began examining the affected systems, leaving the precise customer scope and the division of evidential responsibility between the securities provider and its supplier important outstanding questions.
Research released around 31 October described VOLTA-AUTODOXER, Windows information-stealing malware that gathers browser credentials, tokens and financial artefacts before using commercial language models to construct and rank profiles of prospective victims. Cisco Talos researchers examined its internal profiling logic and fallback behaviour, but did not establish a verified infection count or the identities of its operators, so analysts should distinguish observed malware capabilities from evidence of deployment in specific environments.
Canonical published details of CVE-2026-112816 on 30 October, describing a certificate-validation weakness in affected LXD releases that could permit a remote attacker with a trusted client certificate to impersonate its owner and control cluster resources. Corrected versions were made available for supported release branches, while public vulnerability documentation establishes a plausible exploitation path rather than compromise of any particular host, which requires examination of access logs, certificates and administrative actions.
Delhi Police reported the results of Operation CyHawk 6.0 following coordinated actions across Indian states, saying officers arrested 944 suspects, registered 596 new criminal complaints and examined links to thousands of alleged online-fraud reports. The police account also lists seized phones, SIM cards and computer equipment, but the headline totals cover different procedural categories and must not be conflated with convictions or conclusive attribution of individual transactions to each person detained.
Police in Kanpur, India, arrested a Bihar resident on suspicion of receiving approximately ₹48 lakh diverted from a doctor during an alleged scam in which callers impersonated officers from national investigative agencies. Regional reporting described recovered mobile devices and analysis of transfers through bank accounts, providing potential means to connect the newly arrested suspect to other participants, although the alleged roles, transaction chains and criminal responsibility remain subject to investigation and court proceedings.
Singapore Police announced the introduction from 2 November of a single caller identification number for outbound official calls, accompanied by a government-branded follow-up message intended to reduce successful impersonation fraud. The initiative responds to documented losses from callers pretending to represent law enforcement, although caller display alone should not be considered conclusive authentication and the accompanying official verification channels remain critical for preserving trustworthy contact records and distinguishing fraudulent approaches.
A UK High Court judgment issued on 30 October rejected legal challenges brought by Meta, X and TikTok against information notices issued by Ofcom under the Online Safety Act, confirming the regulator’s ability to demand material relevant to its statutory functions. The decision concerns information-gathering powers rather than a finding that the platforms breached substantive safety duties, and reinforces requirements for reliable platform metrics and preserved regulatory evidence.
Editorial Perspective
The strongest common thread across these investigations is the need to distinguish what a system could expose from what evidence demonstrates an intruder actually obtained. Application code, supplier audit logs, payment records and device extractions capture different stages of activity and often have different custodians. Investigators should establish collection dates, integrity checks, account provenance and relevant retention policies before treating those datasets as a coherent chronology. Vendor incident estimates and reported police totals remain hypotheses or administrative measures until supported by reproducible records.
The cases also illustrate how routine infrastructure can become a key evidential dependency, from third-party hosting to authenticated caller displays and cloud certificates. Effective forensic preparation requires access to historical configurations, identity mappings and transaction trails before those records expire. Investigative conclusions should separate demonstrated access, suspected exfiltration and proven misuse rather than collapse them into a single description of compromise. Clear evidential boundaries will matter as both criminal courts and regulators test competing accounts of security events.
Reference Reading
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM