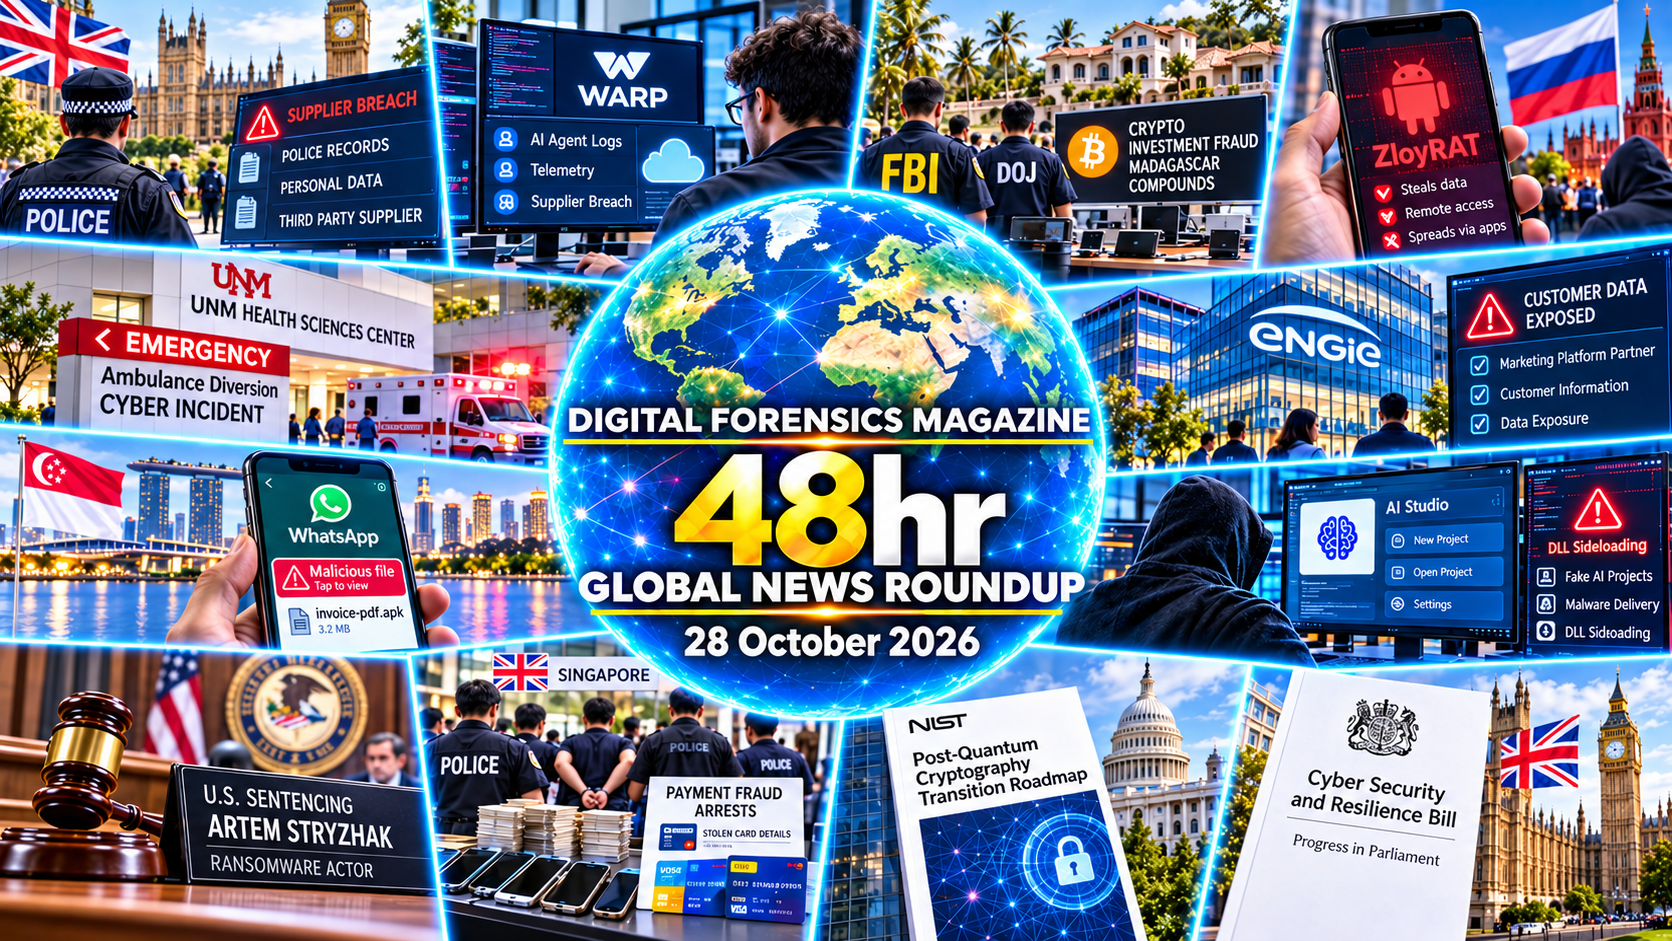

What’s in this roundup?
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
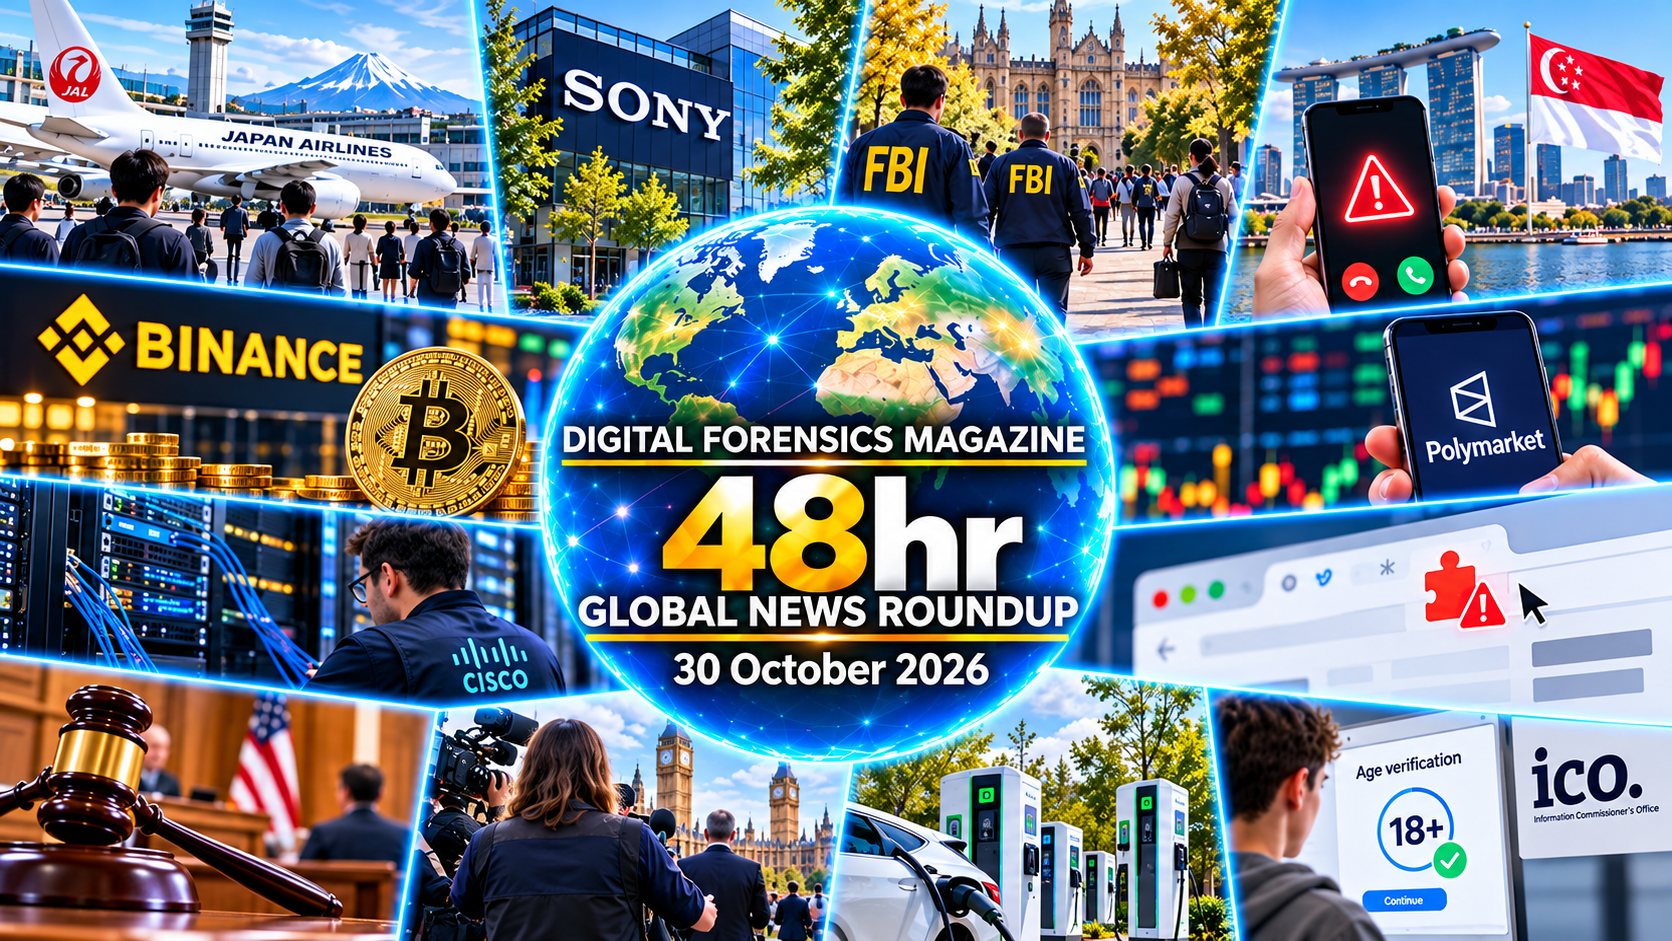
Japan Airlines identifies exposure of 92,000 reservations
Sony ISP breach reveals separate password exposure
→Cyber Investigations
US indictments trace alleged ghost-student fraud network
Singapore maps impersonation calls and payment demands
→Major Cyber Incidents
Binance reports multibillion-dollar security investigation
Polymarket halts trading after supplier compromise
→Exploits & Threat Intelligence
Cisco Talos traces KeyDrift implants in SD-WAN systems
Researchers identify widespread browser search hijacking
→Law Enforcement
US court sentences Syrian hacking conspirator
UK jury convicts over online harassment of journalists
→Policy & Standards
UK consults on security baseline for public EV chargers
UK regulator highlights privacy safeguards in age assurance
→Japan Airlines disclosed in Japan that traces of unauthorised access at its Amadeus reservation-system supplier involved records associated with approximately 92,000 passengers, including a smaller group whose passport and contact information may have been viewed. The airline said payment-card numbers and passwords were not exposed, while the supplier evidence spans several years and requires careful separation of observed external access from any confirmed subsequent misuse of individual travel records.
Japanese internet provider Sony Network Communications disclosed that unauthorised access to its So-net membership database exposed more than 2.5 million records, with separate findings concerning thousands of email-service passwords and a limited number of banking details. Its reported timeline distinguishes initial intrusion, discovery, containment and password resets, while the publicly described evidence does not establish the intrusion method or whether the stolen credentials were subsequently used against other accounts.
US federal prosecutors announced indictments arising from Operation Ghostbusters, an investigation alleging that stolen identities were used to establish fraudulent student-aid accounts and divert university grant and loan refunds through controlled bank accounts. The charges describe a network with alleged connections to Kenya and domestic money mules, but individual responsibility remains to be determined in court through linked applications, identity evidence, transactions and communications rather than scale of the alleged scheme.
Singapore Police warned that callers impersonating telecommunications provider SIMBA and government officials were linked to at least 59 reported cases during October, with reported losses of at least S$1.3 million. The described sequence moved victims between supposed customer-service and official investigators before demanding transfers or valuables, giving investigators a pattern to test against call records, bank transfers and reported contacts without assuming that every linked telephone identity belongs to an offender.
Cryptocurrency exchange Binance reported a security incident affecting an estimated US$6.3 billion in assets, saying preliminary examination suggested a compromised engineer laptop may have enabled unauthorised withdrawals through a service container. The exchange said approximately US$3 billion had been frozen on-chain and reported no evidence of leaked wallet private keys, but its proposed entry path and loss estimates remain subject to further examination, blockchain tracing and a promised technical account of the intrusion.
Prediction-market platform Polymarket temporarily halted trading on its international service on 29 October after identifying a security incident involving a compromised third-party provider, later reporting that the immediate issue was fixed. The platform said it had referred the matter to law enforcement and would reimburse affected users, while independently reported wallet losses and the supplier attack mechanism require separate verification through transaction traces, injected-script evidence and the provider’s investigation.
Cisco Talos published forensic findings showing that a cluster it tracks as UAT-11473 exploited an authentication-bypass weakness in Cisco Catalyst SD-WAN controllers to establish the KeyDrift malware framework in targeted networks. Researchers described implanted services, recovered binary behaviour and infrastructure overlaps with other covert activity, but their assessment of overlapping infrastructure should not be treated as definitive operator attribution; the reported artefacts provide testable indicators for examining affected devices and configuration histories.
Software supply-chain researchers at Socket reported 319 browser extensions with approximately 13.4 million combined installations that redirected searches through intermediary servers and supported advertising-referral revenue schemes. The new investigation added 264 extensions to earlier findings and described how apparently routine PDF, manual and search utilities altered browser behaviour, although installation counts do not by themselves measure active victims or prove theft of credentials beyond the documented collection and redirection of queries.
A United States federal court sentenced Ahmad Umar Agha to 42 months in prison following proceedings concerning a hacking conspiracy linked by prosecutors to the former Syrian government and attacks on media organisations and other targets. Justice Department accounts describe the defendant’s role in a longer-running campaign, underscoring the evidential importance of associating intrusions, communications and specific conduct with a named individual rather than relying on broader geopolitical assessments of the operation.
A jury at Southwark Crown Court in England convicted Stephen Lennon on 28 October of two counts of harassment causing fear of violence arising from conduct directed towards journalists through social media and telephone communications. The Crown Prosecution Service said the case involved direct and indirect targeting and publication of family images, demonstrating the need to preserve attributable posts, communications context and corroborating evidence while distinguishing the verdict from a future sentencing decision.
The UK Department for Transport launched a consultation on 29 October proposing baseline cyber security requirements for public electric-vehicle charging points sold or installed in Great Britain, including reference to ETSI EN 303 645. Officials also proposed physical tamper protection and a possible alternative route using EN 18031, while the measures remain proposals rather than current obligations and could shape future expectations for device logging, integrity verification and investigations involving charging infrastructure.
The UK Information Commissioner’s Office issued a statement on 29 October concerning highly effective age assurance, welcoming Ofcom’s assessment while emphasising personal-data protection and information rights in emerging online age-checking measures. The regulator said it was working with government and Ofcom as rules develop, making evidence of proportionality, retention, access controls and reliable assessment particularly relevant where identity or age-verification systems handle sensitive records about children and platform users.
Editorial Perspective
Across the current investigations, digital records held by third parties repeatedly determine whether a claim can be substantiated. Passenger reservations, hosted trading scripts, credential stores and outsourced infrastructure each have separate custodians and retention practices. Investigators need precise acquisition times, provenance and access histories before correlating these records. A published estimate of exposure or loss must remain distinguishable from evidence of an individual transaction, accessed account or compromised device.
The enforcement and technical reports also emphasise the limits of attribution by association. Shared infrastructure, recurring fraud scripts and similar malware behaviours can generate useful hypotheses without identifying a particular operator. Preserved endpoint artefacts, transaction chains, communications and witness accounts are needed to build reproducible evidential links. Policy discussions on connected equipment and identity verification make those requirements increasingly important before disputes or incidents arise.
Reference Reading
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM