
What’s in this roundup?
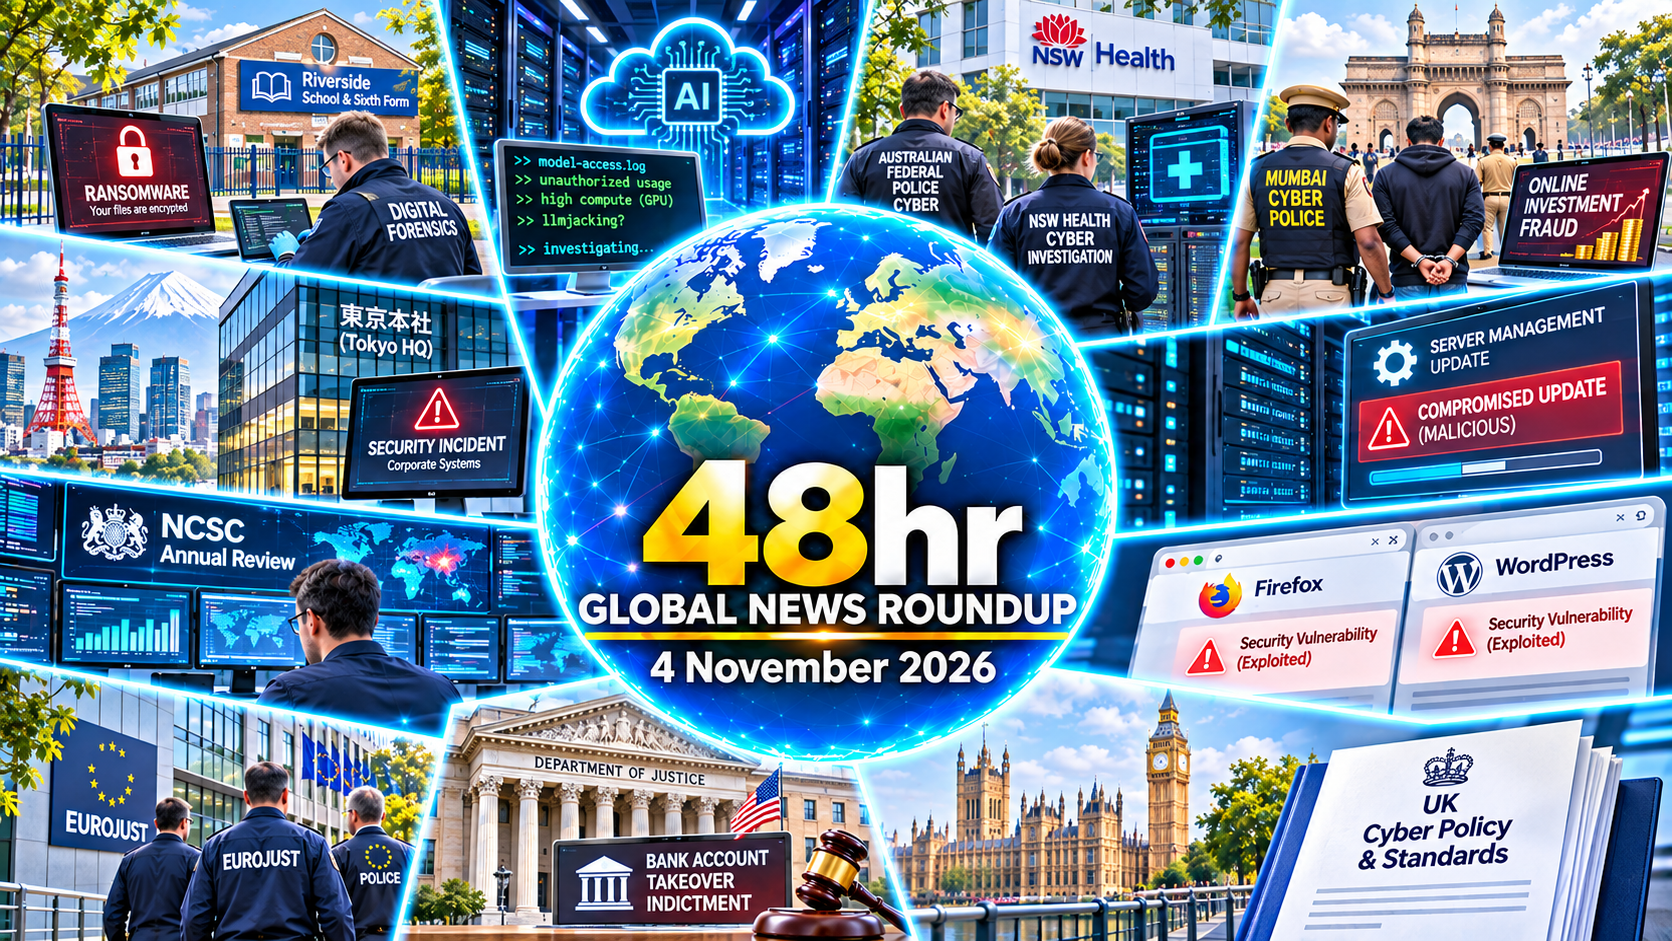
Both headline highlights from each existing section. Select a section to open it.
Digital Investigations
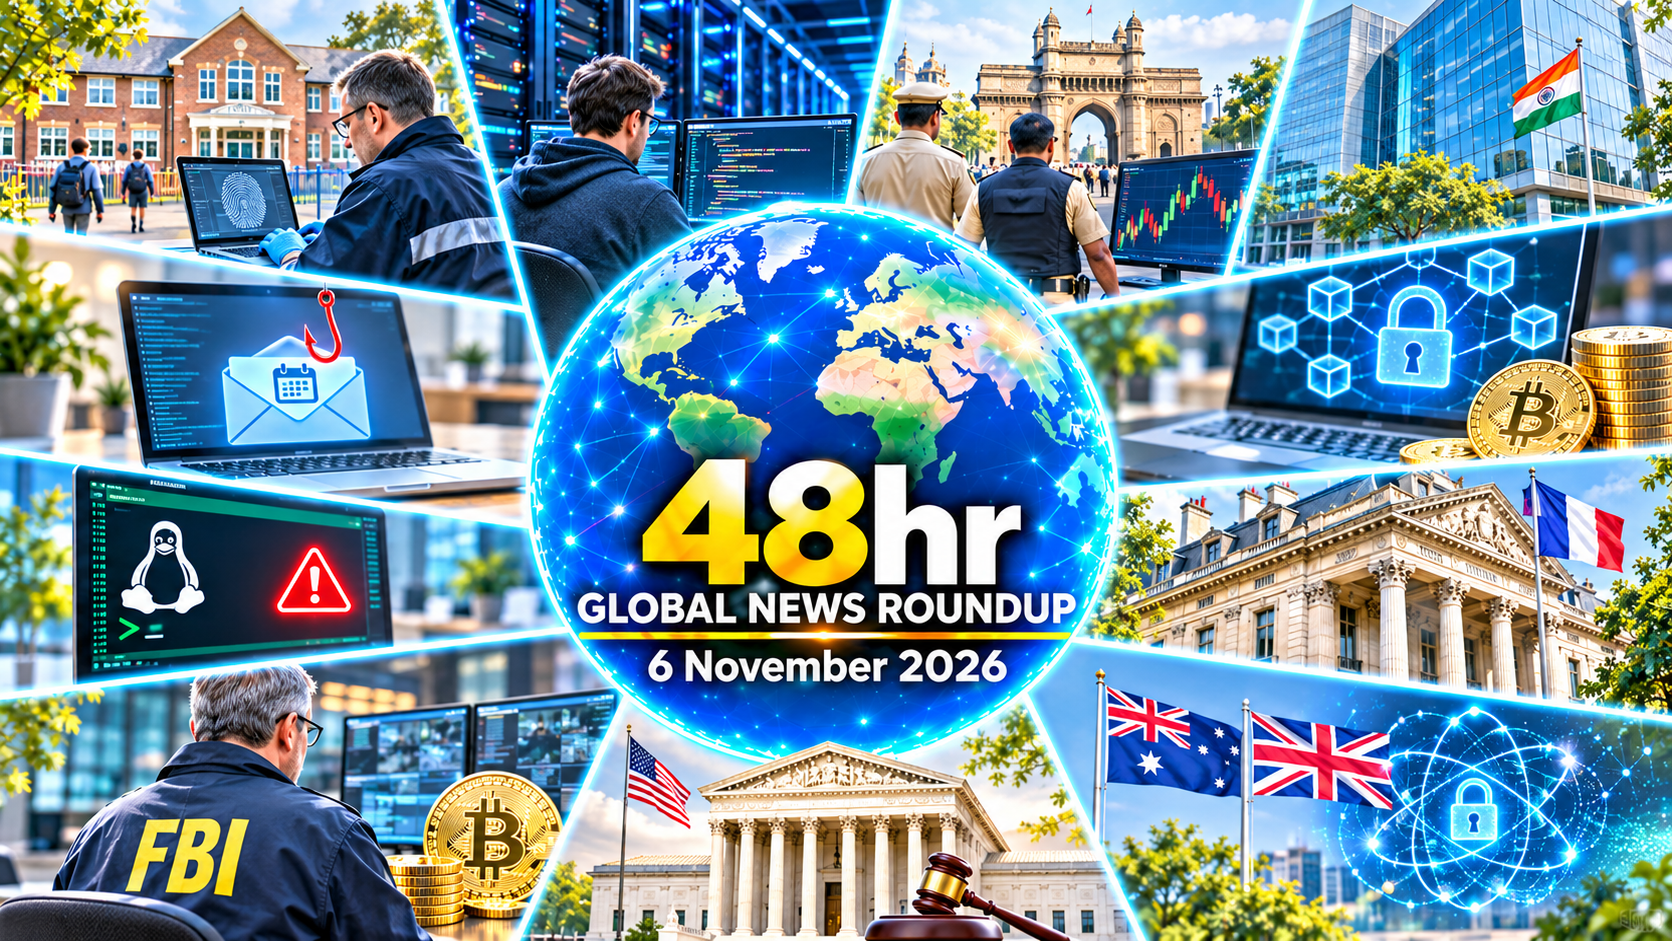
Bristol school file leak prompts forensic review
BO Team compromise reconstructed across supplier systems
→Cyber Investigations
Mumbai police trace unauthorised trading activity
Indian authorities warn of attacks against financial firms
→Major Cyber Incidents
Chainalysis expands scope of credential exposure
French bank investigates substantial fraudulent transfers
→Exploits & Threat Intelligence
Alpine Linux details OpenSSH authentication bypass
Fake AI events combine two phishing services
→Law Enforcement
US charges three in alleged international company fraud
Former FBI agent admits cryptocurrency theft
→Policy & Standards
Australia updates post-quantum supplier guidance
UK statistics show rising supply-chain cyber concern
→Bristol City Council confirmed on 4 November that files stolen from its Trading with Schools network had been published online, with investigators examining records associated with 39 schools in England. The council and police are reviewing the material to identify affected people and data categories, while the reported file count does not establish how many individuals were compromised or whether every file contains personal information.
Kaspersky investigators published a forensic reconstruction of an intrusion affecting a software developer’s infrastructure, documenting the compromise of servers, directory services, mail systems and deployment tooling during an earlier campaign. Their investigation identified suspicious SMB connections, recovered commands associated with the BO Team threat group and traced initial access to an internet-accessible Linux terminal server, illustrating why interconnected administration systems and preserved event logs are essential to determining the intrusion’s scope.
Mumbai police described an investigation into unauthorised access to an Indian investor’s demat account, alleging that a suspect sold shares worth approximately ₹4.58 crore before purchasing speculative securities. Regional reporting says investigators examined the account credentials, email-delivered one-time passwords and a linked SIM card, while the freezing of shares worth more than ₹2.86 crore represents a documented preservation measure rather than proof of every alleged transaction or participant’s criminal responsibility.
India’s CERT-In published an updated advisory on 4 November describing an evolving campaign against non-bank lenders, payment providers and cryptocurrency businesses, tracked by the agency as Crafty Falcon. The advisory links reported incidents to abuse of payment and disbursement interfaces and the suspected use of automated security tools, but its threat-actor description is an official assessment rather than independently established state attribution, and it does not confirm a comprehensive victim count.
Blockchain analysis company Chainalysis said that its continuing intrusion investigation had identified exposure of usernames, password hashes and live tokens affecting all users, substantially expanding an earlier disclosure. The company reported disruption to screening and investigative tools and possible access to some customer accounts, while saying it had no evidence that investigations datasets were accessed or attribution records manipulated; the number of individual users and precise intrusion method remain unconfirmed.
French lender Crédit Mutuel Arkéa confirmed on 4 November that unauthorised transactions had been initiated using a bank account, prompting a criminal investigation and precautionary transfer restrictions in France. The company said customer assets were unaffected and described the loss only by order of magnitude rather than confirming a final amount, leaving the initial access mechanism, recovery position and transaction chain for investigators to establish from financial and technical records.
Alpine Linux published a security advisory on 5 November describing a password authentication bypass affecting certain OpenSSH configurations built with the musl library and without active PAM checks. Exploitation requires password authentication to be enabled, a passwordless account marked with an asterisk and another locally hashed password, so the advisory recommends installing fixed packages and restarting the daemon while checking authentication records rather than assuming every exposed SSH service has been compromised.
Push Security researchers analysed fraudulent event invitations impersonating technology companies and found that the operators combined Kali365 device-code phishing with VoidProxy authentication interception to target Microsoft and Google accounts. Observed landing pages, redirect chains, collection infrastructure and browser telemetry support the reconstruction, although shared criminal services do not establish that their developers operated the campaign; the report provides investigators with concrete domains and session-capture indicators to test against enterprise access records.
US federal prosecutors unsealed charges against three foreign nationals accused of participating in a scheme to defraud companies worldwide using what the indictment calls super intelligence, with alleged losses exceeding $100 million. Authorities said arrests had occurred in Spain and the United Kingdom and extradition requests were pending, but the indictment remains an allegation; investigators and courts must distinguish claimed technological methods, documented money flows and each defendant’s responsibility.
A former FBI agent pleaded guilty in Virginia to wire fraud and money laundering after misusing access to cryptocurrency credentials collected during federal investigations, according to US prosecutors. Court records describe theft involving investigated wallets and an FBI-controlled operational wallet, with authorities stating that multiple investigations and sensitive methods were affected; the case underscores the evidential importance of privileged-access records, segregation of duties and independently verified transaction histories.
The Australian Cyber Security Centre updated its guidance on questions organisations should ask technology suppliers when assessing post-quantum cryptography readiness, working alongside cyber agencies in the United States. The document is planning guidance rather than an immediate migration mandate, and directs attention towards cryptographic dependencies, vendor roadmaps and lifecycle assurances that organisations may need to document as future systems and archived evidence remain exposed to changing cryptographic risks.
The UK Office for National Statistics reported that 21 per cent of businesses with ten or more employees were concerned about cyberattacks affecting supply chains over the next year, based on October surveys. The figure reflects expectations rather than measured attack incidence, rising from the previous month, and indicates perceived third-party risk while leaving incident counts, evidential collection practices and individual organisational exposures to separate assessment.
Editorial Perspective
The latest investigations illustrate why an initial account of an intrusion rarely captures its evidential scope. Access logs, administrative identities and archived credentials can reveal entirely different conclusions as investigators correlate technical records with supplier and customer statements. Forensic readiness requires preserved configuration histories and defensible timestamps, particularly where migration decisions or delegated privileges alter the systems exposed to unauthorised activity. Claims about automated or artificial-intelligence-enabled attacks should remain separate from directly observed commands, transactions and authenticated sessions.
Evidence ownership becomes more complex when investigations span certificate services, financial platforms, outsourced infrastructure and operational technology. Investigators need to establish which party retained the relevant logs, how reliably records identify individuals and whether later remediation has overwritten the earliest indicators. Regulators and courts are likely to place greater weight on demonstrable provenance, repeatable analysis and explicit limits of attribution than on estimates of severity. Long-term cryptographic planning also matters where preserved electronic evidence must remain authentic and verifiable well beyond the lifetime of current systems.
Reference Reading
Share this roundup
Advertisements
Latest Issue
Student Discount

Briefing Centre
Advertise With DFM